Stored DOM XSS | Practitioner
Really took a long time with this one due to not knowing enuf JS syntax
Upon closer inspection of the source, the comment body seems to be added into an innerHTML sink for display, which is a huge red flag opening up to Stored XSS payloads.
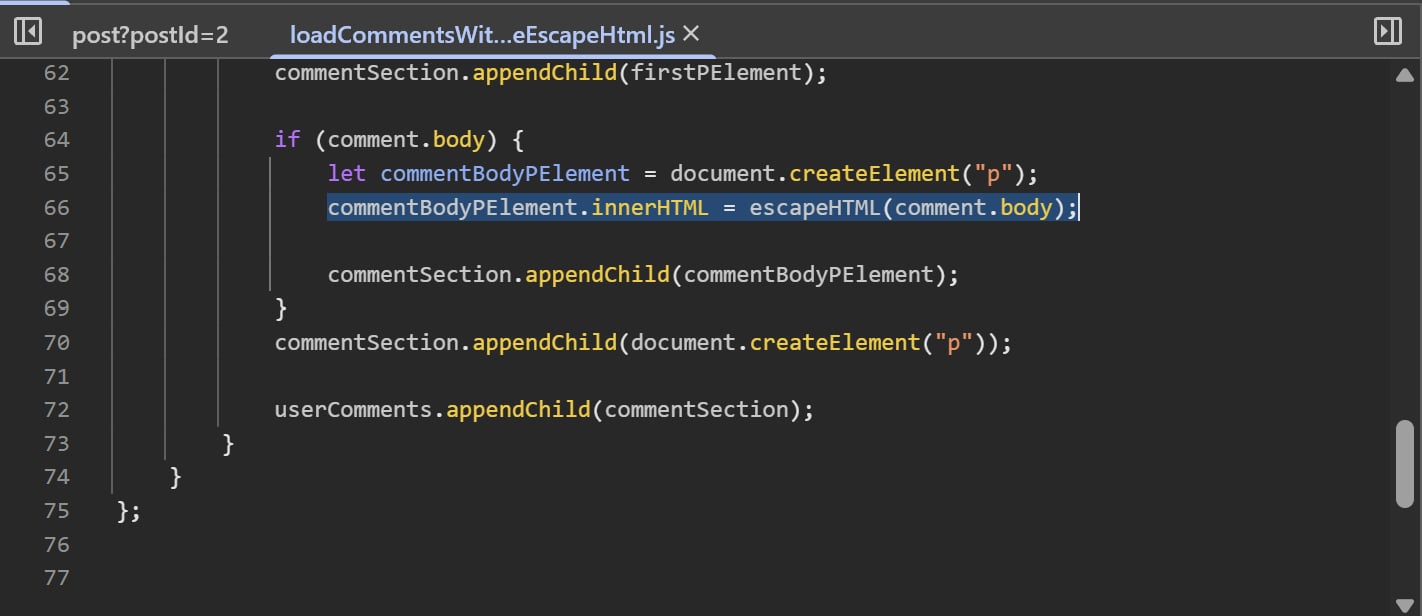 There is a peculiar custom function
escapeHTML() which does as it says on the tin. It filters out < and >, effectively blocking most XSS payloads, at least in theory.
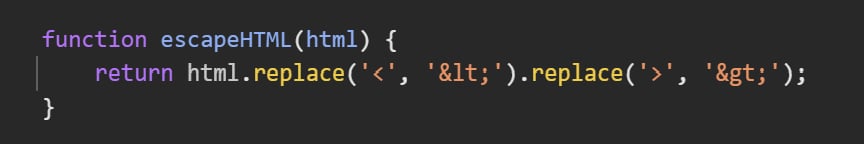 This only encodes the first occurences of those two brackets, which mean our payload can simply be:
<><img src=1 onerror=alert(1)>
The first two angle brackets will be encoded, but any subsequent angle brackets will be unaffected.