Reflected XSS into a JavaScript string with angle brackets and double quotes HTML-encoded and single quotes escaped | Practitioner
As usual, we first try to insert our canary string along with special characters to see what sticks:
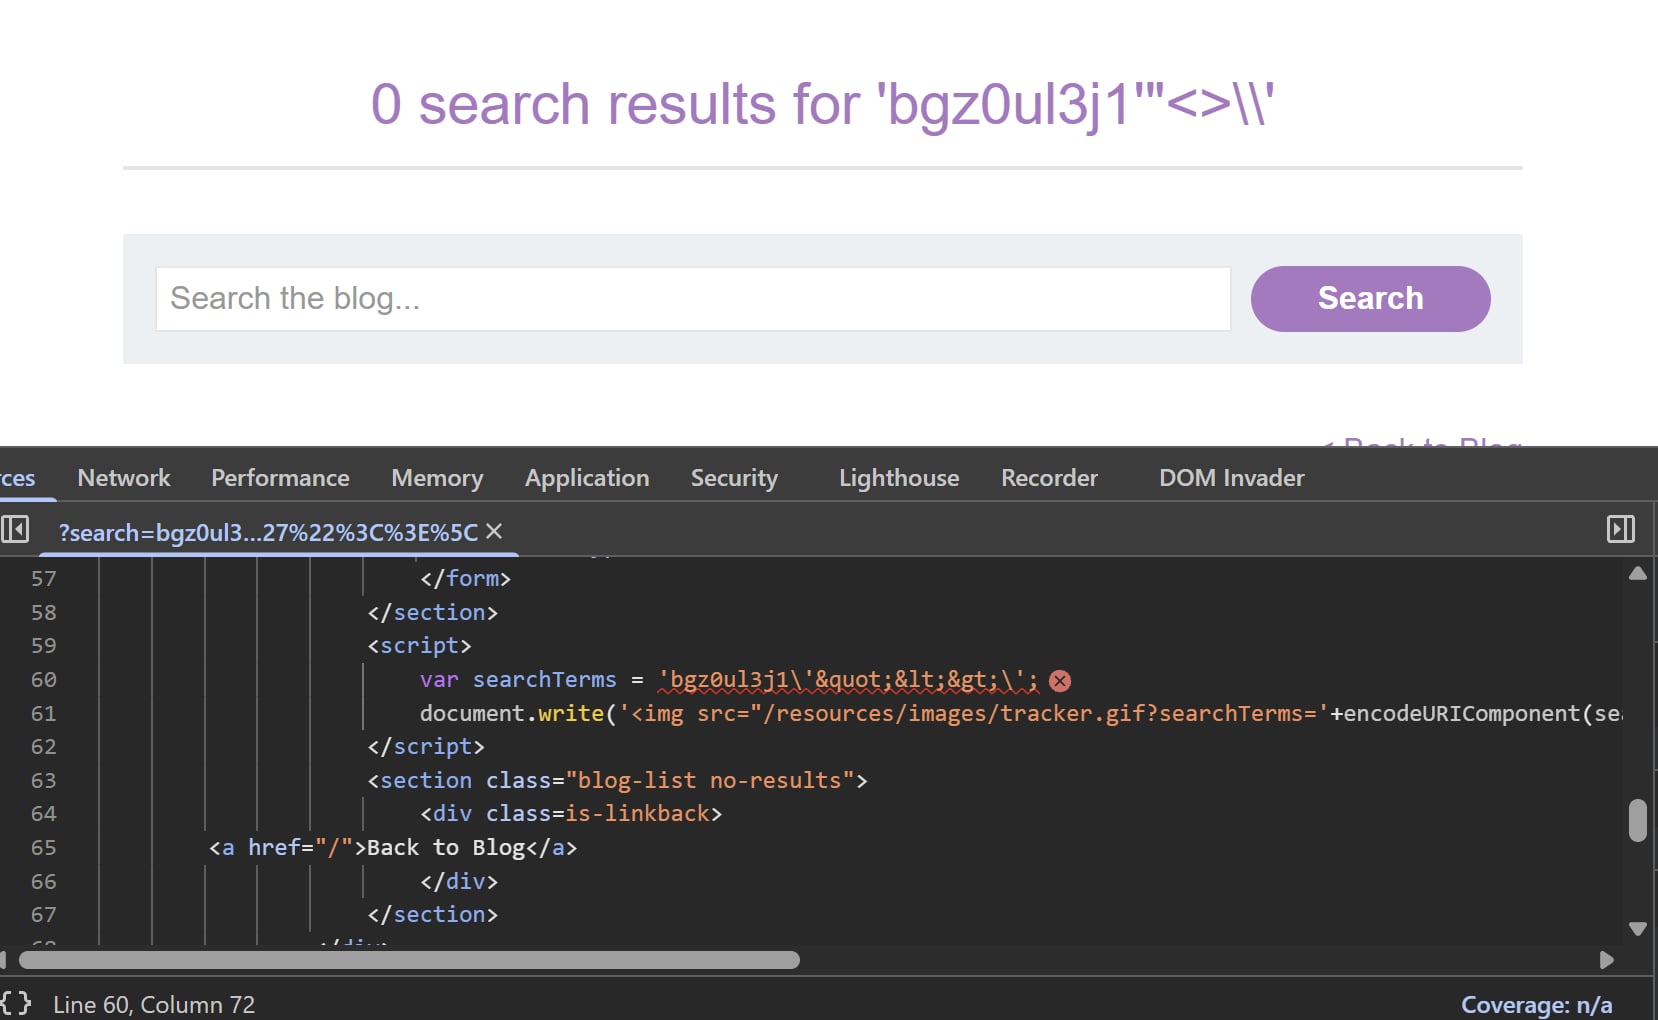
Notice all of the characters are encoded, save for one trailing backslash at the end. Since single quotes are escaped, we should expect the same for backslashes and see two of them rather than one. This means backslashes are not escaped, and we can use this to our advantage.
We can insert our own backslash character before a single quote to neutralize the backslash that is added by the application.
This means, suppose this input:
';alert(document.domain)//
is converted to:
\';alert(document.domain)//
We can use this alternative payload:
\';alert(document.domain)//
that gets converted to:
\\';alert(document.domain)//
Here, the first backslash means that the second backslash is interpreted literally, and not as a special character. This means that the quote is now interpreted as a string terminator, and so the attack succeeds.