DOM XSS in document.write sink using source location.search inside a select element | Practitioner
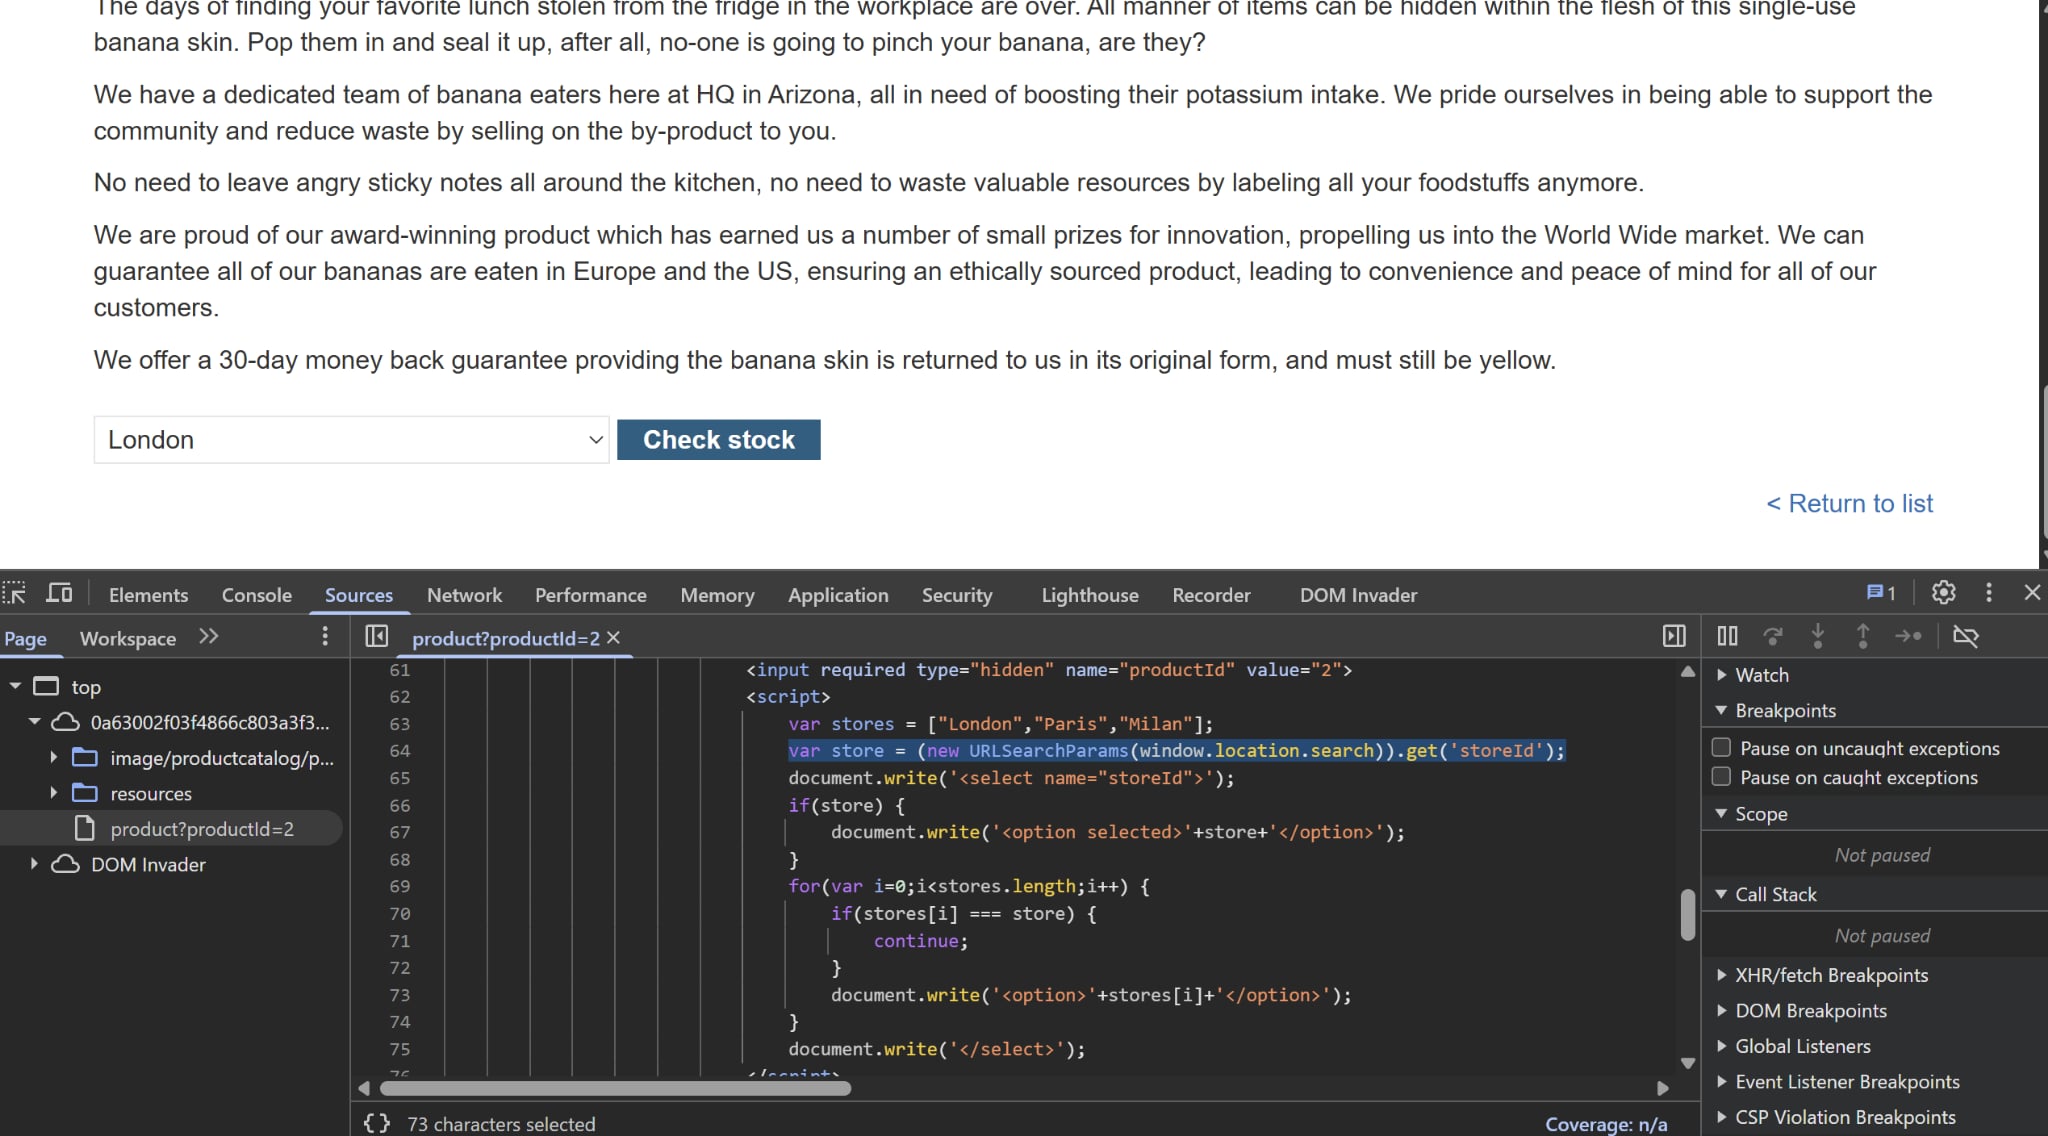 Upon viewing the source, we see that this script has a
document.write() sink that writes out the select form in the HTML. It queries for the value of storeId param and attaches it to an <option> tag as shown.
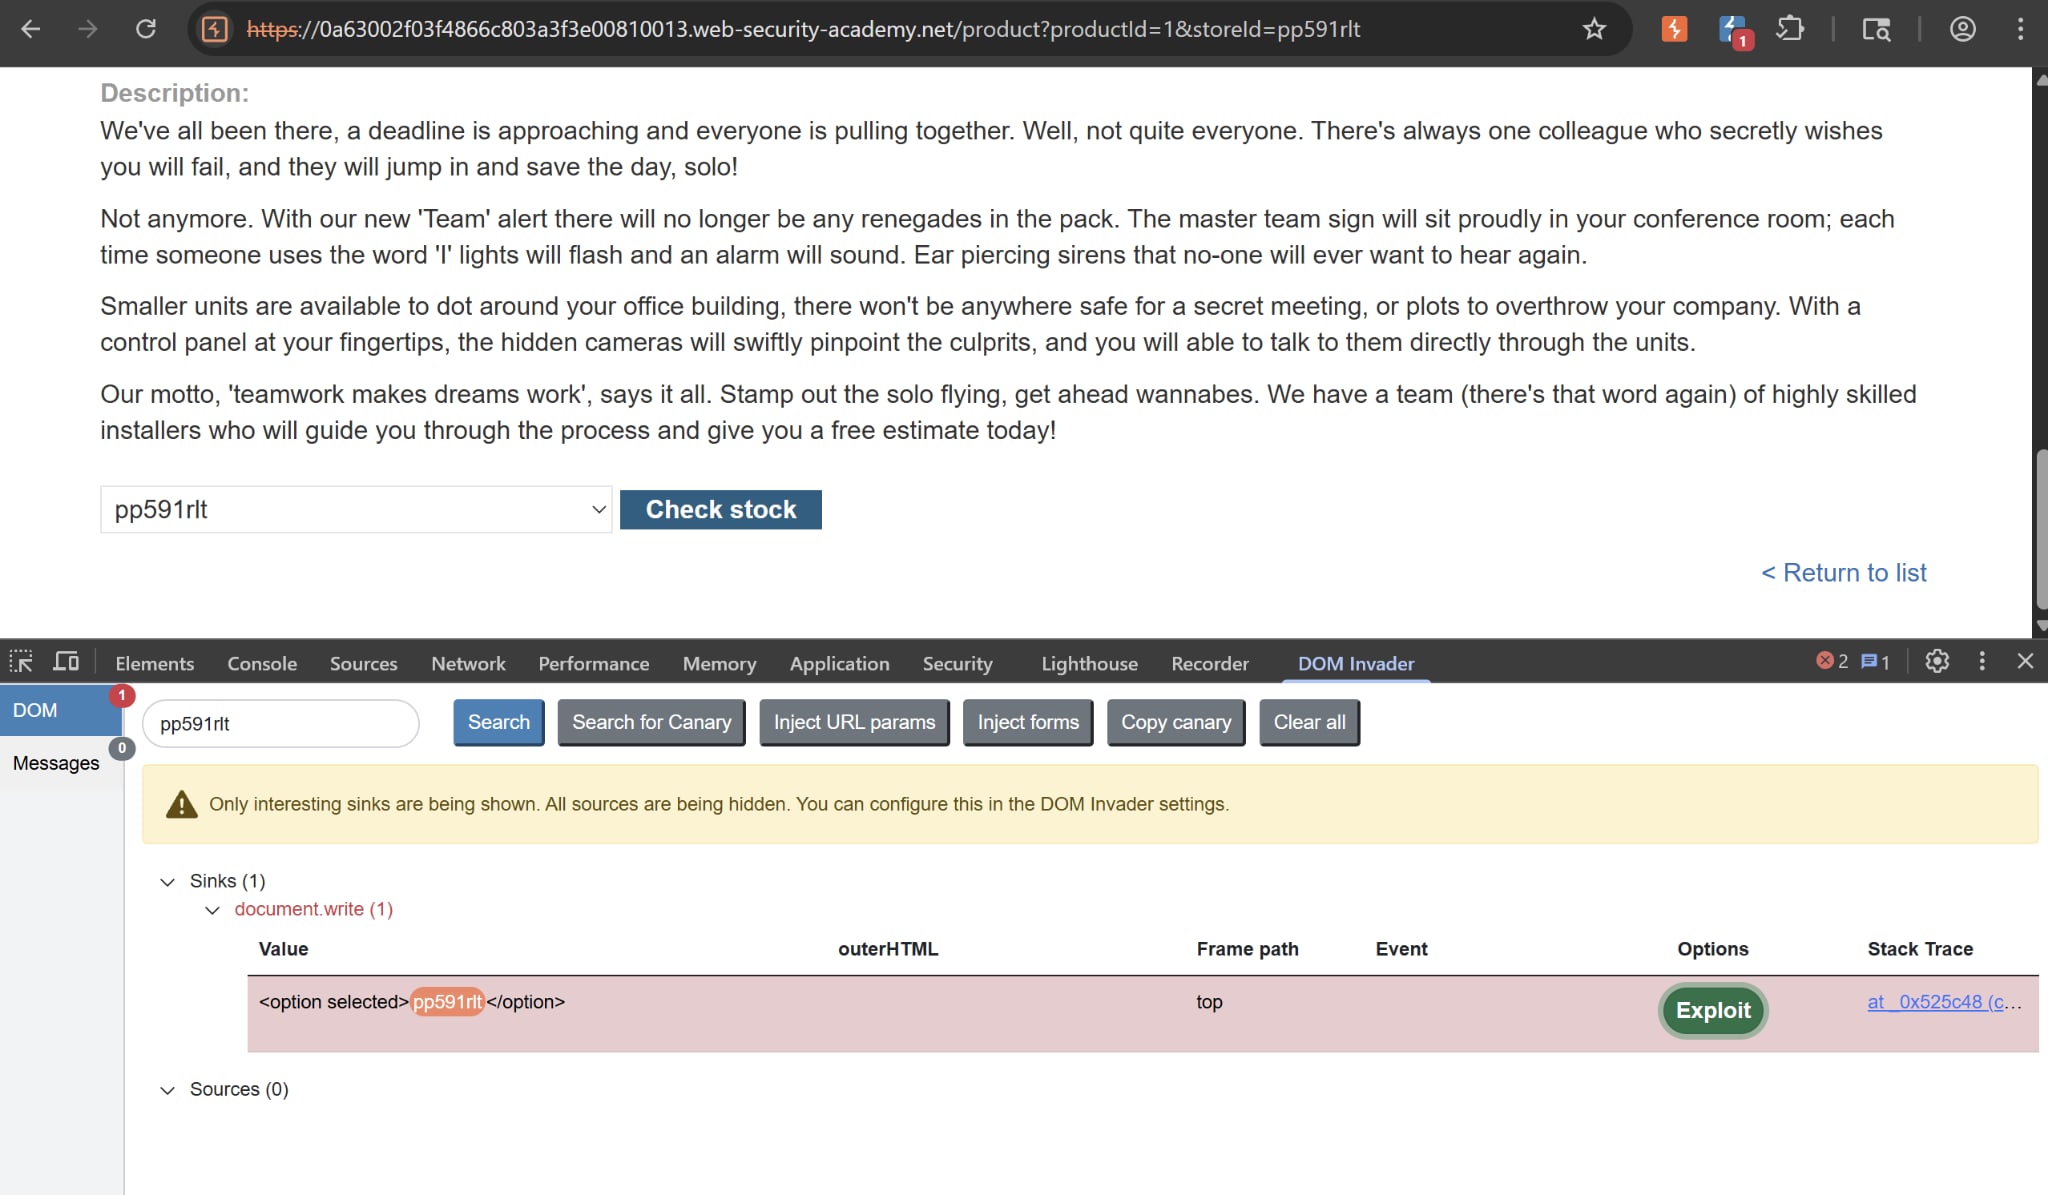
Upon attaching a storeId query param into the URL, the DOM Invader captures our random string present within the HTML, and confirming that the sink in question is indeed document.write():
We can then simply set storeId=<script>alert(1)</script> and it works fine, but weirdly this lab requires us to get out of the select element. To solve this, we prepend </select> at the beginning of our payload.