DOM XSS in document.write sink using source location.search | Apprentice
This is quite a straightforward lab, but I want to emphasize on the use of Burp Browser’s DOM Invader.
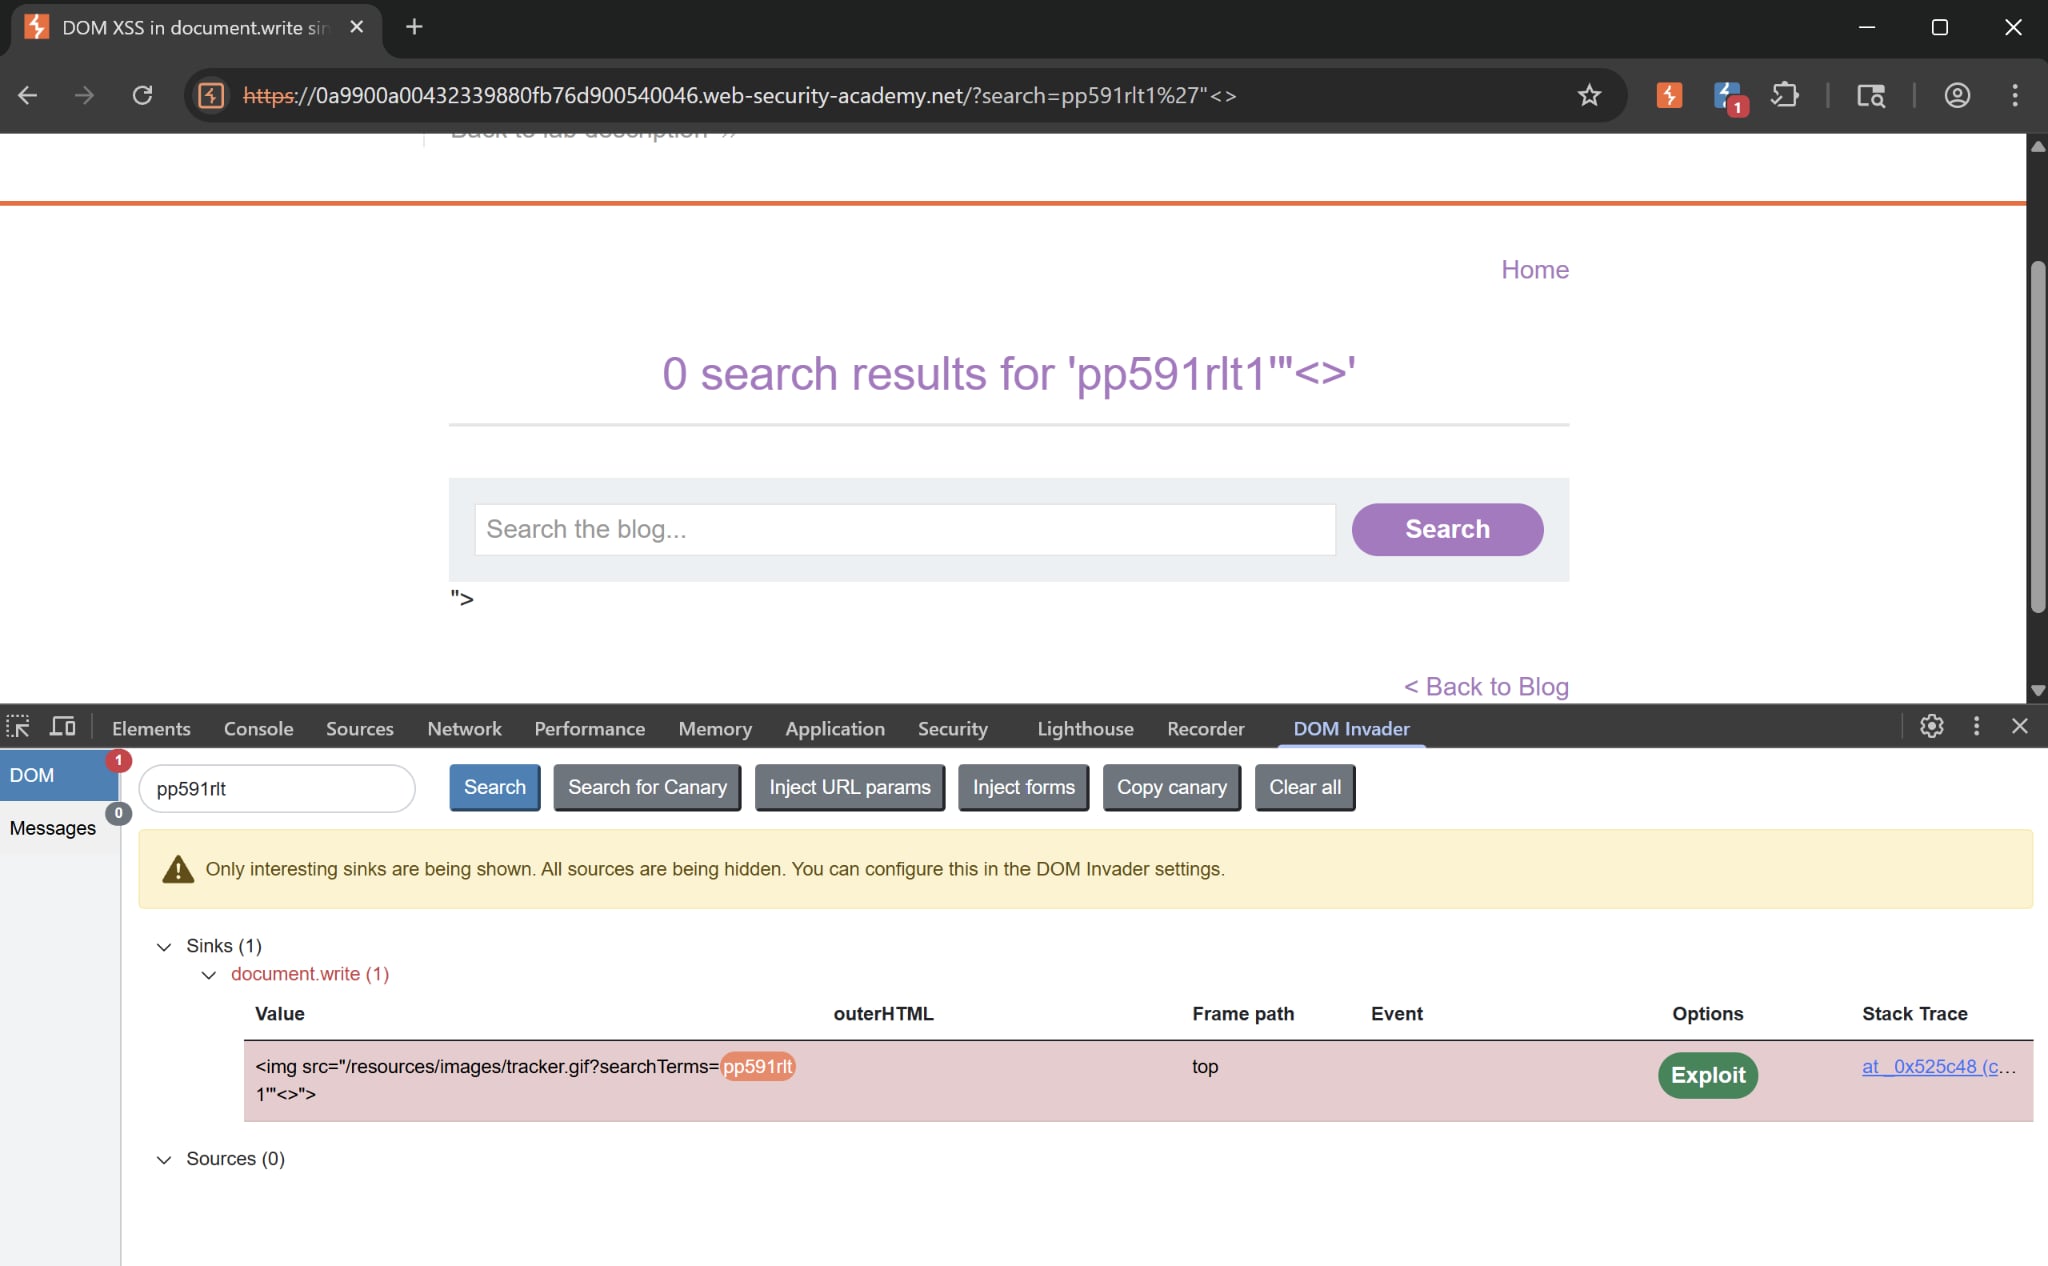
The “canary” here is pp591rlt, which is an unpredictable and uncommon string that we can inject into different sources to see which sinks they flow into. Included in the string are special characters ", <, and >. This helps test whether the browser will sanitize the quotes and brackets or not.
In this example, we find out that the canary flowed into the document.write (1) sink, which is an HTML sink as it directly modifies HTML in the page. The “Value” column shows where our payload has landed in the code. Essentially, the JS code is trying to do this:
document.write('<img src="/resources/images/tracker.gif?searchTerms=' + your_search + '">');
The special characters are not sanitized, that’s why "> appear as stray text as shown. That means we can craft an XSS payload without being filtered by the backend. Click on the “Exploit” button to send out a simple alert() payload.