Exploiting clickjacking vulnerability to trigger DOM-based XSS | Practitioner
As the lab’s name suggests, there exists a DOM-XSS vulnerability somewhere in the application. Naturally, we should crawl through the site and see where does a vulnerable DOM sink lives. The feedback form is looking a bit fishy so let’s check that out!
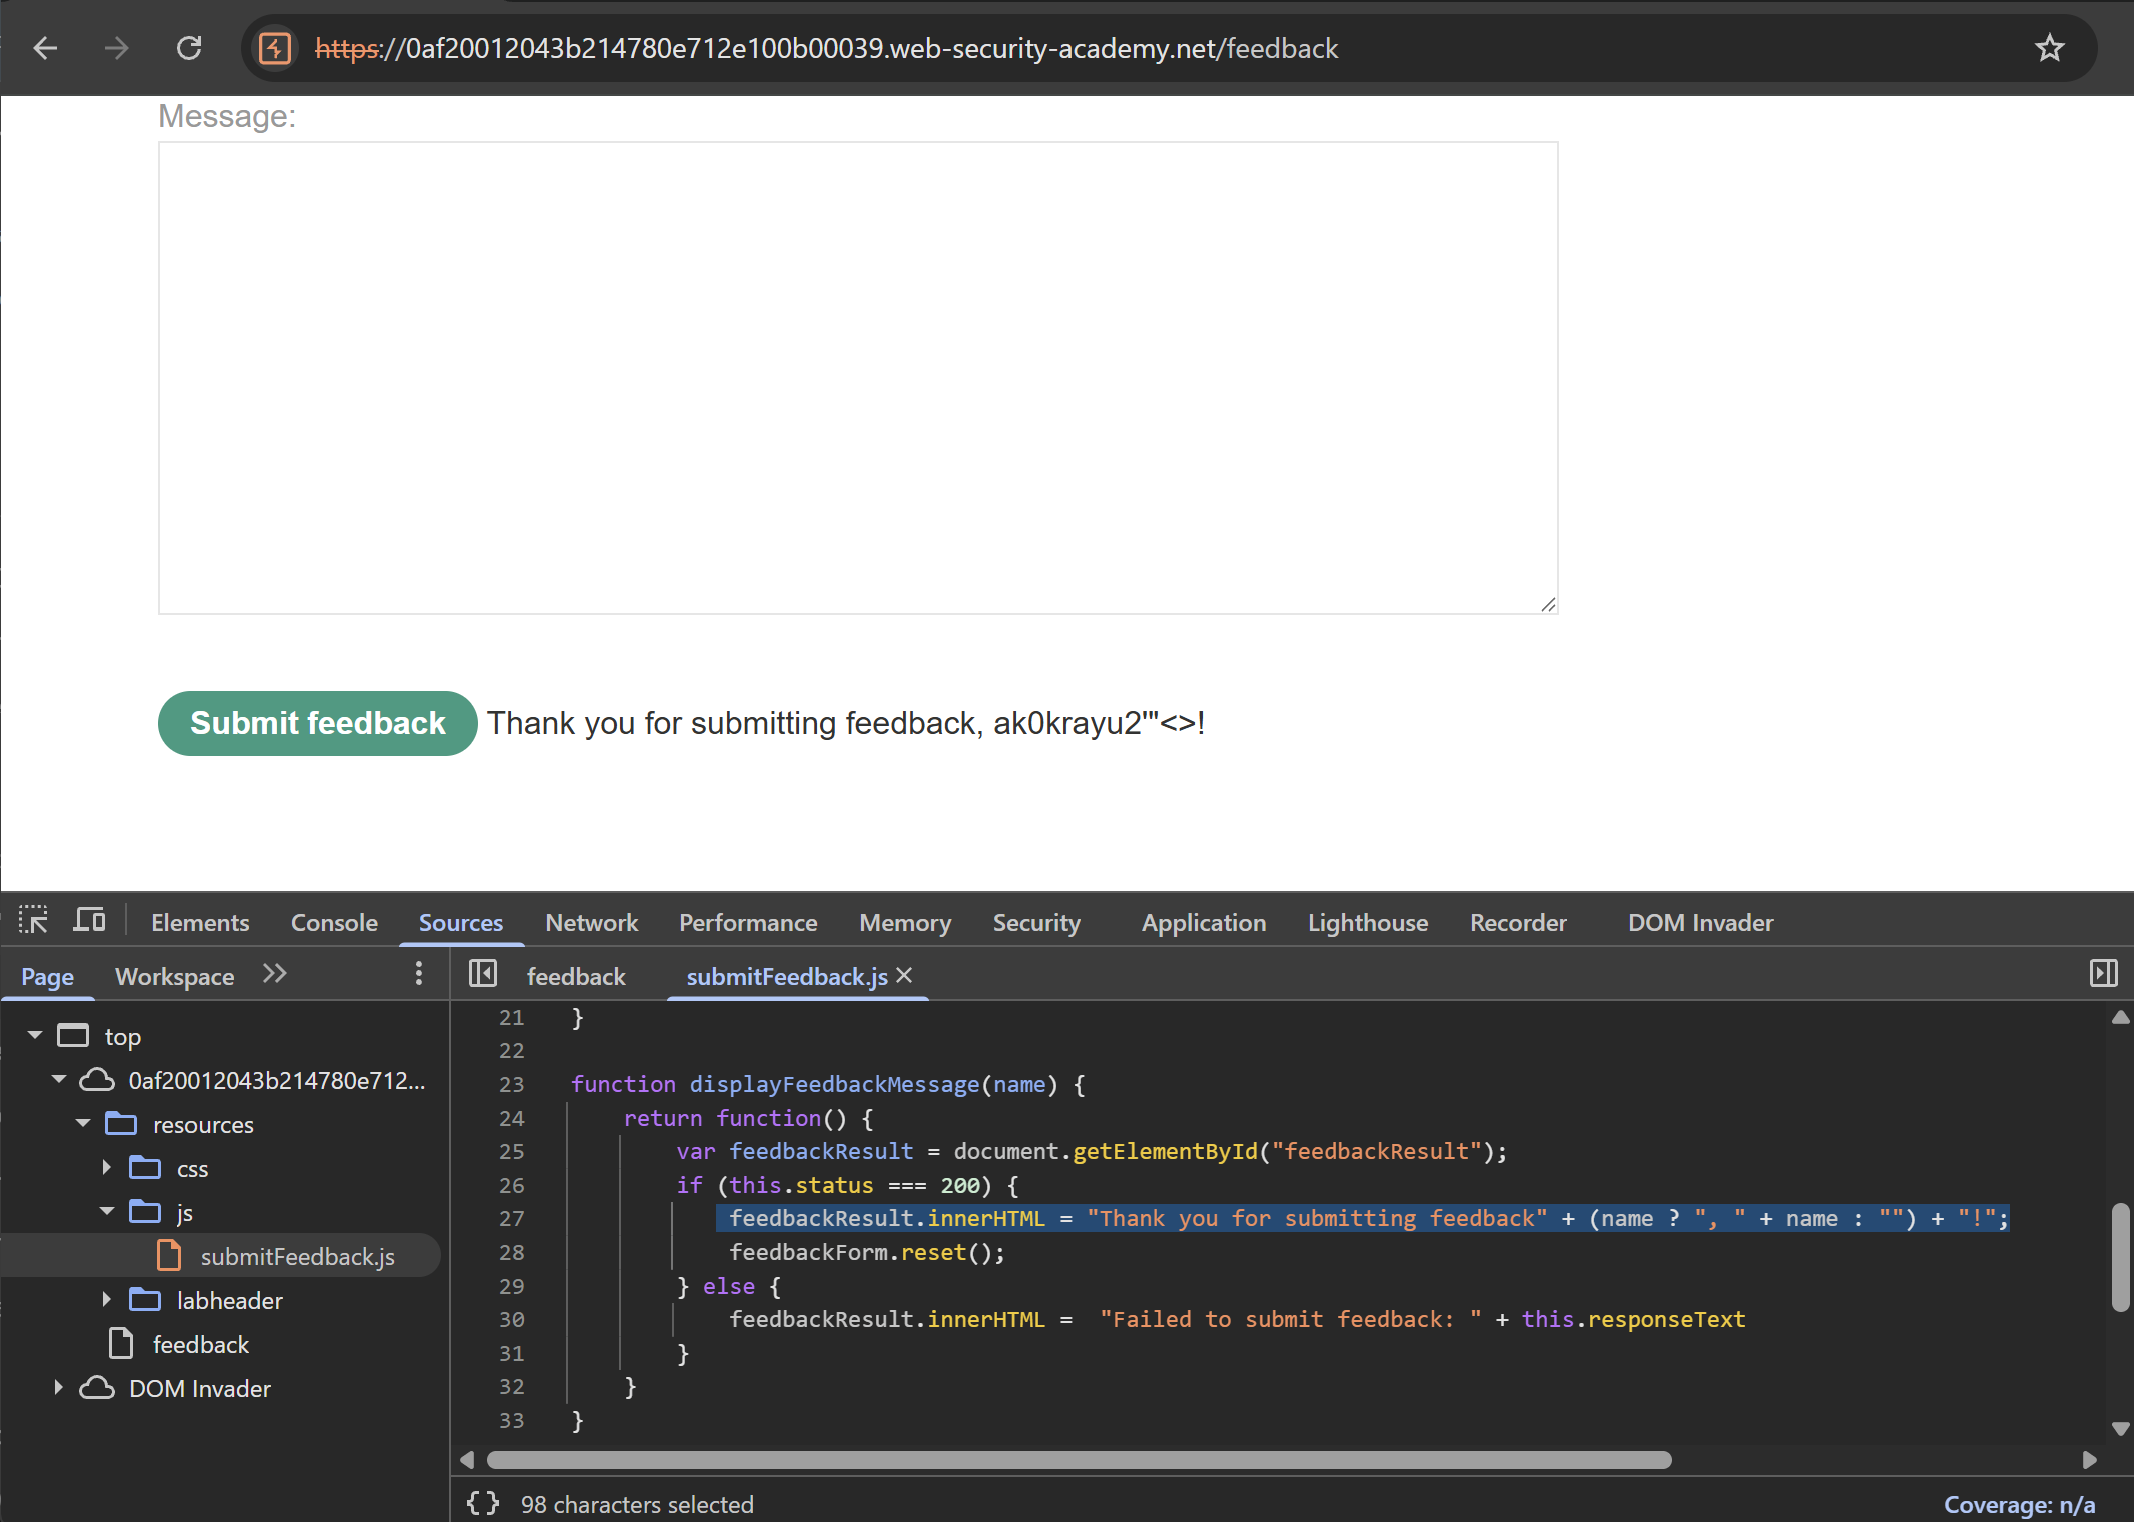 Looks like our intuition is correct! Whatever passed into the
name field will be reflected in the innerHTML sink after submission. And it looks like the application doesn’t filter out angle brackets or quotes, which makes constructing XSS payloads much easier. Let’s test this out by injecting a harmless h1:
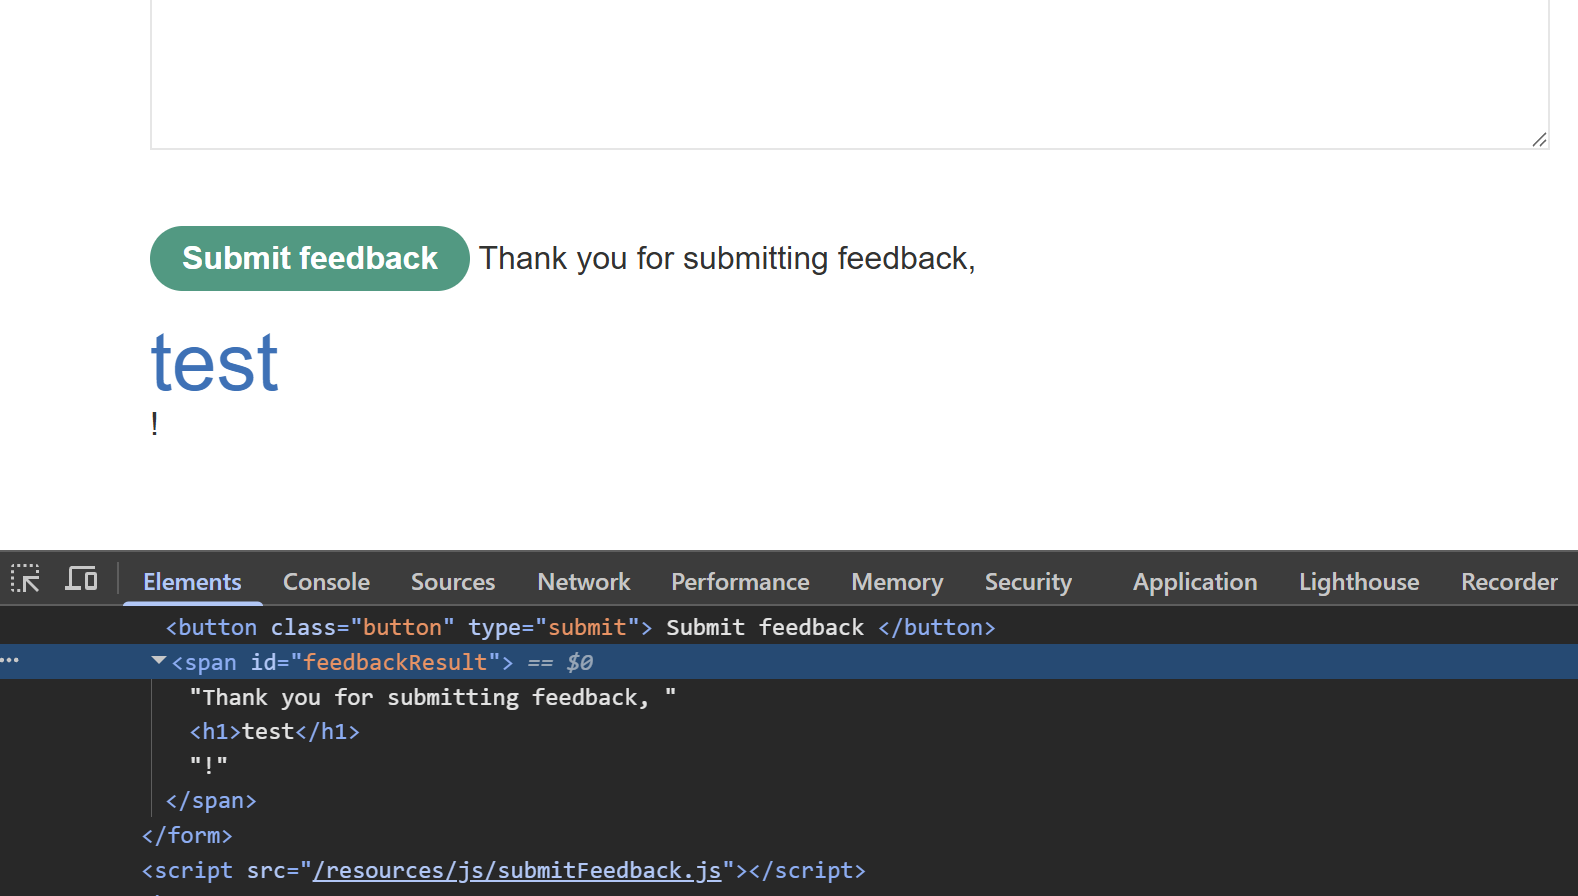 The parser indeed recognises this as valid HTML, and display it proudly. Since our sink is
innerHTML, we have to use img or iframe to fire our events. Testing with the <img src=1 onerror=print()> payload will do its job as told.
Since the lab has no authentication, we can safely assume that one does not need to verify his cookies to send feedbacks. But just to be safe, we should check whether the session cookie has SameSite set to None or not, and it looks like it does:
 With all these in mind, we can use Burp Clickbandit to set up a quick PoC and solve the lab!