Clickjacking with a frame buster script | Apprentice
First of all, in order for a clickjacking attempt that changes victim’s states to work, anything that requires cookie auth must have that cookie set SameSite=None. Thankfully, this is indeed the case for this lab:
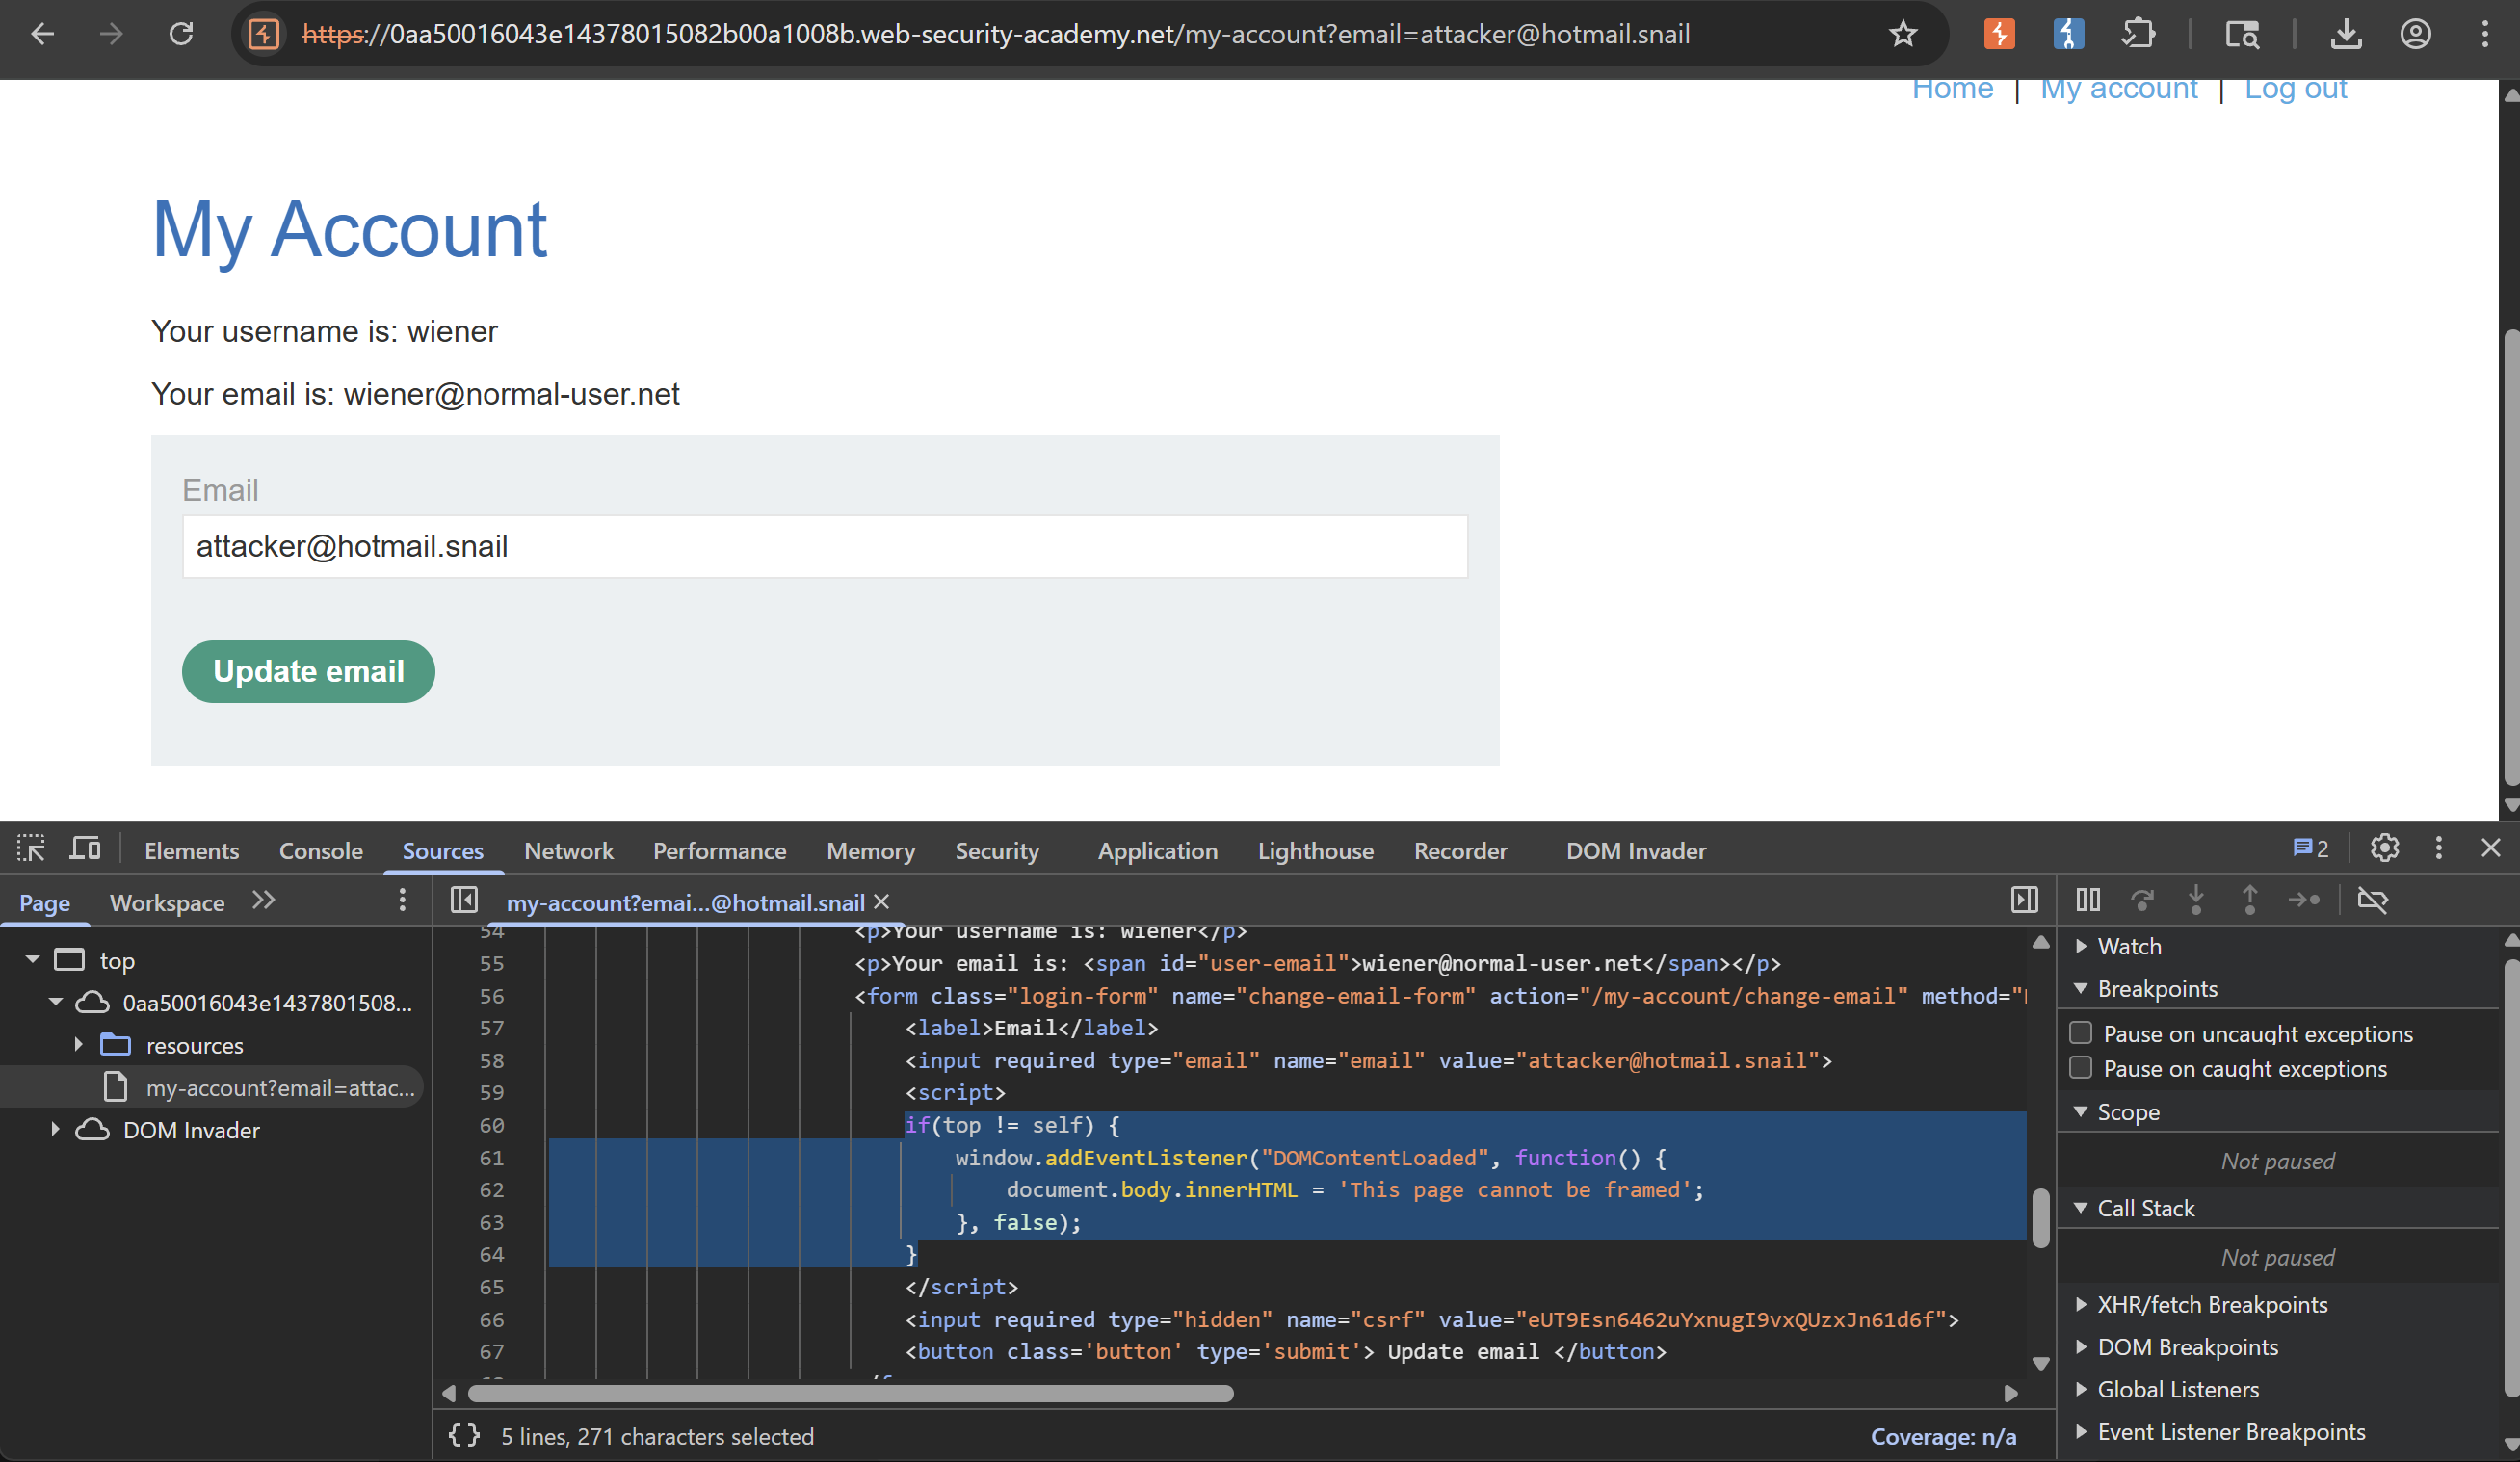
 Upon checking the source code, we can see that the developer tries to prevent clickjacking by adding a frame busting script as shown here. What this does is that it checks if the top-most window is the same as the current window. If they are different, it means the page is inside an iframe and the attempt is blocked:
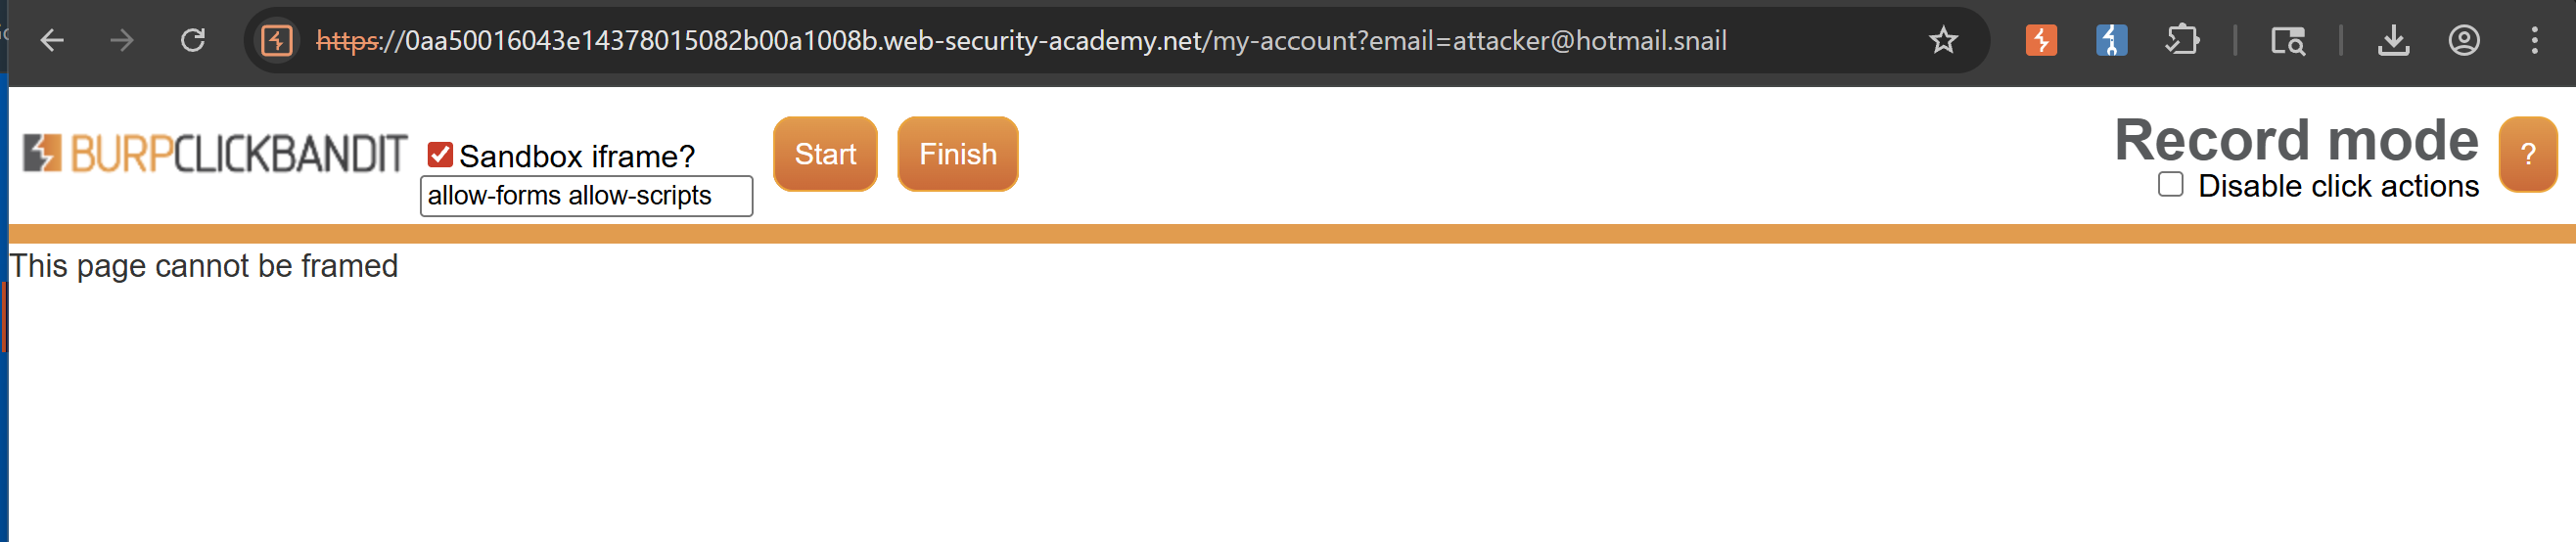
 If we try to use Burp Clickbandit, notice that the attempt to frame the site is blocked:
 To solve this, we should also strip
allow-scripts so that the framed page’s JavaScript will be blocked. allow-forms is still kept because we need a form to change emails with (lol)
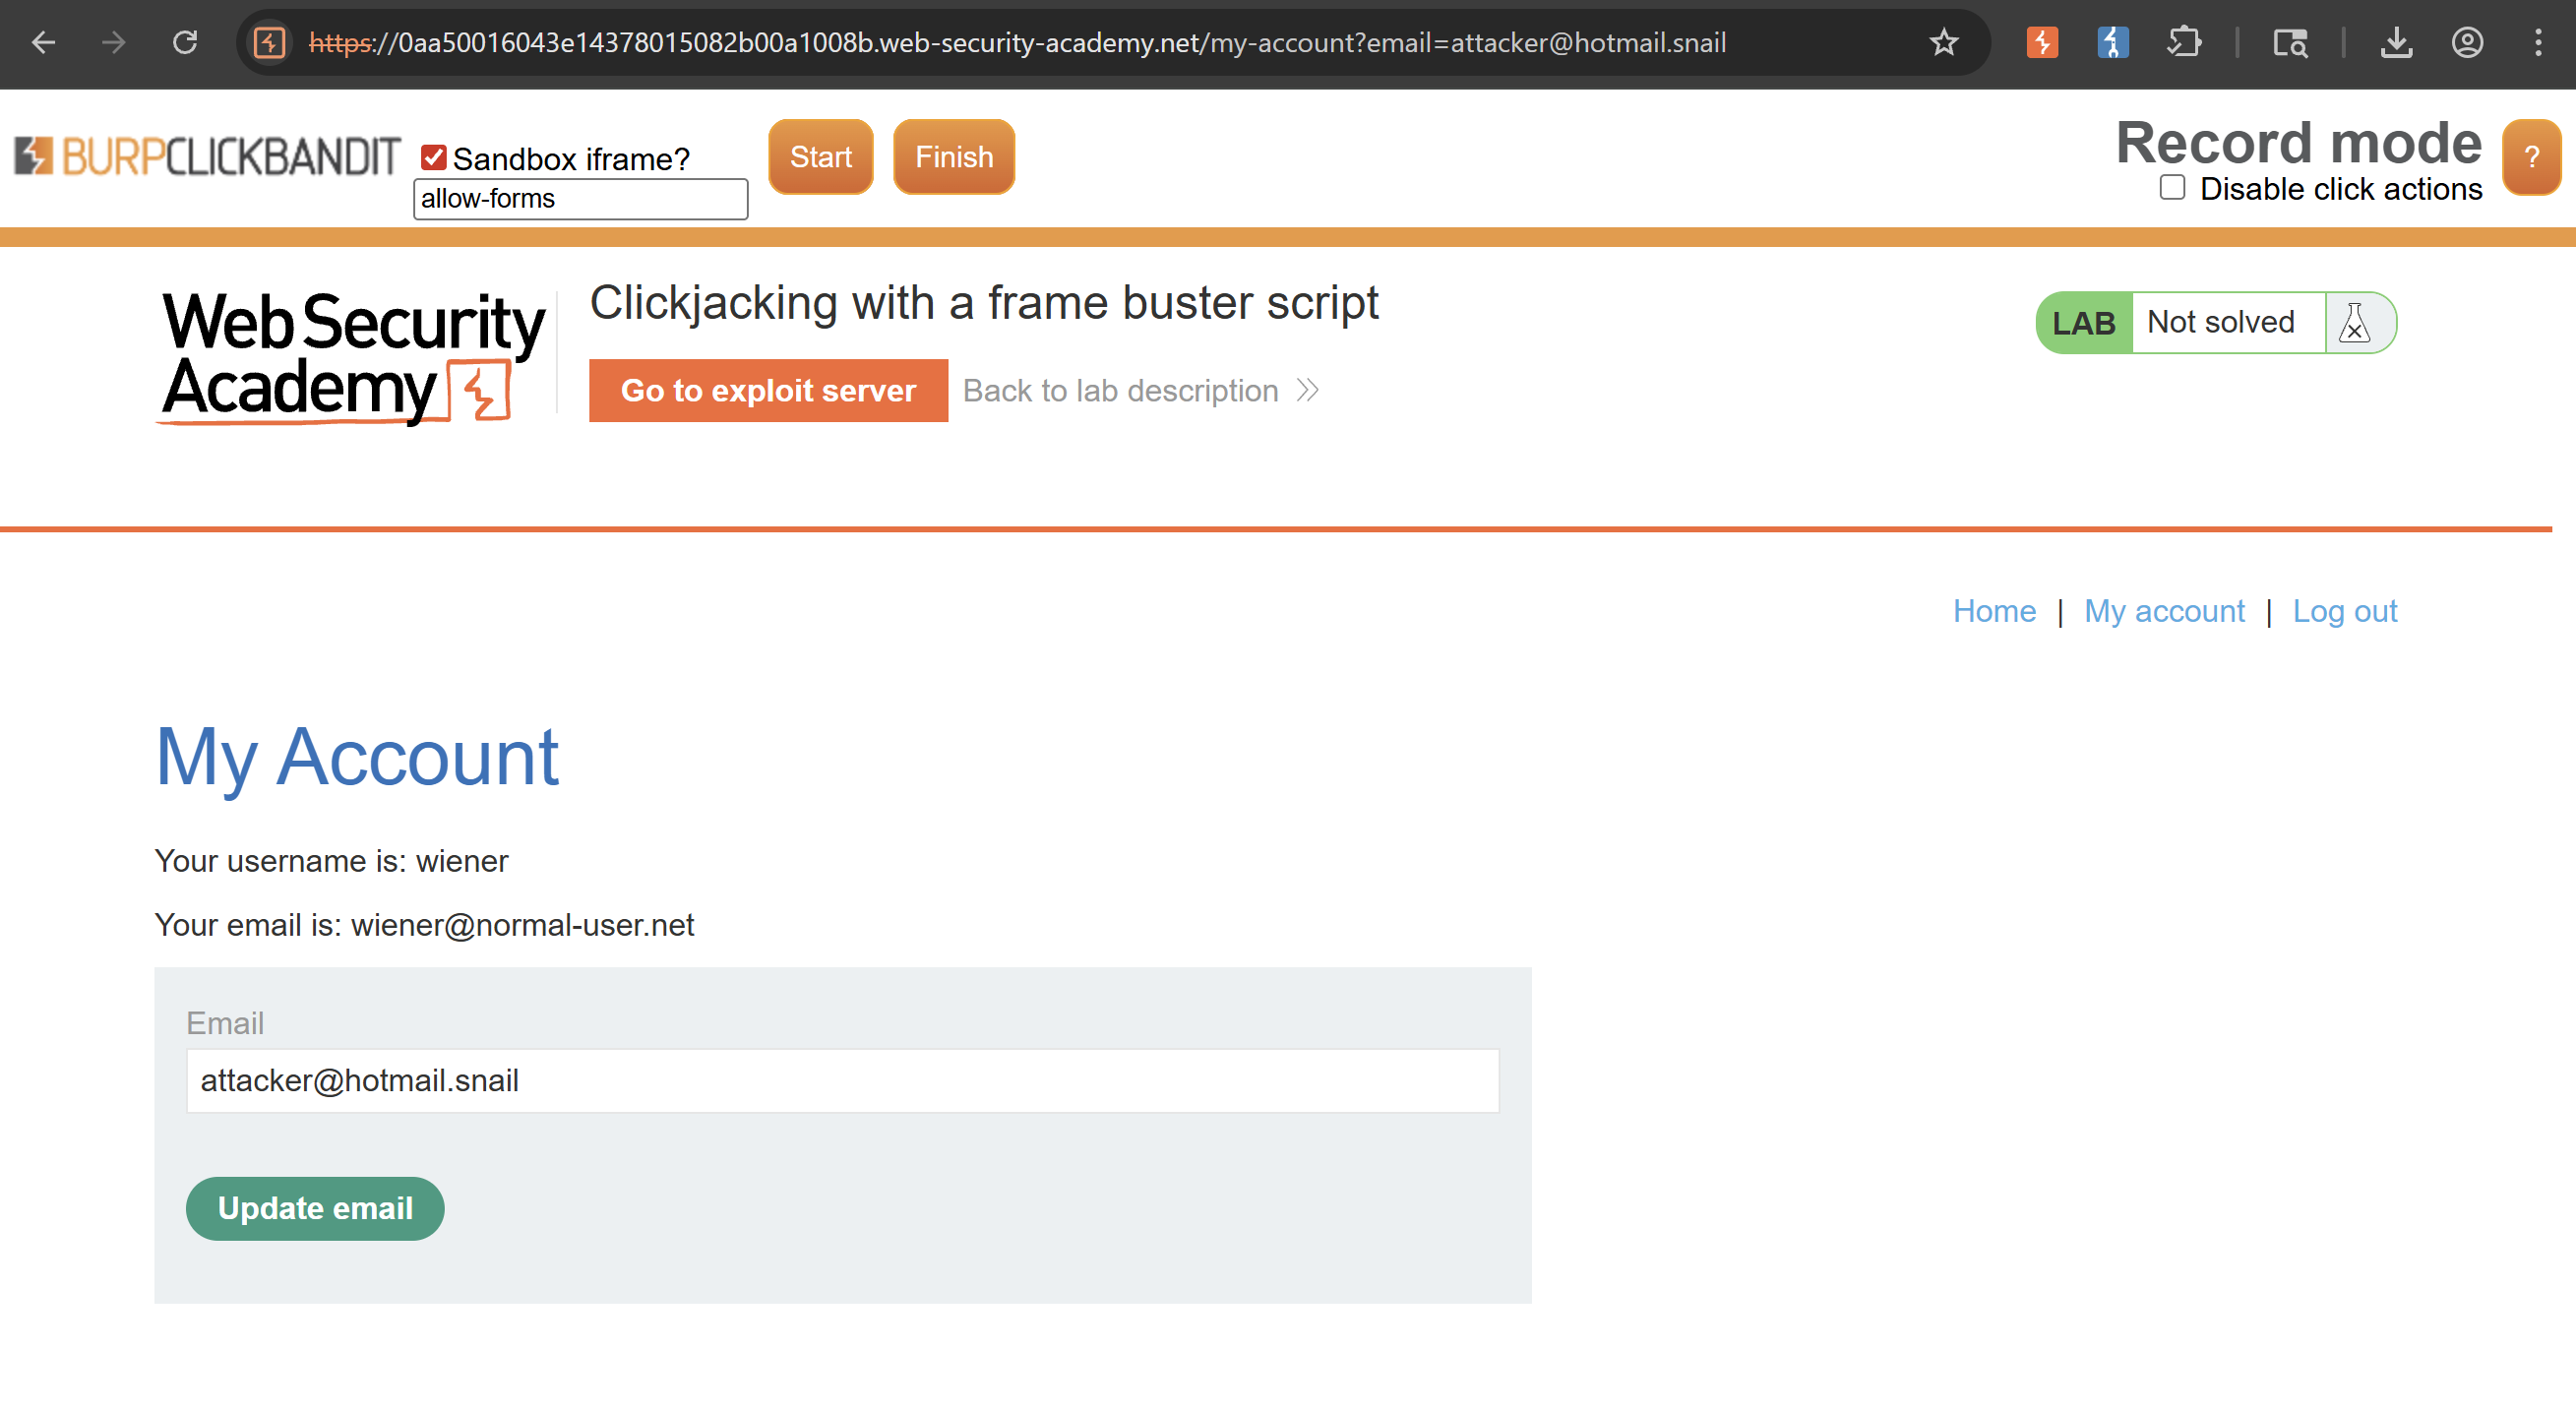 After that, use Clickbandit to generate a sample PoC and deliver it to the victim. Neat