Username enumeration via different responses | Apprentice
Using the provided username and password wordlists, my initial solution is to simply run a cluster bomb attack in Intruder to test all permutations possible. But on the Community version this took an excruciatingly long time because of the rate limit.
Another way to do this is to perform a sniper attack to enumerate only the valid usernames first, and from there we have a much shorter list of usernames to check their passwords.
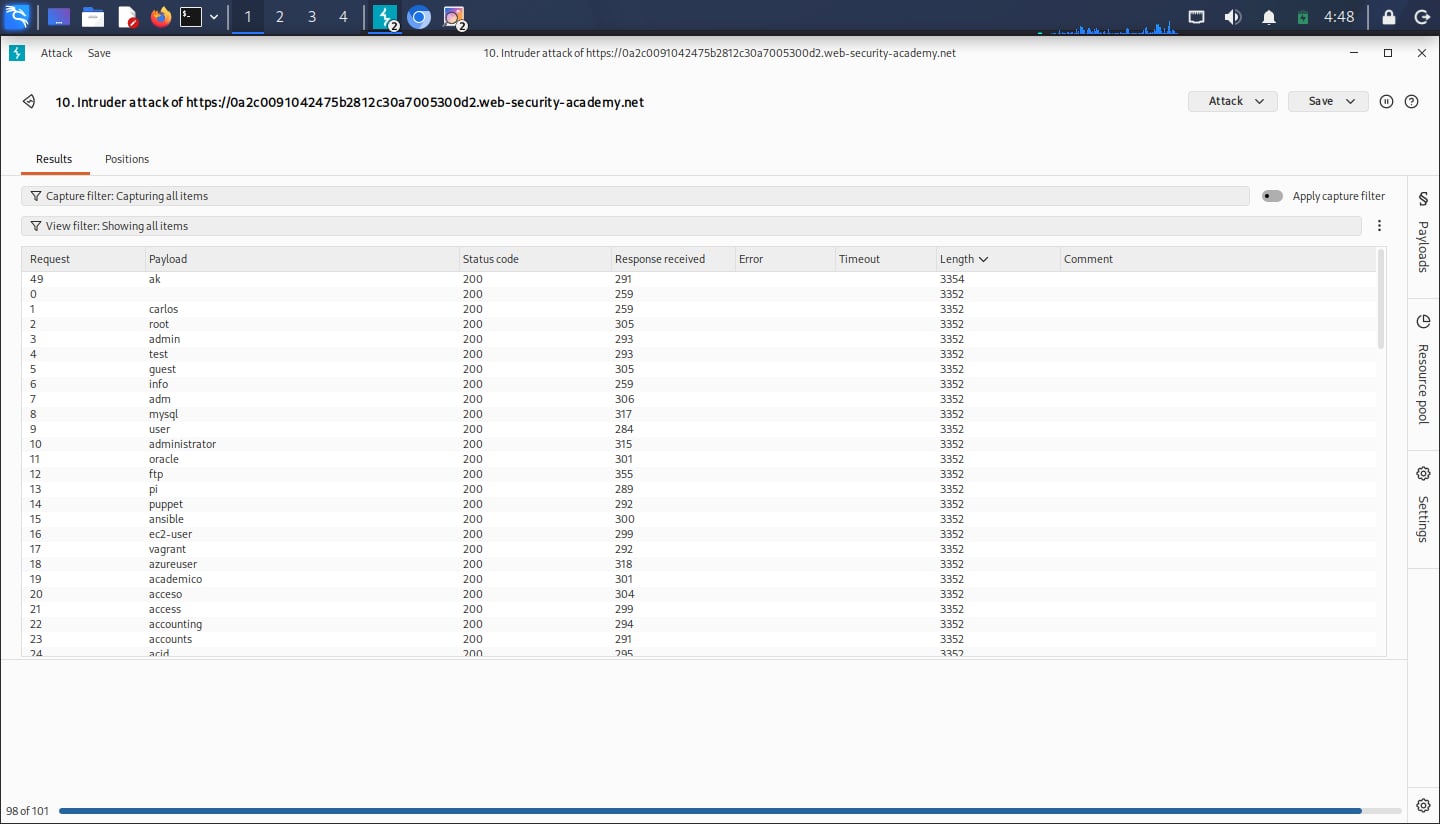
Notice that ak has a slightly longer length than the rest, we can confirm this is the only valid username by typing into the login form.
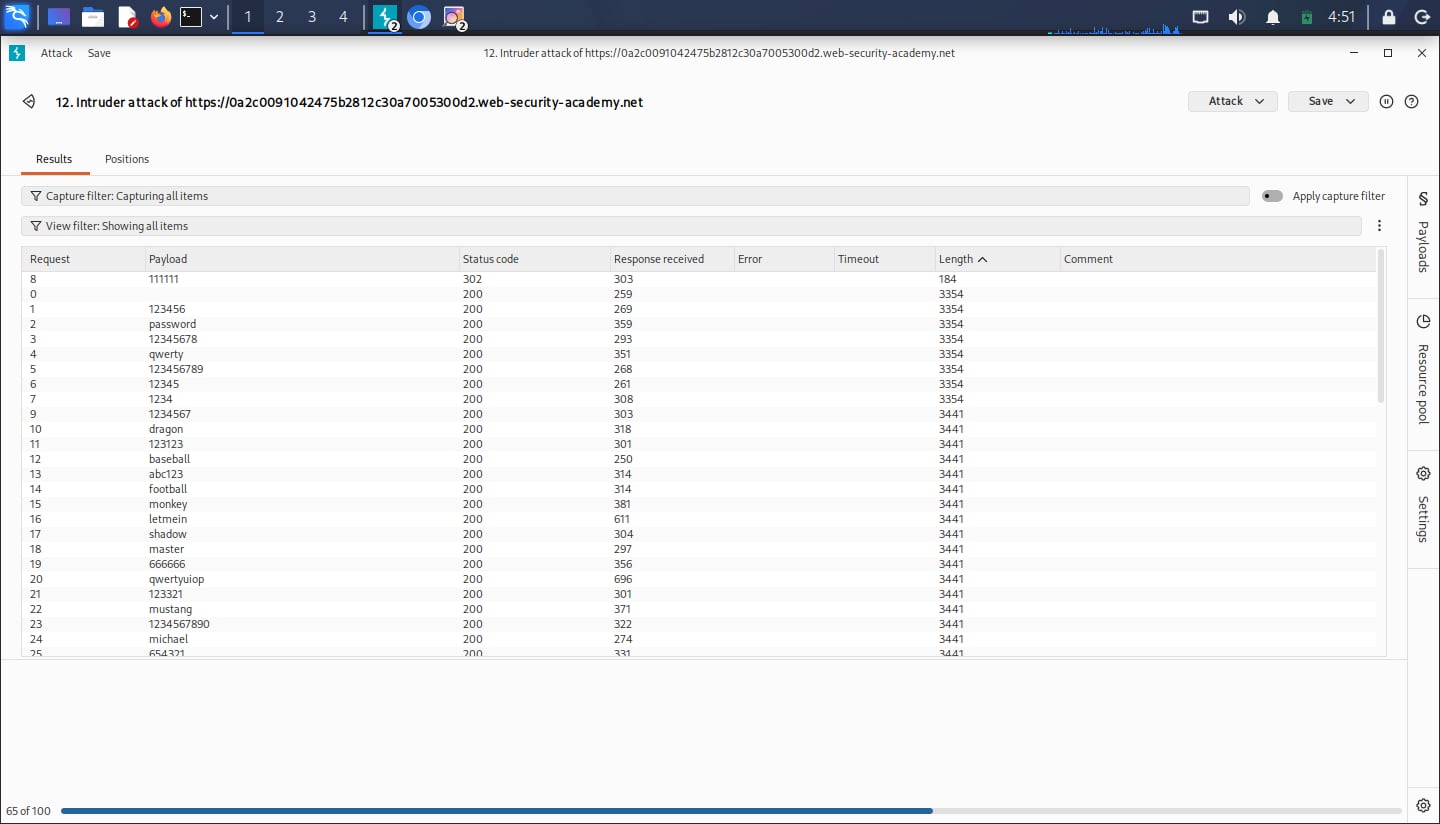
111111 has a significantly shorter length than the rest, and it is indeed our password for ak. Very fun problem.