User role can be modified in user profile | Apprentice
At first, I keep digging session cookies and HTML source to see whether they contain any references of roleid or not, and I stumped. I realised that I hadn’t even attempted to change my email to see what happens yet.
So, upon changing our email, we can observe that the response has a JSON object that keeps tab of our username, email, and roleid:
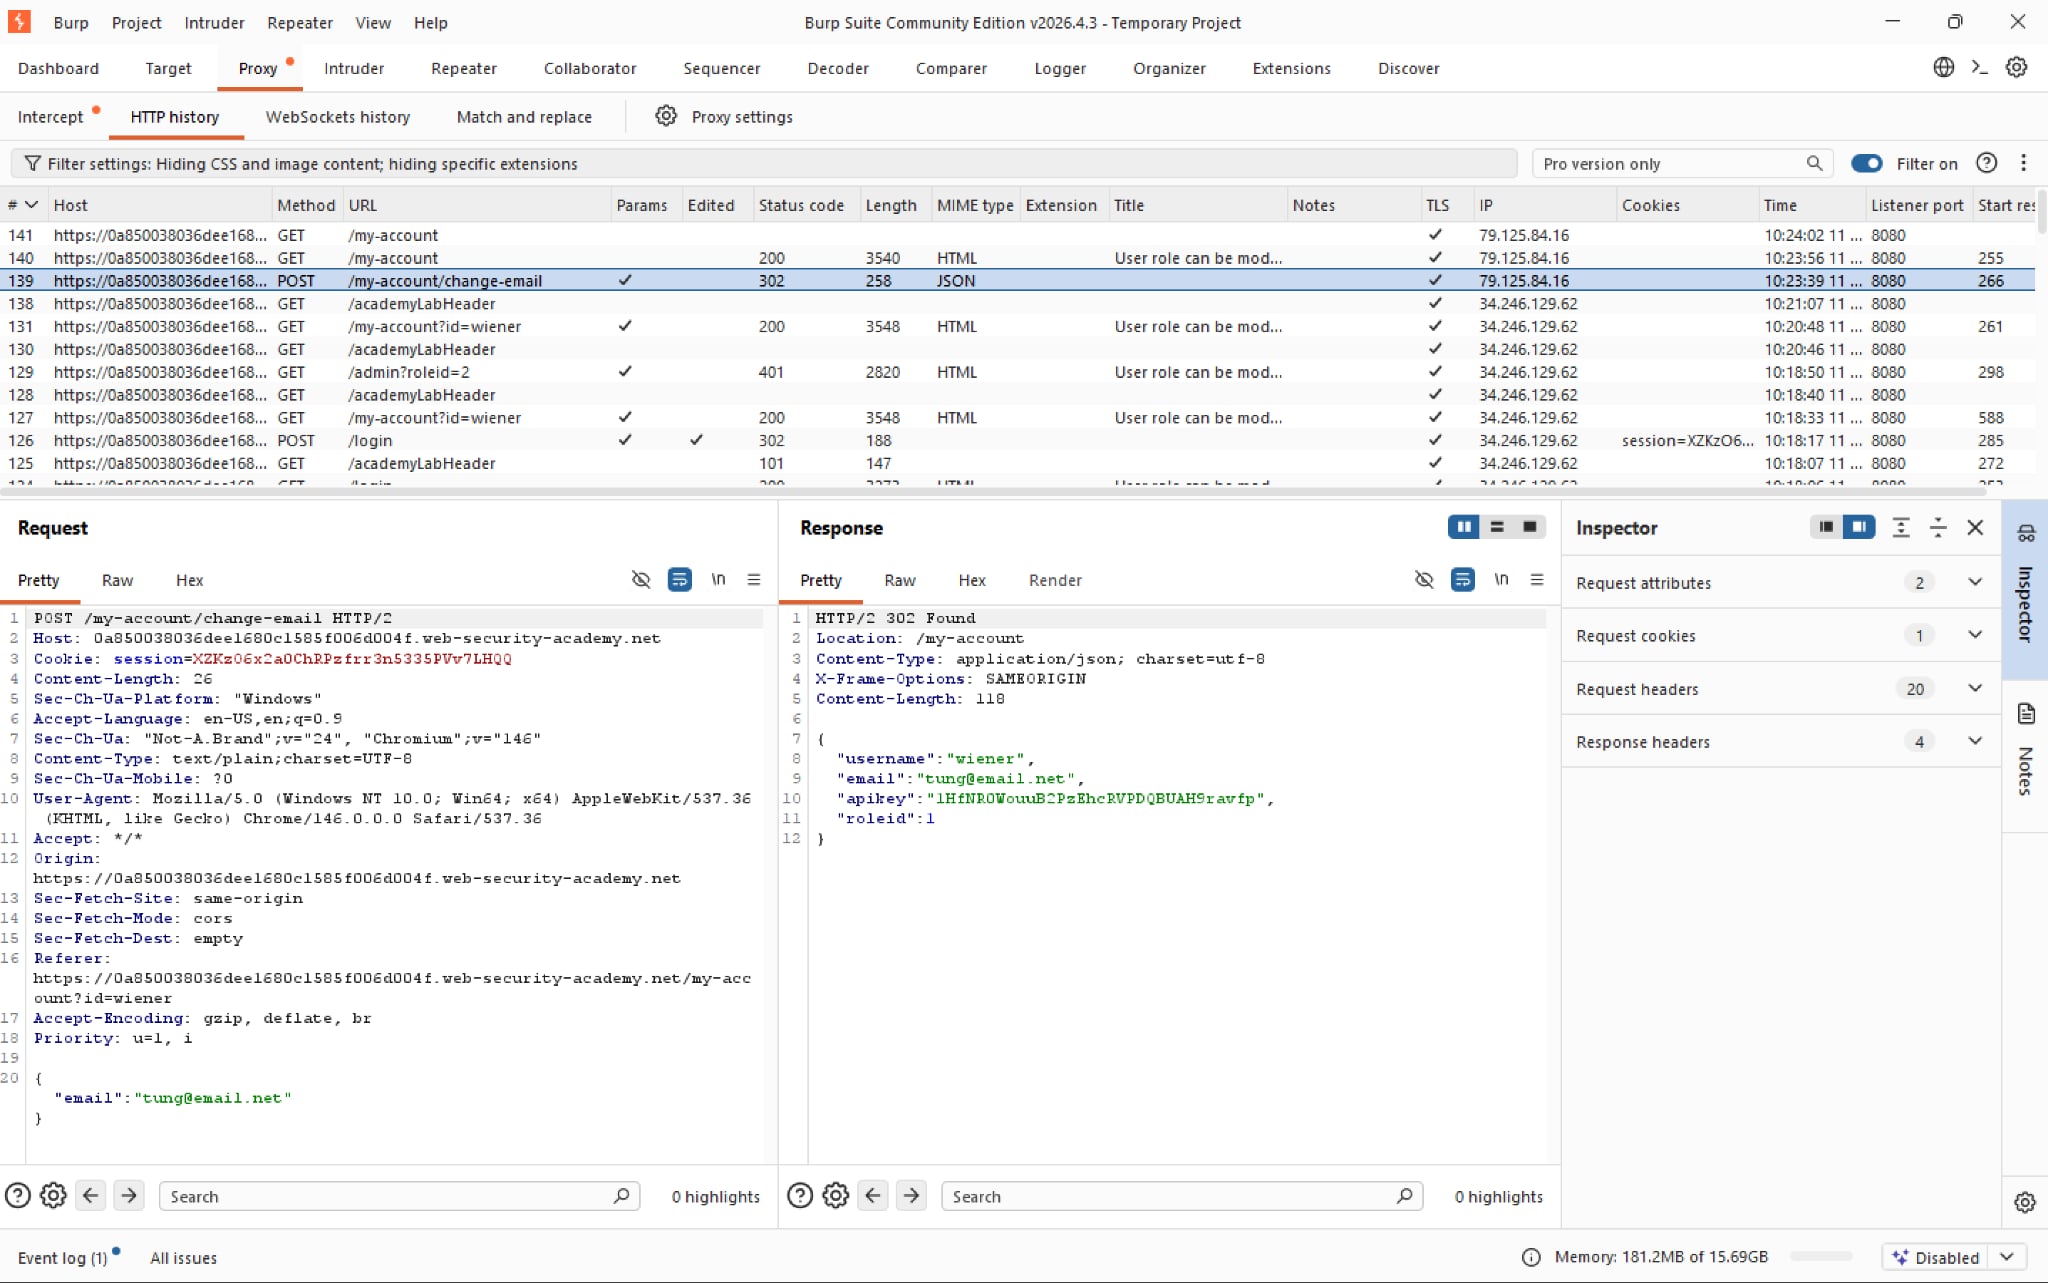 Simply add
"roleid":2 into the request body and voila we will get access to the admin panel. This is a vuln called Mass Assignment