Unprotected admin functionality with unpredictable URL | Apprentice
Very straightforward, the lab introduces a vuln where sensitive endpoints are exposed in plaintext, in this case some JS scripts:
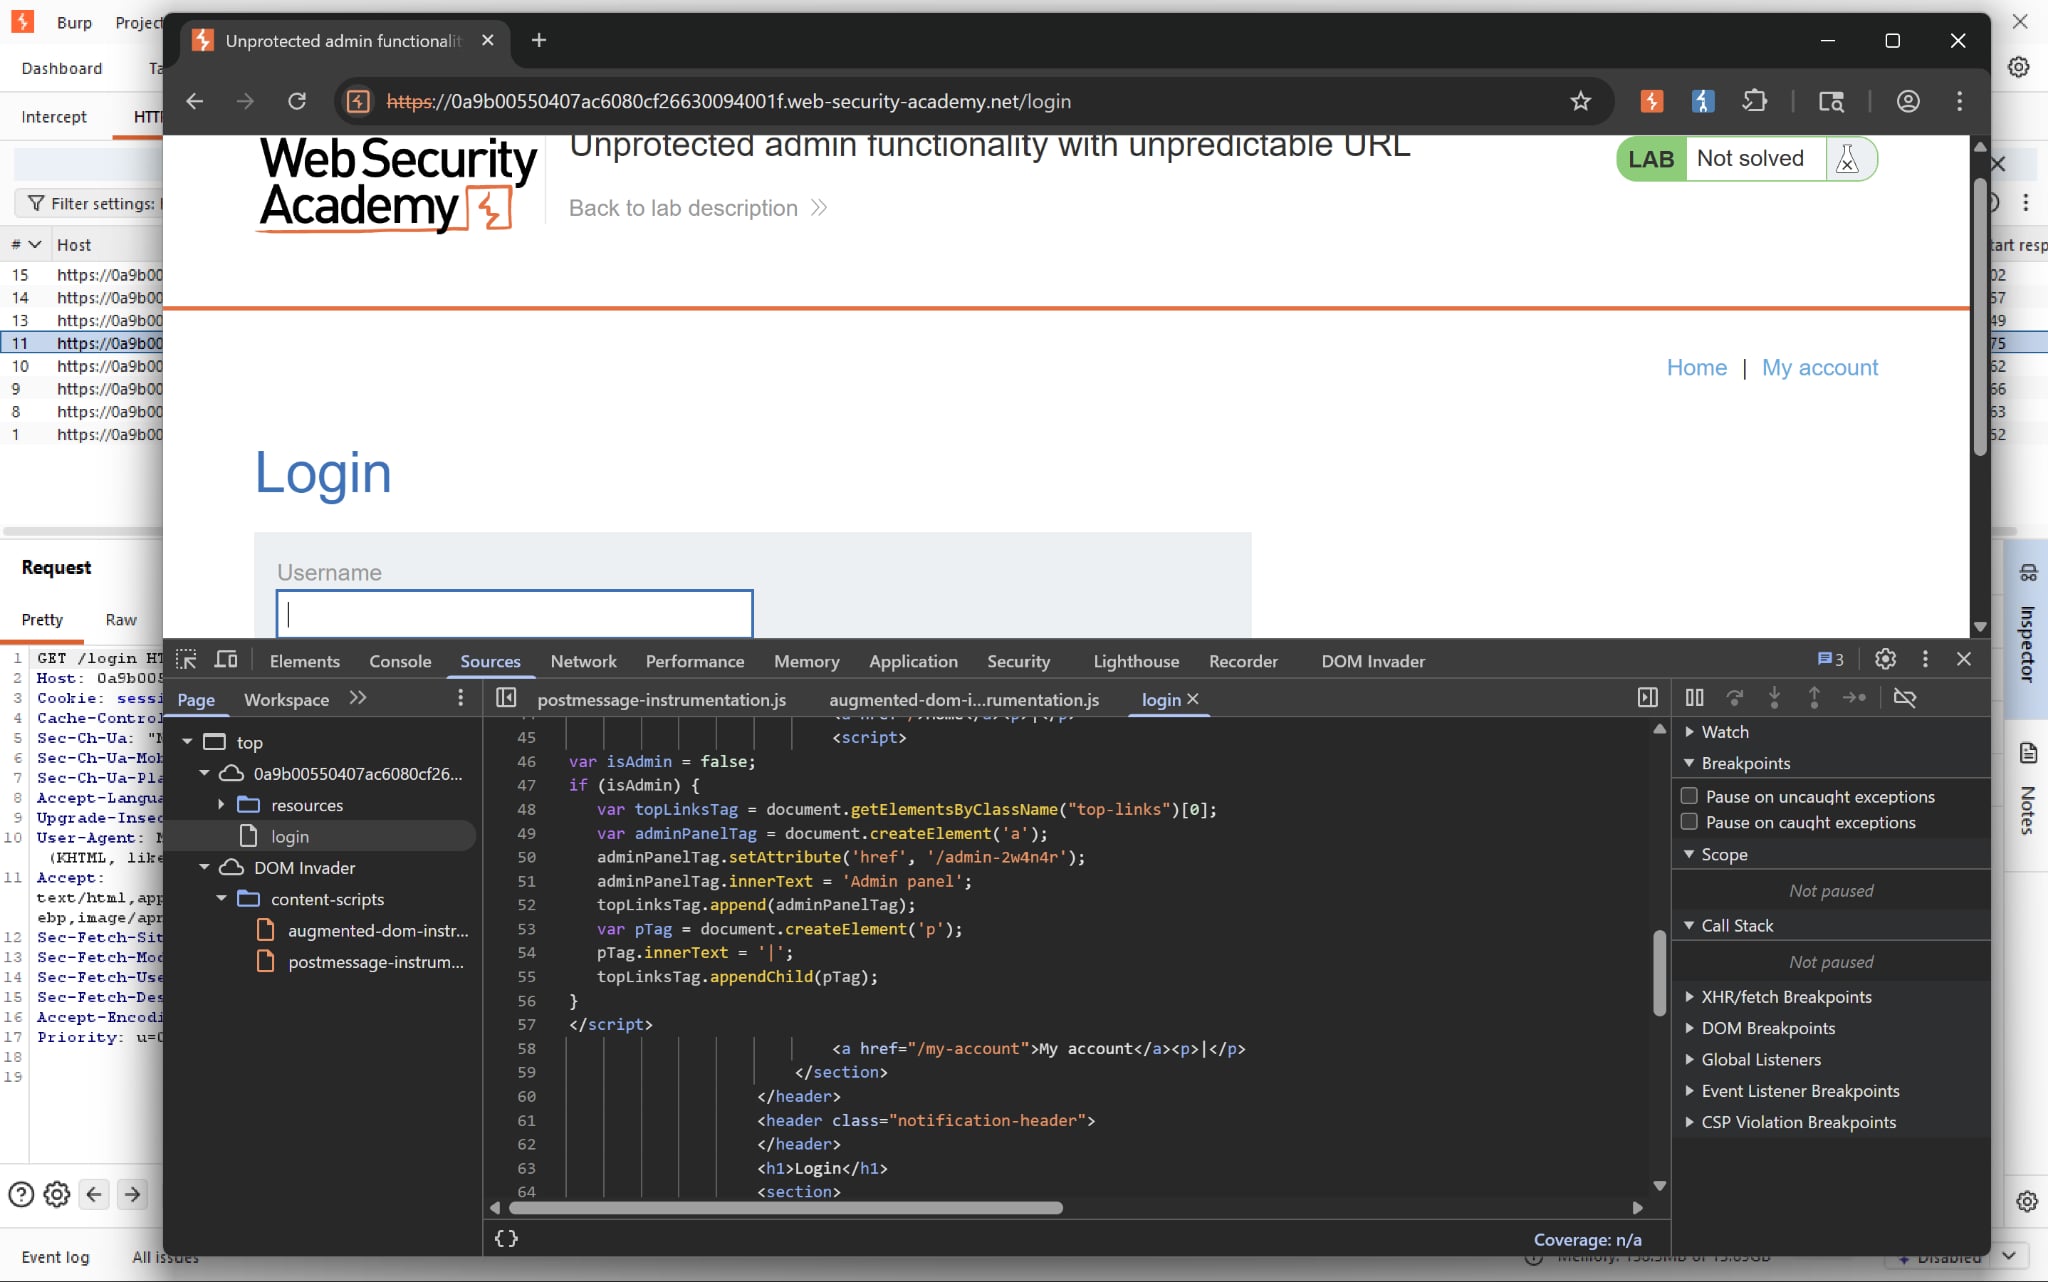 Simply access the hidden endpoint and we can solve the lab.